
ISO 27701 Certification in Angola
Quick Answer
ISO 27701 certification is an internationally recognized Privacy Information Management System credential, extending ISO 27001 specifically to how you manage personal data as a controller or processor. In Angola it’s voluntary, requires ISO 27001 as its foundation, typically takes two to four months if you’re already ISO 27001 certified, and gives you structured, auditable evidence of Law 22/11 compliance specifically around personal data handling, not just general information security.
About ISO 27701
ISO 27701 is a privacy extension to ISO 27001, adding requirements specific to managing personally identifiable information, whether your organization acts as a controller, deciding why and how data is processed, a processor, handling data on someone else’s behalf, or both. It doesn’t replace ISO 27001; it builds directly on top of it.
Certification means an independent, accredited certification body has audited your actual privacy controls alongside your existing information security system, and confirmed they genuinely meet the standard’s requirements. It’s reissued on a three-year cycle with annual surveillance audits in between, aligned with your ISO 27001 cycle.
A brief history of the standard : ISO 27701 was published in August 2019, developed specifically in response to the global wave of new privacy regulation that followed the EU’s GDPR in 2018, when organizations worldwide needed a way to demonstrate systematic privacy management beyond general information security. Rather than creating an entirely separate management system, ISO deliberately built it as an extension to the already widely adopted ISO 27001, reducing duplication for organizations that had already invested in information security certification.
Why It Matters in Angola?
Angola’s data protection law creates specific obligations around personal data that general information security doesn’t fully address. Law 22/11 and APD oversight cover how personal data is collected, used, and protected, questions ISO 27001 alone doesn’t dedicate specific structure to answering. ISO 27701 adds that structure: defined roles for controllers and processors, data subject rights handling, and privacy-specific risk assessment.
What not having this specific layer actually costs you : Organizations with only ISO 27001 certification can demonstrate strong general security but struggle to show a systematic approach to privacy-specific questions, like how data subject access requests are handled or how consent is tracked, that increasingly come up in Law 22/11-related scrutiny or partner due diligence.
Why is this becoming more relevant in Angola now? As banks, telecoms, and fintechs already pursuing ISO 27001 certification handle growing volumes of personal data, more are being asked by partners and regulators specifically about privacy management, not just general security, making this a natural next step rather than a separate project.
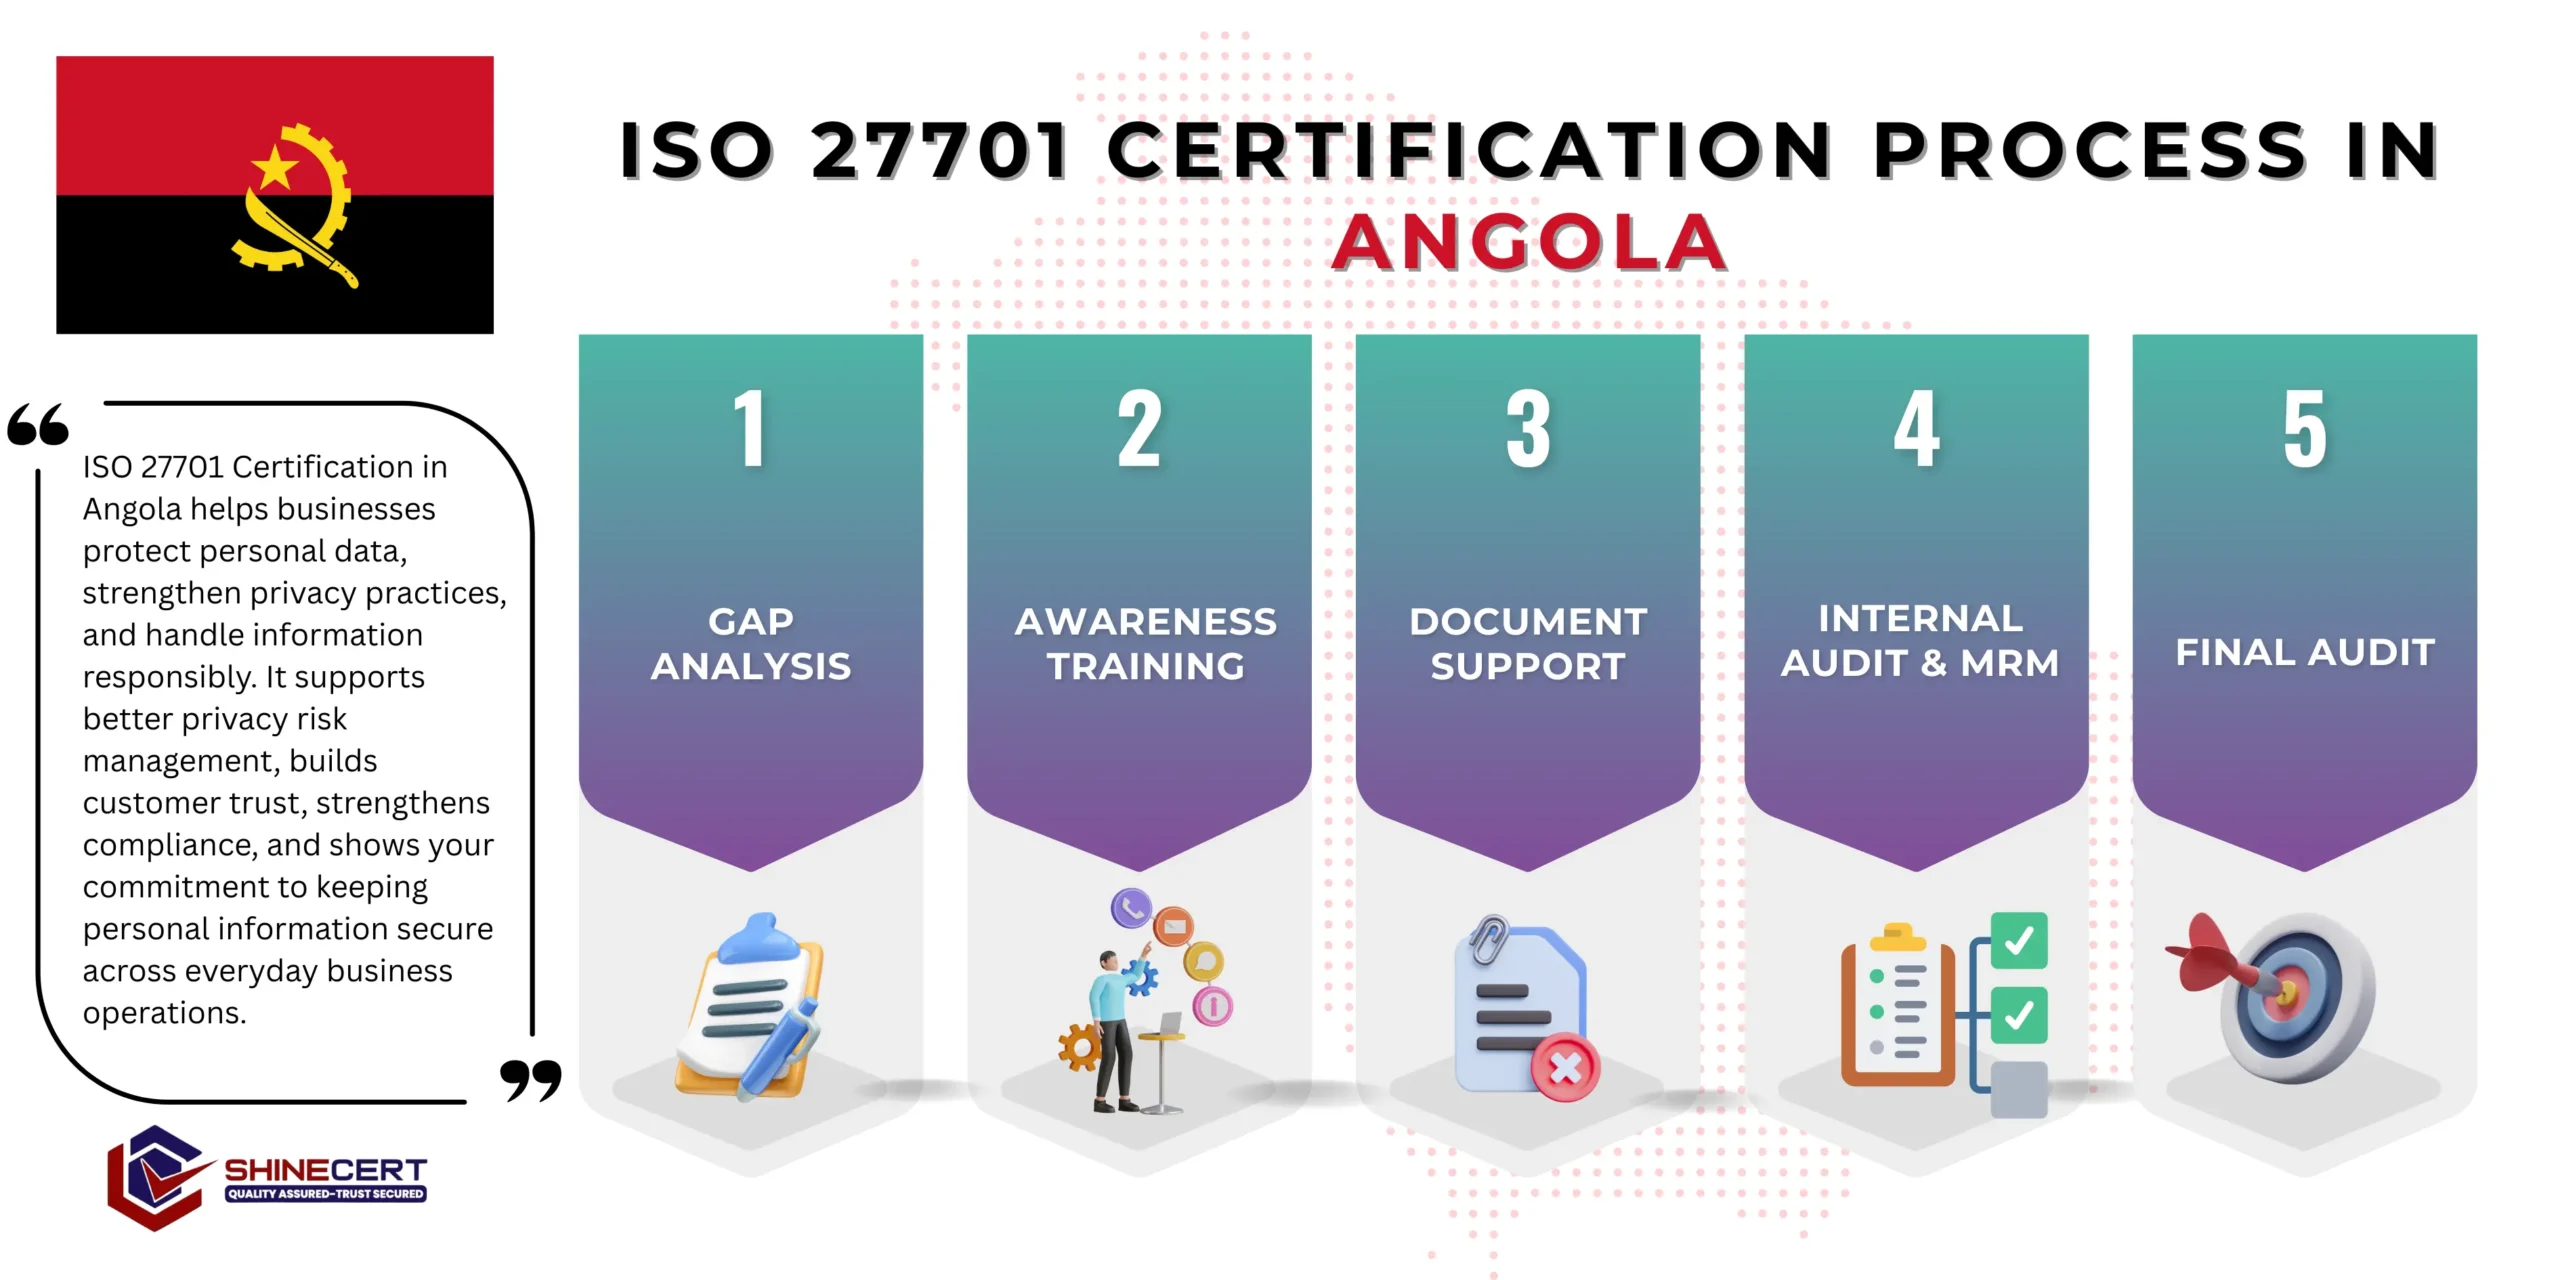
What are the steps to get ISO 27701 Certification in Angola?
our services
- ISO Certification Angola
- ISO 9001 Certification Angola
- ISO 14001 Certification Angola
- ISO 27001 Certification Angola
- ISO 22000 Certification Angola
- ISO 20000-1 Certification Angola
- ISO 45001 Certification Angola
- ISO 42001 Certification Angola
- ISO 13485 Certification Angola
- ISO 17025 Certification Angola
- ISO 31000 Certification Angola
- ISO 22301 Certification Angola
- ISO 27701 Certification Angola
- ISO 37001 Certification Angola
- ISO 50001 Certification Angola
- CE Mark Certification Angola
- GMP Certification Angola
- GDPR Certification Angola
- Halal Certification Angola
The Certification Process
Privacy Gap Mapping
Over one to two weeks, we compare your current privacy practices, often informal, against the standard's requirements, working from your existing ISO 27001 documentation as the foundation rather than starting from zero. Why this matters: this stage typically moves faster than a standalone ISO 27001 gap assessment, since your information security context is already documented.
Controller-Processor Determination
Over one to two weeks, we formally define whether you're acting as a controller, processor, or both for each significant data processing activity, a distinction many organizations have never explicitly documented despite it shaping their legal obligations. You walk away with clarity on exactly which privacy obligations apply to which of your activities.
Privacy Documentation Build
Over two to four weeks, we build data subject rights handling procedures, consent tracking documentation, and privacy-specific risk assessments layered onto your existing ISO 27001 risk register. Why this matters: this is where the standard's genuinely new requirements, beyond general information security, take concrete shape.
Rollout and Verification
Over two to three weeks, privacy procedures go live and relevant staff, particularly customer service and legal, are trained on handling data subject requests properly. You walk away with a functioning privacy system your team can actually operate, not just a document.
Extension Audit
Over one to two weeks, your certification body audits the privacy extension specifically, often alongside a scheduled ISO 27001 surveillance audit, and issues the ISO 27701 certification once satisfied.
How Long Does Certification Take?
| Organization Status | Typical Timeline | Why |
|---|---|---|
| Already ISO 27001 certified | 2–3 months | Foundation already exists; only privacy-specific work needed |
| Pursuing ISO 27001 and 27701 together | 4–6 months | Both systems built simultaneously from scratch |
| Complex data processing (banking, telecom) | 5–6 months | Extensive controller-processor relationships to document |
- Organizations already ISO 27001 certified (2 to 3 months) : Since the information security foundation, risk assessment, documentation practices, staff training culture, already exists, the additional privacy-specific work moves considerably faster than a standalone certification project.
- Organizations pursuing both standards together (4 to 6 months) : Building the full ISO 27001 foundation and the privacy extension simultaneously takes meaningfully longer, since neither system has an existing base to build from.
- Organizations with complex data processing, including banks and telecoms (5 to 6 months) : These organizations typically have the most extensive network of controller and processor relationships, sometimes acting as both simultaneously across different services, which takes real time to document accurately.
- The variable that matters most: how clearly your organization already understands its controller and processor roles : Organizations that have never thought through this distinction, common even among otherwise security-mature businesses, need meaningfully more time in the early stages than those who’ve already mapped it informally.
- A real example : A bank we worked with, already ISO 27001 certified for three years, assumed the privacy extension would take a few weeks; the controller-processor determination stage alone took closer to five weeks, because the bank operated as a controller for its own customer data but as a processor for a partner insurance product, a distinction nobody internally had previously documented.
What Affects the Cost?
- Whether you’re already ISO 27001 certified : This is the single biggest cost driver, since the privacy extension is meaningfully cheaper than building both systems from scratch.
- Complexity of your controller and processor relationships : More data processing activities and partnerships mean more roles to formally document.
- Volume of data subject requests you expect to handle : Higher-volume consumer businesses need more robust request-handling procedures.
- Certification body fees, separate from consulting costs.
Answering the Objections Every Owner Has
- We already have ISO 27001, isn’t that enough? ISO 27001 covers information security broadly; ISO 27701 adds the privacy-specific structure, controller and processor roles, data subject rights, that increasingly matters for Law 22/11-related scrutiny specifically.
- Isn’t this just IT’s problem, like security? Privacy governance touches legal, customer service, and HR as much as IT, since data subject requests and consent tracking are rarely purely technical issues.
- We’re too small for this : If you’re already ISO 27001 certified, adding privacy scope is proportionate to your data processing activities, not your overall size.
- Can’t we extend our security policy ourselves? You can attempt it, but data subject rights handling and controller and processor role documentation are exactly what auditors scrutinize most closely, and informal extensions rarely hold up.
Benefits of ISO 27701 Certification
- Structured evidence of Law 22/11 compliance specific to personal data : Certification demonstrates privacy governance beyond what general information security certification covers.
- Clear controller and processor role definition : The standard requires clarity on which role you occupy for each data processing activity, reducing ambiguity that often surfaces during a dispute.
- Systematic handling of data subject rights : A documented process for access, correction, and deletion requests, increasingly expected by regulators and privacy-conscious customers.
- Faster path to certification if already ISO 27001 certified : Since the standard builds directly on your existing system, the additional work is meaningfully less than starting from scratch.
- Stronger trust with privacy-conscious partners and customers : Certification is a credible, independently verified signal in a market where privacy expectations are rising alongside data protection awareness.
- A foundation for pursuing ISO 42001 alongside privacy governance : These standards share complementary risk and governance structures.
Required Documentation
The scope statement defines which data processing activities and business units the privacy extension covers. The privacy policy extends your existing information security policy with specific commitments around personal data.
The controller-processor role register documents your specific role for each data processing activity, the foundation the rest of the privacy documentation builds on. The privacy risk assessment, layered onto your existing ISO 27001 risk register, addresses privacy-specific risks like unauthorized data subject access.
Privacy-specific training records prove staff handling data subject requests understand their responsibilities, distinct from general security awareness training. The document control procedure you already have under ISO 27001 extends to cover new privacy documentation.
Data subject rights handling procedures document how access, correction, and deletion requests are managed, one of the most heavily scrutinized areas during an audit. Consent management records document how and when consent was obtained for data processing activities that require it.
Internal audit records covering the privacy extension specifically, alongside your existing ISO 27001 audit program, demonstrate ongoing oversight rather than a one-time addition.
Standards and Clauses: What ISO 27701 Actually Requires
- PIMS-Specific Requirements Related to ISO 27001 Clauses 4-10 extend each corresponding ISO 27001 clause with privacy-specific considerations, context, leadership, planning, support, operation, performance evaluation, and improvement, all now explicitly covering personal data management alongside general information security.
- Additional Guidance for PII Controllers covers specific obligations when you determine why and how personal data is processed, including data subject rights handling, consent management, and privacy by design considerations for new processing activities.
- Additional Guidance for PII Processors covers specific obligations when you process personal data on behalf of another organization, including contractual obligations, sub-processor management, and breach notification responsibilities to the controller.
- Annex mappings to other privacy frameworks help organizations cross-reference ISO 27701 controls against other regimes they may need to demonstrate alignment with, useful when partners or regulators reference frameworks beyond Law 22/11 specifically.
Case Study: A Bank in Luanda Extending Its ISO 27001 Certification
- A bank in Luanda, already ISO 27001 certified for three years, needed ISO 27701 certification after a partner insurance product raised specific questions about how customer data was shared between the two organizations.
- Our gap assessment found strong general information security but no formal controller-processor determination and no documented data subject rights handling procedure.
- Over ten weeks, we formally mapped the bank’s controller and processor roles across its own products and the partner arrangement, built data subject rights procedures, and trained customer service staff on handling requests. The extension audit found no major nonconformities.
- The bank used its ISO 27701 certification to resolve the partner’s data-sharing concerns and finalize the product arrangement.
Common Mistakes We See
- Trying to pursue ISO 27701 without a functioning ISO 27001 system first : The standard is explicitly an extension; attempting it standalone creates unnecessary complexity and confusion during the audit.
- Never formally determining controller versus processor status : This ambiguity is one of the most common findings during an extension audit.
- Treating data subject rights handling as a legal-only concern : Customer service and IT both need clear procedures for these requests to actually function day to day.
- Choosing a certifier unfamiliar with the ISO 27001-27701 relationship : Confirm your auditor genuinely understands how the extension audit works alongside your existing certification.
Who Actually Needs This?
Banks and financial institutions
already handling extensive personal data under ISO 27001 and facing rising privacy-specific scrutiny.
Read moreTelecommunications and mobile money operators
processing large volumes of customer personal data daily.
Read moreFintech and payment technology companies
where privacy failures carry both regulatory and reputational consequences.
Read moreAny ISO 27001-certified organization handling significant personal data
looking for the natural next step in demonstrating data governance maturity.
Read moreWhich Certification Body Should You Choose?
Confirm your certification body can audit the ISO 27701 extension alongside your existing ISO 27001 certification, ideally the same body handling your ISO 27001 surveillance audits. Ask specifically about their experience with controller-processor determinations. Be cautious of consultants treating this as an entirely separate project rather than a genuine extension.
Choosing the Right Partner?
| DIY | Generic Consultant | ShineCert | |
|---|---|---|---|
| Controller-processor mapping | Often incomplete | Templated, generic | Mapped to your actual data relationships |
| Timeline realism | Often underestimated | Sometimes overpromised | Set to your real starting point |
| ISO 27001 integration | Often disconnected | Sometimes handled as a separate project | Built directly onto your existing system |
| Post-certification support | None | Ends at the certificate | Supports ongoing surveillance audits |
Why Businesses Choose ShineCert in Angola?
Across 10 years of ISO consulting and more than 10,000 organizations certified worldwide, coordinated through our Riyadh and India offices, we build the privacy extension with ShineCert as the best ISO 27701 consultant in Angola, directly onto your existing information security system, avoiding the duplicated effort that comes from treating ISO 27701 as an unrelated project.
Ready to Get Started?
Whether you’re extending an existing ISO 27001 certification or building both systems together, we’ll assess your real situation and give you a clear, honest quote. Book a free consultation or contact us to get started.
Frequently Asked Questions
No, but Law 22/11 and APD oversight of personal data create a strong practical foundation certification that demonstrates compliance more credibly.
Yes, ISO 27701 is explicitly built as an extension to ISO 27001, not a standalone certification.
It depends heavily on whether you’re already ISO 27001 certified and the complexity of your data processing relationships. We quote individually.
Two to three months if already ISO 27001 certified; four to six months if pursuing both standards together.
Banking, telecommunications, mobile money, and fintech, particularly those already ISO 27001 certified.
Most of the process can happen remotely, often aligned with your existing ISO 27001 surveillance audit schedule.
In August 2019, in response to the global wave of privacy regulation following the EU’s GDPR.