
ISO 42001 Certification in India
Quick Answer
ISO 42001 certification is the world’s first internationally recognized Artificial Intelligence Management System credential, confirming an organization responsible for how it develops, deploys, and monitors AI systems. India currently has no standalone AI law, relying instead on the MeitY AI Governance Guidelines unveiled at the India AI Summit 2026, a principles-based framework built on seven “Sutras” rather than binding regulation. Certification typically takes two to five months and gives organizations a structured, internationally recognized way to demonstrate responsible AI governance ahead of firmer regulation.
About ISO 42001
ISO 42001 is the world’s first Artificial Intelligence Management System standard, published by the International Organization for Standardization. It requires organizations to establish governance over how AI systems are designed, developed, deployed, and monitored, covering risk assessment, data governance, transparency, and human oversight, rather than leaving AI governance to ad-hoc internal policy.
Certification means an independent, accredited certification body has audited your actual AI development and deployment practices, not just a written AI policy, and confirmed they genuinely meet the standard’s requirements. It runs on a three-year cycle with annual surveillance audits, appropriate for a technology area evolving as quickly as AI governance itself.
A brief history of the standard : ISO 42001 was published in December 2023, making it one of ISO’s newest management-system standards. It drew significantly on the EU AI Act’s risk-based approach during its development, and because it’s still so new, the pool of certification bodies and auditors with deep practical AI-system audit experience is genuinely smaller than for long-established standards like ISO 9001, worth factoring in when choosing a certification partner.
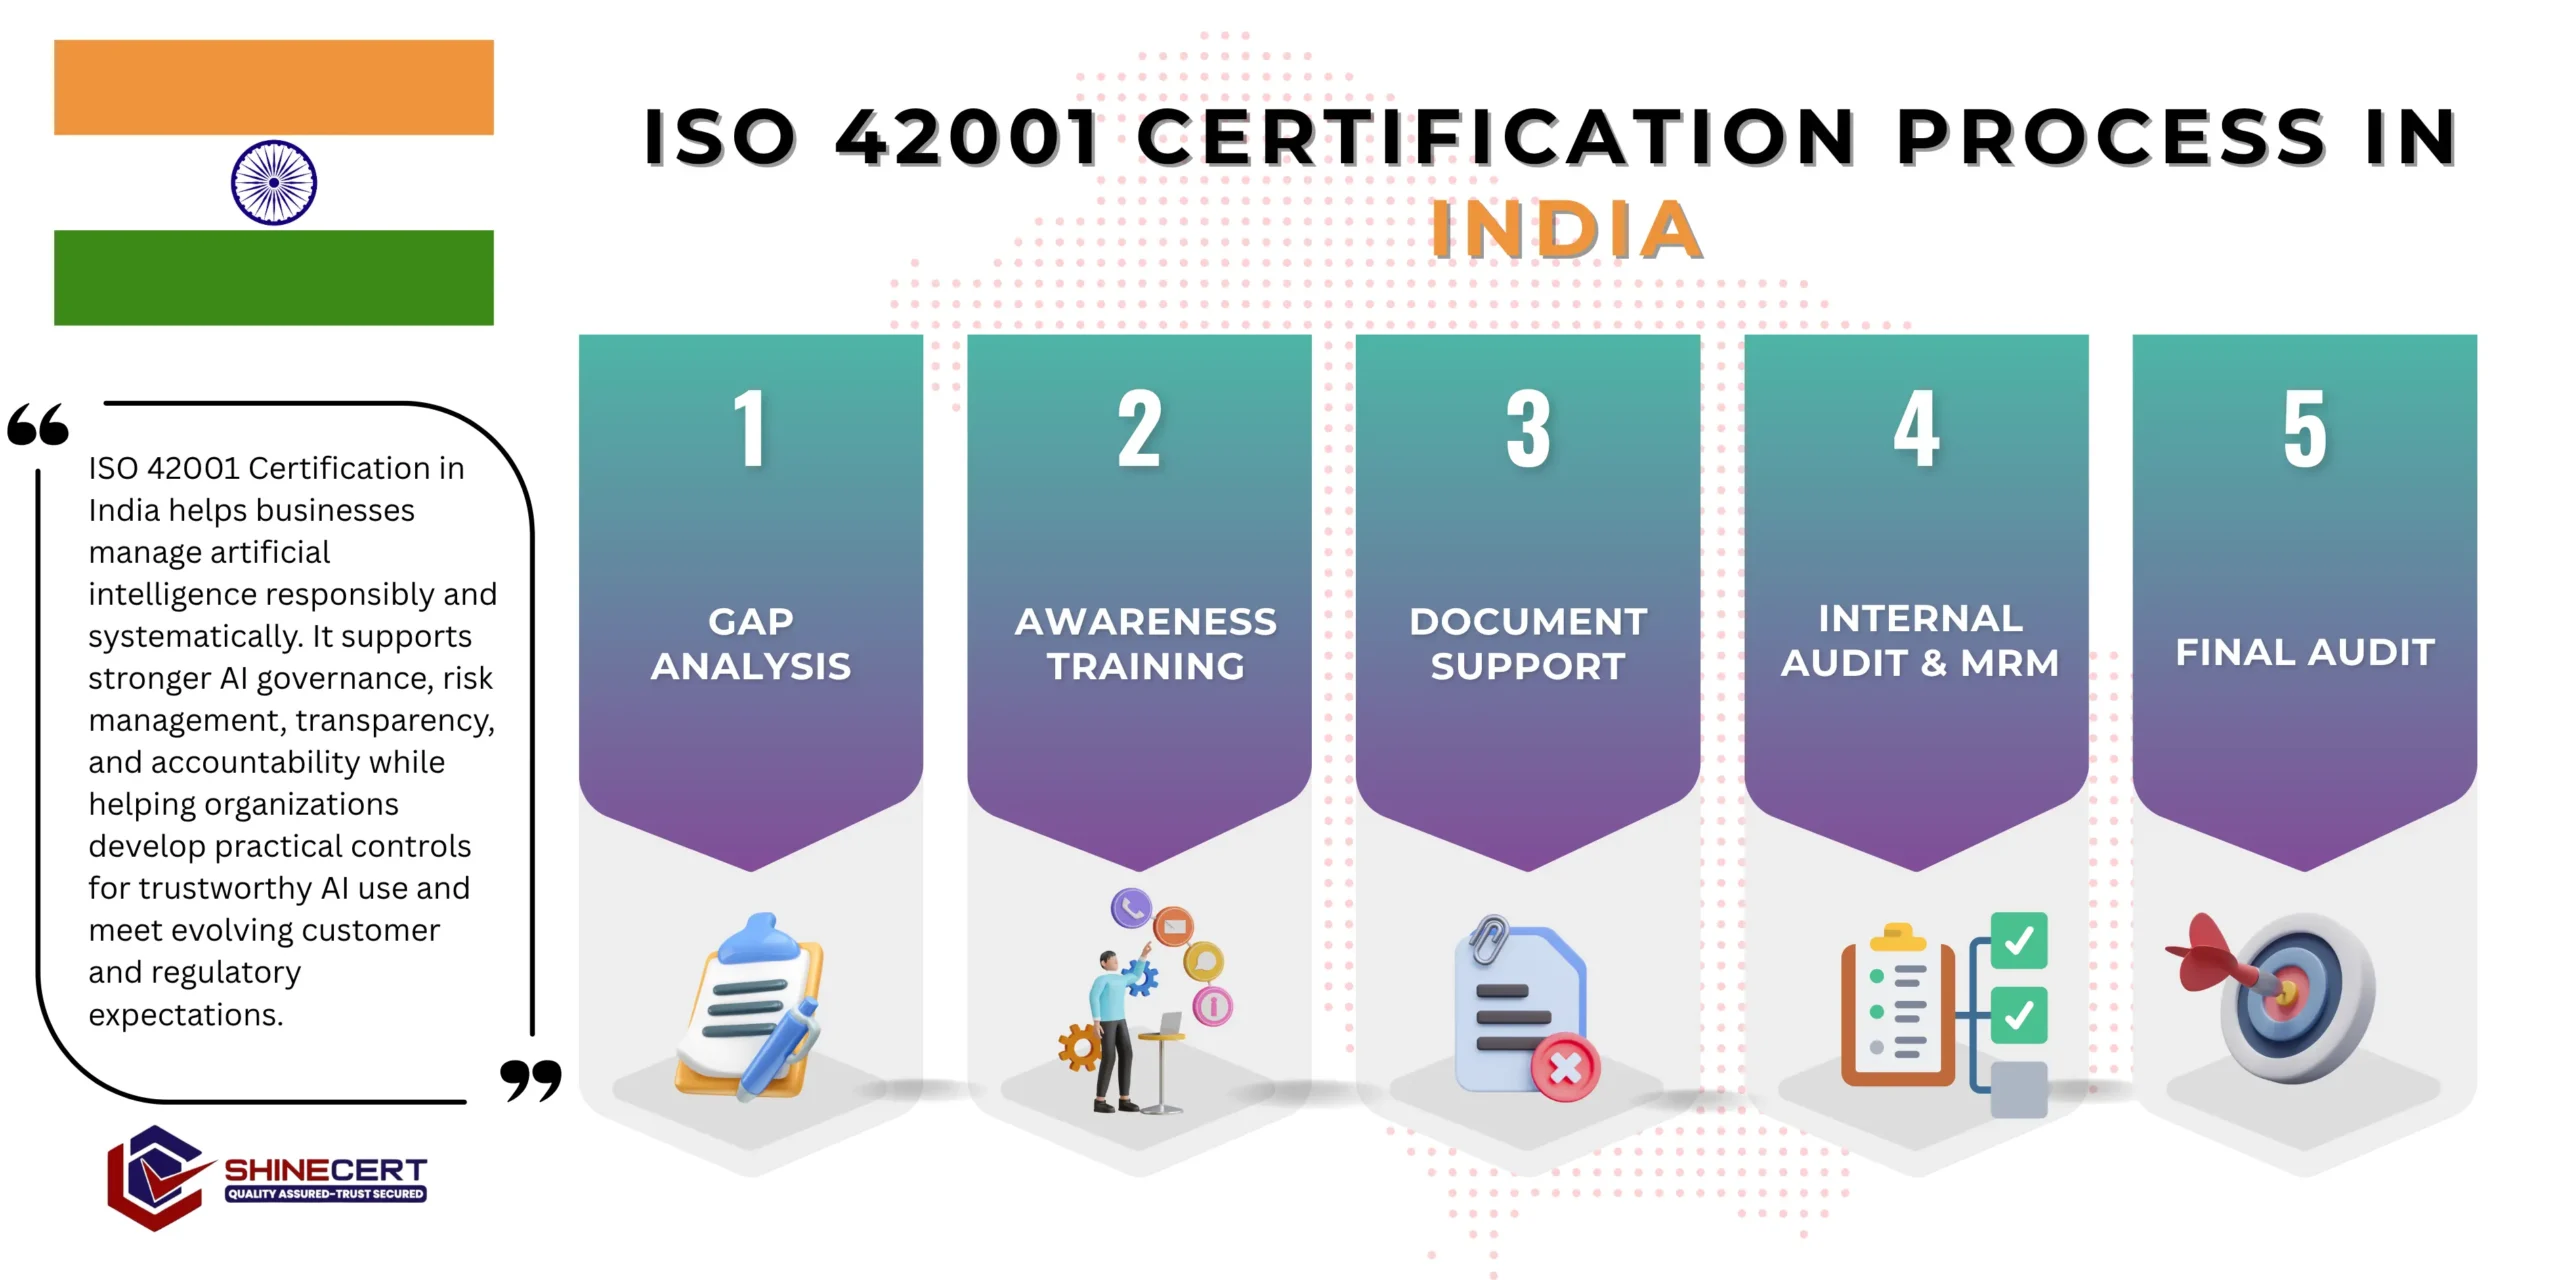
What are the steps to get ISO 42001 Certification in India?
our services
- ISO Certification India
- ISO 9001 Certification India
- ISO 14001 Certification India
- ISO 27001 Certification India
- ISO 22000 Certification India
- ISO 27701 Certification India
- ISO 45001 Certification India
- ISO 20000-1 Certification India
- ISO 13485 Certification India
- ISO 17025 Certification India
- ISO 31000 Certification India
- ISO 42001 Certification India
- ISO 37001 Certification India
- ISO 22301 Certification India
- ISO 50001 Certification India
- CE Mark Certification India
- GDPR Certification India
- GMP Certification India
- Halal Certification India
The Certification Process
Gap Assessment
We inventory every AI system your organization actually uses, including embedded features in third-party software many businesses don't initially count, and compare your current governance practices against the standard's requirements.
Documentation Development
We build the AI policy, risk assessment framework, and impact assessment templates, written around your actual AI use cases rather than generic language borrowed from a template built for a different kind of organization.
Implementation and Training
Governance controls go live, and staff involved in AI development, deployment, or oversight are trained specifically on their responsibilities, not handed a policy document to acknowledge.
Internal Audit and Management Review
We run a structured internal audit against the same criteria the certification auditor will use, and complete a formal management review with leadership.
Certification Audit
An accredited certification body audits your actual AI governance practices and issues the certificate once satisfied you genuinely meet the standard's requirements.
How Long Does Certification Take?
| Business Size | Typical Timeline | Why |
|---|---|---|
| Small, few AI systems | 2–3 months | Fewer systems and use cases to assess and document |
| Medium, several AI use cases | 3–4 months | More systems, more risk assessments, more training needed |
| Large or multi-product AI operations | 4–5 months | Extensive AI systems and cross-team governance coordination |
- Small businesses with a few AI systems (2 to 3 months) : With a narrower AI footprint, often a handful of embedded third-party tools rather than custom models, the risk assessment and documentation phase is considerably faster.
- Medium businesses with several AI use cases (3 to 4 months) : More AI systems, potentially spanning different products or departments, mean more individual risk assessments and more staff to train on governance responsibilities.
- Large or multi-product AI operations (4 to 5 months) : Coordinating governance across multiple AI-driven products, often built by different teams with different practices, typically requires more documentation review rounds and cross-team alignment.
- The variable that matters most: how complete your AI system inventory actually is before you start : Many businesses genuinely underestimate how many AI systems they’re using until a structured inventory is done, and discovering this partway through the process extends timelines more than any other single factor.
A real example : A Hyderabad-based telecom analytics company believed it had three AI systems in active use; our inventory process uncovered eleven, including several embedded within third-party customer analytics tools nobody had flagged as AI at all, which extended the gap assessment by roughly three weeks but ultimately produced a far more accurate and defensible governance system.
Why It Matters in India?
India does not currently have a standalone AI law. Instead, the Ministry of Electronics and Information Technology unveiled its AI Governance Guidelines at the India AI Summit 2026, following a drafting process that began in July 2025 under a dedicated MeitY committee. The framework adopts a principles-based, techno-legal approach anchored in seven guiding “Sutras,” alongside new institutions including the AI Governance and Economic Group, constituted 16 April 2026, and the Technology and Policy Expert Committee, constituted 18 April 2026. Rather than a standalone AI Act, the guidelines apply existing Indian laws through a risk-based lens, explicitly described as a “light-touch” model favoring innovation over binding rules for now.
What not being certified actually costs you. You’re less prepared if India’s light-touch approach tightens, which every one of the newly constituted governance institutions suggests is a live possibility as they build out sector-specific guidance. You’re also weaker positioned with international clients and investors who increasingly expect demonstrable AI governance, particularly in markets like the EU where the AI Act imposes binding requirements ISO 42001 is designed to align with. And without structured AI risk assessment, problems like biased outputs or uncontrolled model behavior tend to surface as public incidents rather than being caught internally.
Why is this happening in India right now? With MeitY’s guidelines so recently unveiled and the AI Governance and Economic Group and Technology and Policy Expert Committee only just constituted in April 2026, India’s AI governance landscape is visibly still being built, and organizations that establish a genuine management system now are positioned to adapt as sector-specific rules emerge, rather than scrambling to retrofit governance once mandates firm up.
What Affects the Cost?
- Number and complexity of AI systems : More use cases, whether custom-built or third-party, mean more individual risk assessments.
- Existing governance maturity : A business with some documented AI policy already starts from a stronger position than one with none.
- Industry risk profile : Fintech and healthcare AI applications typically require more detailed impact assessments than lower-stakes use cases.
- Certification body fees : Separate from consulting fees, and worth confirming accreditation and genuine AI-system audit experience before comparing quotes.
Required Documentation
The scope statement defines exactly which AI systems the certification covers. The AI policy sets top management’s commitment to responsible AI governance.
The AI risk assessment framework documents what could go wrong with each AI system and how severe the consequences would be. The AI system impact assessments evaluate effects on individuals and groups affected by AI-driven decisions.
Competence and training records prove staff developing or overseeing AI systems are genuinely qualified. The data governance procedure documents how training and input data is sourced and managed.
AI system lifecycle management procedures describe how systems are developed, tested, deployed, and retired. Human oversight procedures document where and how humans review or override AI-driven decisions.
AI system monitoring records, internal audit reports, and management review minutes demonstrate ongoing oversight. Corrective action records show how you respond when an AI system behaves unexpectedly.
Who Actually Needs This?
IT services and software companies building or deploying AI features
IT services and software companies building or deploying AI features, particularly for enterprise or international clients.
Read moreFintech companies using AI for credit scoring, fraud detection, or algorithmic trading
Fintech companies using AI for credit scoring, fraud detection, or algorithmic trading, where AI-driven decisions carry direct financial consequences.
Read moreHealthcare technology companies using AI for diagnostics or triage
Healthcare technology companies using AI for diagnostics or triage, where AI governance overlaps directly with patient safety.
Read moreBusinesses serving EU or international clients
Any business serving EU or international clients, where alignment with binding frameworks like the EU AI Act is increasingly a client expectation.
Read moreOrganizations already ISO 27001 certified
Organizations already ISO 27001 certified are looking to extend governance specifically to their AI systems, since the two standards share considerable structural overlap.
Read moreBenefits of ISO 42001 Certification
Certification builds exactly the risk assessment and oversight documentation that MeitY’s evolving framework is likely to expect in more detail over time.
Particularly those operating in or serving markets like the EU, where binding AI regulation already exists.
Structured risk assessment and human oversight requirements catch problems, biased outputs, uncontrolled model behavior, before they become visible failures.
With ISO 42001 still new globally, early certification signals AI governance maturity relative to competitors who haven’t yet formalized it.
A working management system is considerably easier to extend than one built from nothing once specific rules emerge.
Common Mistakes We See
- Underestimating how many AI systems are actually in use : Embedded AI features in third-party tools are routinely missed until a structured inventory is done, as our own case study above illustrates.
- Treating the AI policy as a document rather than an operational discipline : Auditors specifically probe whether human oversight and risk assessment are genuinely practiced, not just written down.
- Confusing data protection compliance with AI governance : DPDP Rules compliance and ISO 42001 governance overlap but aren’t the same thing; businesses sometimes assume one covers the other.
- Choosing a certification body without confirming genuine AI-system audit experience : Because the standard is still new, not every accredited body has deep practical experience auditing AI systems specifically.
Standards and Clauses: What ISO 42001 Actually Requires
- Context of the Organization (Clause 4) : requires identifying AI-relevant conditions and interested parties’ expectations, including regulators, customers, and those affected by AI-driven decisions.
- Leadership (Clause 5) : requires top management to set an AI policy and take visible ownership of responsible AI governance.
- Planning (Clause 6) : requires AI-specific risk and impact assessment, operationalizing responsible AI principles rather than treating them as aspirational statements.
- Support (Clause 7) : covers competence, awareness, and documented information needed to run the system.
- Operation (Clause 8) : covers AI system lifecycle management, data governance, and human oversight in practice.
- Performance Evaluation (Clause 9) : requires monitoring AI system performance and impact, internal audits, and management review.
- Improvement (Clause 10) : requires acting on AI-related nonconformities and continually improving governance over time.
Case Study: A Hyderabad-Based Telecom Analytics Company
- A telecom analytics company needed ISO 42001 certification to satisfy a European carrier client’s AI governance due diligence requirement ahead of a data analytics partnership.
- Our gap assessment began, as it always does, with a structured AI system inventory. The company believed it had three AI systems in active use; the inventory process uncovered eleven, including several embedded within third-party customer analytics platforms nobody had previously flagged as AI at all.
- Over roughly four months, we built risk and impact assessments for all eleven systems and established human oversight procedures for the highest-risk ones. The certification audit confirmed genuine governance discipline, with only minor documentation gaps in monitoring records.
- The company secured the partnership, with the client specifically citing the certification’s completeness, given how many systems it actually covered, as a deciding factor.
Answering the Objections Every Owner Has
“There’s no Indian law requiring this yet, why bother?”
MeitY’s own newly constituted governance institutions signal that firmer rules are actively being developed; certifying now means you’re ready rather than reacting once they arrive.
“We only use a few AI tools, not building our own models.”
The standard applies to how you govern AI use generally, including third-party AI tools and embedded AI features, not only custom-built models; many businesses discover they’re using more AI systems than they realized once they inventory properly.
“Isn’t this just for big tech companies?”
Any organization using AI in ways that affect customers, decisions, or data carries governance responsibility regardless of size; the standard scales its documentation expectations to your actual AI footprint.
“Can’t we just write an internal AI policy ourselves?”
A policy alone doesn’t demonstrate ongoing risk assessment, monitoring, or human oversight in practice, which is exactly what an audit, or a client’s due diligence, will actually test.
Choosing the Right Partner?
| DIY | Generic Consultant | ShineCert | |
|---|---|---|---|
| AI system inventory | Often incomplete, missing embedded third-party AI | Templated, rarely thorough | Built through a structured, complete inventory process |
| MeitY framework awareness | Rarely considered | Sometimes mentioned, rarely integrated | Tracked and reflected in your governance approach |
| Auditor AI experience verification | Often overlooked | Sometimes assumed rather than confirmed | Verified explicitly given how new this standard is |
| Post-certification support | None | Often ends at the certificate | Built to support your ongoing surveillance audits |
Which Certification Body Should You Choose?
Confirm the certification body is accredited by NABCB or another IAF-member accreditation authority, and specifically ask about their auditors’ practical experience with AI systems, given how new this standard is globally. Confirm the audit includes a genuine review of your AI systems in operation, not a policy-document check alone.
Why Businesses Choose ShineCert in India?
We’ve spent 10 years helping more than 10,000 businesses worldwide get certified, coordinated through our Riyadh and India offices with work delivered remotely or on-site as needed. Our consultants start every ISO 42001 engagement with a genuinely thorough AI system inventory, since incomplete inventories are the most common reason implementations run long, and we track MeitY’s evolving guidance closely so your governance approach stays relevant as India’s framework matures, with ShineCert as the best ISO 42001 consultant in India. We only work with accredited certification bodies with genuine AI-system audit capability.
Frequently Asked Questions
No, India has no standalone AI law; MeitY’s AI Governance Guidelines are currently principles-based rather than binding, but certification positions you ahead of tightening expectations.
It depends on the number and complexity of your AI systems and existing governance maturity. We quote individually.
Usually two to five months depending on business size, with the completeness of your AI system inventory mattering more than headcount alone.
Yes, the standard covers how you govern AI use generally, including embedded third-party AI features, which is often where businesses discover the largest gaps.
Confirm accreditation by NABCB or another IAF-member authority, and specifically confirm genuine auditor experience with AI systems given how new this standard is.