ISO 37001 Certification in Egypt
Quick Answer
ISO 37001 certification confirms an organization’s anti-bribery management system meets an internationally recognized standard, verified by an independent, accredited certification body. In Egypt, the Administrative Control Authority, an independent oversight body established in 1964, exercises administrative, financial, and criminal control over public bodies specifically to combat corruption, and businesses in Egypt’s public procurement sector report perceiving diversion of public funds and favoritism toward connected companies as widespread. Certification gives businesses a credible, evidenced way to demonstrate they operate differently. It typically takes three to five months.
Why ISO 37001 Matters in Egypt?
A dedicated anti-corruption oversight body has operated since 1964 : The Administrative Control Authority exercises administrative, financial, and criminal control over public bodies specifically to combat corruption, co-formulate national anti-corruption strategy, and raise awareness of its consequences, giving Egypt a long-standing institutional framework businesses need to operate credibly within.
Procurement corruption risk perception is a documented concern : Companies in Egypt’s public procurement sector report facing a high risk of corruption, with widespread perception that public funds are diverted to connected individuals and companies, and that favoritism among procurement officials is common.
Transparency measures are actively being pursued : Regulations aimed at enhancing transparency in public procurement processes continue to develop, with the Administrative Control Authority responsible for monitoring and investigating corruption across the system.
Certification provides evidence, not just assurance : In an environment where corruption risk perception is genuinely documented, a certified anti-bribery management system gives partners, regulators, and procurement authorities verifiable evidence of controls, rather than asking them to simply take your word for it.
What are the steps to get ISO 37001 Certification in Egypt?
our services
- ISO Certification Egypt
- ISO 9001 Certification Egypt
- ISO 14001 Certification Egypt
- ISO 27001 Certification Egypt
- ISO 22000 Certification Egypt
- ISO 27701 Certification Egypt
- ISO 45001 Certification Egypt
- ISO 20000-1 Certification Egypt
- ISO 13485 Certification Egypt
- ISO 17025 Certification Egypt
- ISO 31000 Certification Egypt
- ISO 42001 Certification Egypt
- ISO 37001 Certification Egypt
- ISO 22301 Certification Egypt
- ISO 50001 Certification Egypt
- CE Mark Certification Egypt
- GDPR Certification Egypt
- GMP Certification Egypt
- Halal Certification Egypt
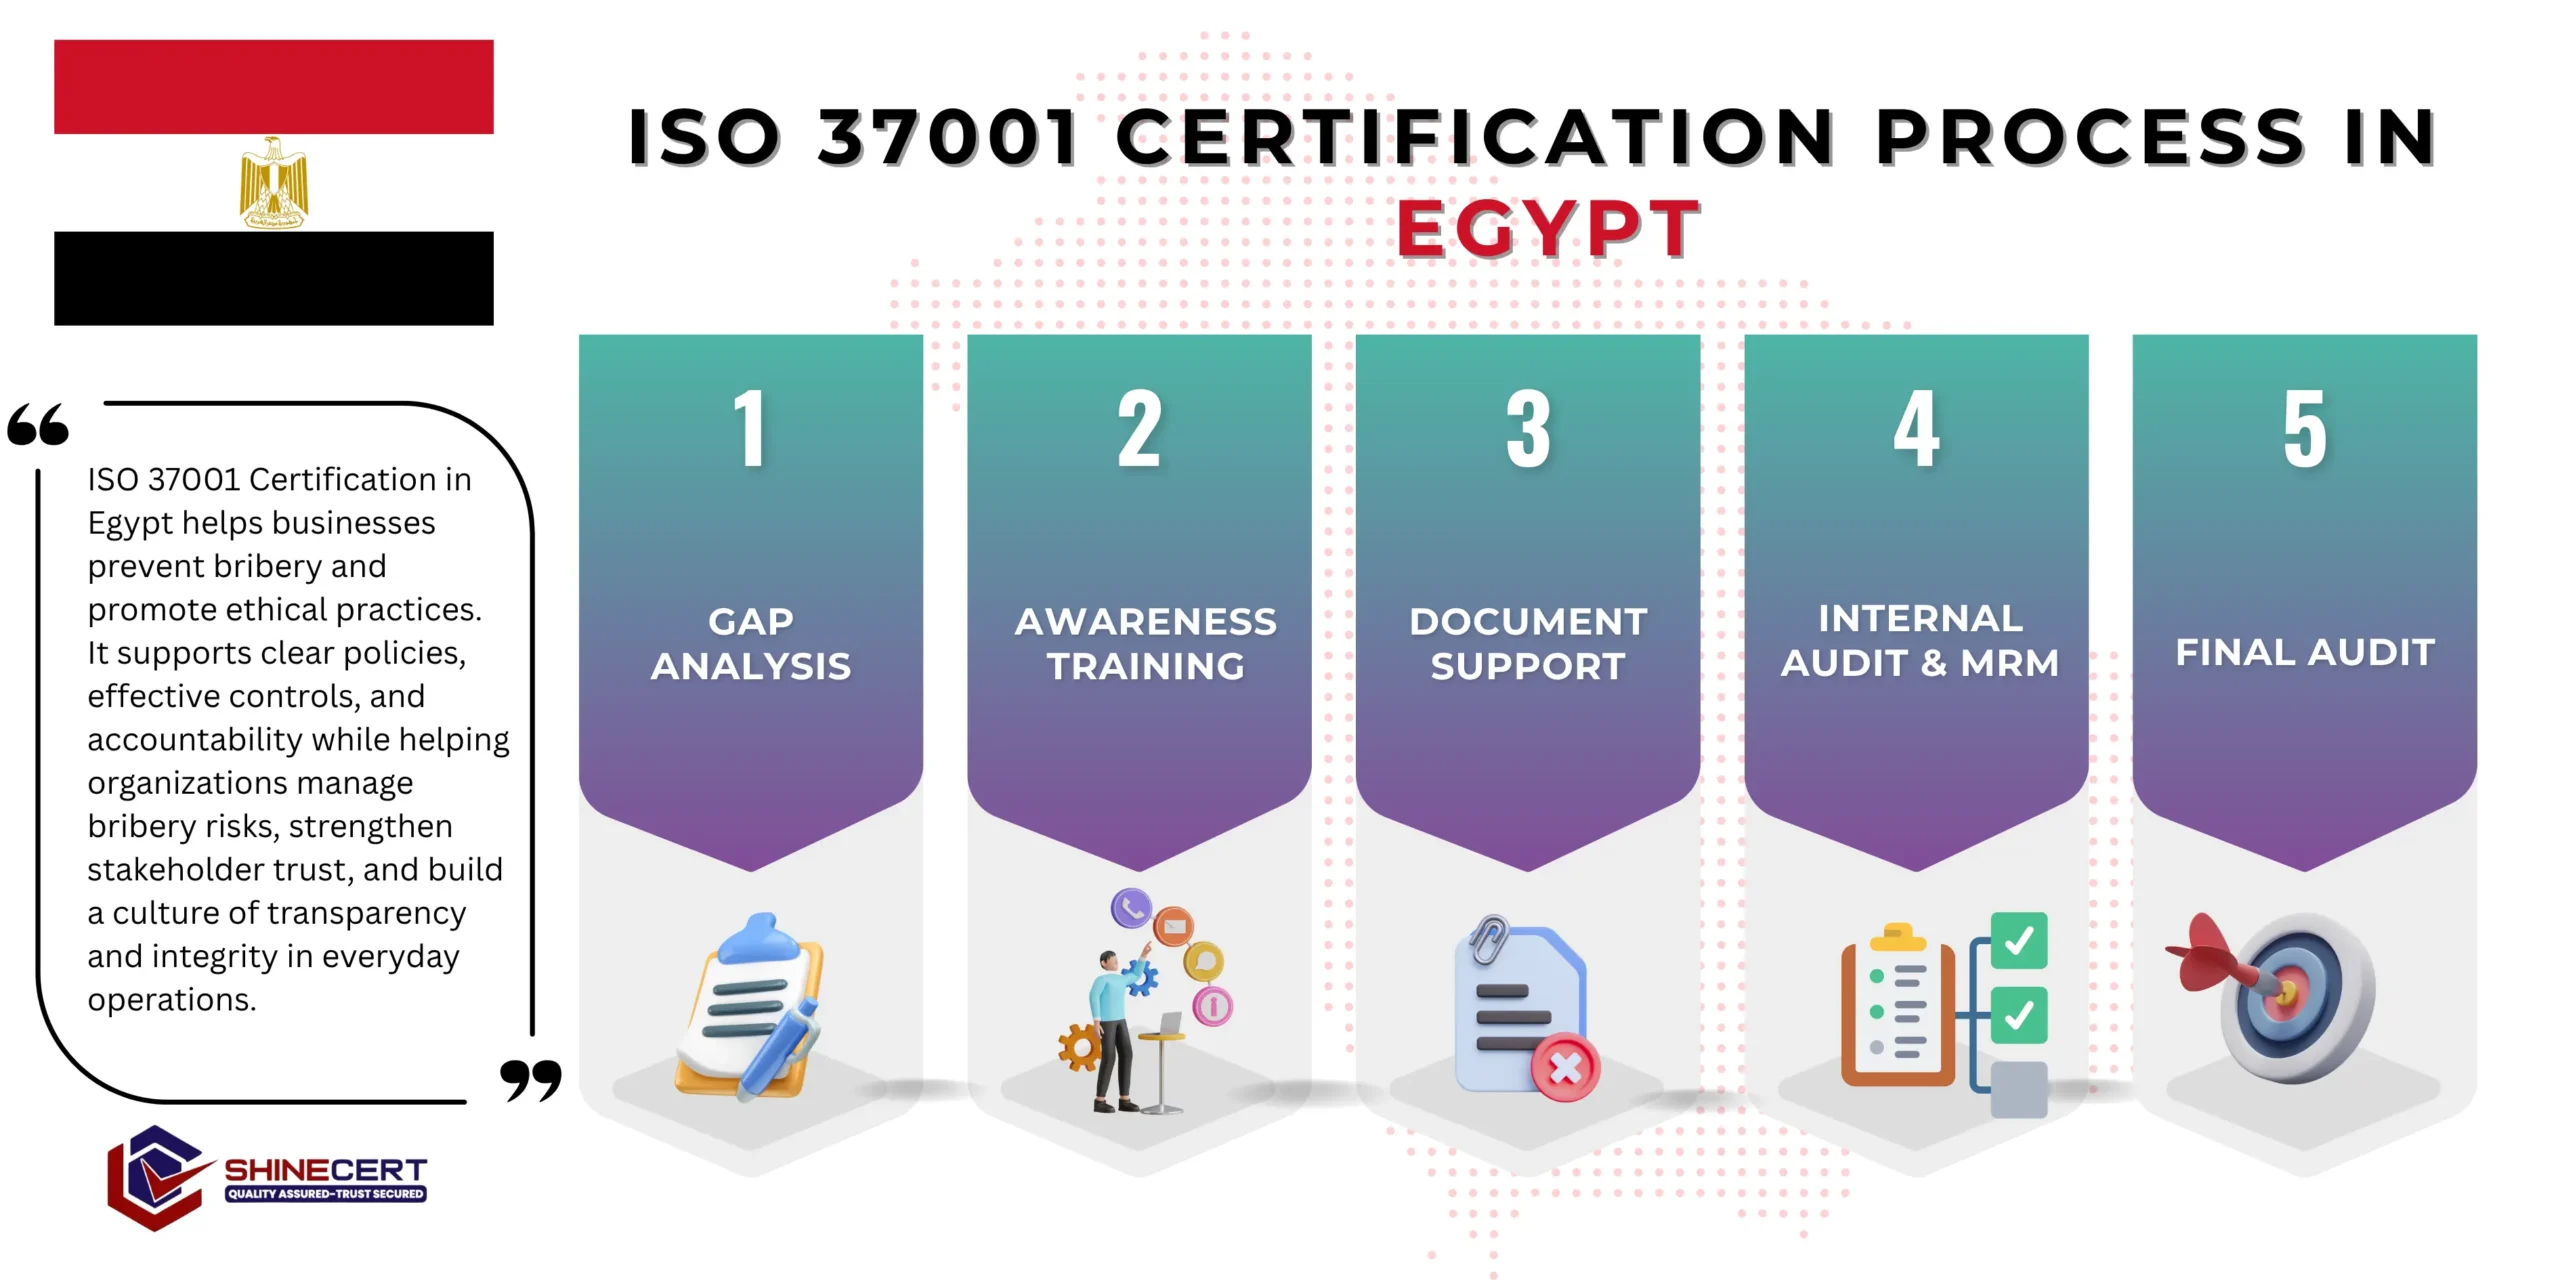
The ISO 37001 Certification Process in Egypt
Bribery Risk Assessment
We identify where your genuine bribery exposure sits, procurement relationships, government interactions, third-party intermediaries, rather than treating all business activities as equally risky.
Controls concentrated where they actually matter.
A documented bribery risk assessment.
Documentation Development
We build your anti-bribery policy, due diligence procedures for business associates, and financial controls specific to your identified risk areas.
A system that addresses your real exposure, not a generic compliance template.
A complete documentation set.
Implementation and Training
Controls go live, and staff plus relevant business partners are trained on what constitutes bribery and how to raise concerns.
A workforce and partner network that genuinely understands the boundaries, not just a signed policy acknowledgment.
Training records and operating evidence.
Internal Audit and Management Review
We test the system internally, ideally with some independence from operational management, and run your first review.
Gaps surface with time to address them.
An internal audit report and review minutes.
Certification Audit
An accredited certification body audits your system and issues your certificate.
Independently verified evidence of anti-bribery controls for procurement bids and partner due diligence.
Your certificate and a surveillance schedule.
Bribery Risk Assessment
We identify where your genuine bribery exposure sits, procurement relationships, government interactions, third-party intermediaries, rather than treating all business activities as equally risky.
Controls concentrated where they actually matter.
A documented bribery risk assessment.
Documentation Development
We build your anti-bribery policy, due diligence procedures for business associates, and financial controls specific to your identified risk areas.
A system that addresses your real exposure, not a generic compliance template.
A complete documentation set.
Implementation and Training
Controls go live, and staff plus relevant business partners are trained on what constitutes bribery and how to raise concerns.
A workforce and partner network that genuinely understands the boundaries, not just a signed policy acknowledgment.
Training records and operating evidence.
Internal Audit and Management Review
We test the system internally, ideally with some independence from operational management, and run your first review.
Gaps surface with time to address them.
An internal audit report and review minutes.
Certification Audit
An accredited certification body audits your system and issues your certificate.
Independently verified evidence of anti-bribery controls for procurement bids and partner due diligence.
Your certificate and a surveillance schedule.
What Is ISO 37001, Clause by Clause?
- Clause 4: Context of the Organization : Requires identifying bribery risks specific to your operations and understanding interested-party expectations, including procurement authorities, business partners, and regulators.
- Clause 5: Leadership : Requires top management to establish an anti-bribery policy and demonstrate genuine, visible commitment, since a policy nobody in leadership actually follows undermines the entire system.
- Clause 6: Planning : Requires a documented bribery risk assessment specific to your business relationships, transactions, and geographic exposure, and planning actions to address identified risks.
- Clause 7: Support : Covers competence, training, and communication needed to run the system, including ensuring staff and business partners understand what constitutes bribery in practice, not just in theory.
- Clause 8: Operation : The largest clause, covering due diligence on business associates and transactions, financial and non-financial controls, gift and hospitality management, and procedures for raising concerns without fear of retaliation.
- Clause 9: Performance Evaluation : Requires monitoring the system’s effectiveness, conducting internal audits, and management review, including review by a function independent of operations where practical.
- Clause 10: Improvement : Requires investigating identified issues, taking corrective action, and continually improving the anti-bribery management system.
What Does ISO 37001 Certification Cost in Egypt?
- Exposure to public procurement and government relationships : Businesses regularly bidding on public contracts typically need more extensive due diligence and controls than purely private-sector operations.
- Use of third-party intermediaries or agents : More intermediary relationships mean more due diligence documentation required.
- Current compliance maturity : A business with existing financial controls and codes of conduct starts from a stronger position than one without.
- Certification body fees : Separate from consulting costs and vary by scope.
Benefits of ISO 37001 Certification
Certification provides evidenced anti-bribery controls in a sector where corruption risk perception is genuinely documented.
Systematic due diligence under Clause 8 catches problematic relationships before they become liabilities.
Certification signals genuine governance to partners increasingly attentive to anti-corruption compliance in their own supply chains.
Clause 8’s whistleblowing provisions give staff a real channel instead of silence or informal workarounds.
As procurement transparency measures continue developing, certified businesses are positioned ahead of that curve rather than reacting to it later.
How Long Does ISO 37001 Certification Take in Egypt?
| Business Profile | Typical Timeline | Why |
|---|---|---|
| Limited government or procurement exposure | 3 months | Narrower risk assessment and simpler controls |
| Regular public procurement bidder | 4 months | More due diligence and controls to document |
| Significant intermediary or agent relationships | 5 months | Extensive third-party due diligence required |
What Documents Do You Need for ISO 37001 in Egypt? (By Clause)
- Clause 4 Documentation : Document: Scope of the Anti-Bribery Management System. Document: Bribery Risk Context Analysis.
- Clause 5 Documentation : Document: Anti-Bribery Policy. Document: Roles and Responsibilities Record.
- Clause 6 Documentation : Document: Bribery Risk Assessment. Document: Anti-Bribery Objectives and Planning Record.
- Clause 7 Documentation : Document: Training Records. Document: Communication Procedure.
- Clause 8 Documentation : Document: Due Diligence Procedures for business associates and transactions. Document: Gift, Hospitality, and Donations Policy. Document: Whistleblowing and Concerns Procedure.
- Clause 9 Documentation : Document: Internal Audit and Management Review Records.
- Clause 10 Documentation : Document: Corrective Action Records. Document: Continual Improvement Log.
Why Businesses Choose ShineCert in Egypt?
Businesses searching for the best ISO 37001 consultant in Egypt are usually trying to win business in an environment where procurement corruption perception genuinely affects competitiveness. We’ve spent 10 years helping more than 10,000 businesses worldwide get certified, coordinated through our Riyadh and India offices. We build controls concentrated on your real exposure, procurement, intermediaries, government relationships, not generic compliance boilerplate.
Case Study: A Construction Firm Bidding on Public Infrastructure Projects
- A mid-sized construction firm regularly bidding on public infrastructure projects needed ISO 37001 certification after losing a bid to a competitor that held it, despite believing its own pricing was more competitive.
- Our risk assessment found the firm had informal ethical practices but no documented due diligence process for subcontractors and agents, no formal gift and hospitality policy, and no confidential channel for staff to raise concerns.
- Over four months, we built a due diligence procedure for subcontractor and agent relationships, a documented gift and hospitality policy with clear approval thresholds, and a confidential reporting channel. The certification audit passed with no major nonconformities.
- The firm has since referenced its certification directly in two subsequent public tender submissions, treating it as a genuine differentiator rather than a compliance afterthought.
Ready to Get Started?
Whether you’re bidding on public infrastructure projects or strengthening partner due diligence, ShineCert will assess your real exposure and give you a clear, honest quote. Book a free consultation or contact us to get started.
Frequently Asked Questions
No, but the Administrative Control Authority’s active anti-corruption oversight and documented procurement corruption risk perception make certification a genuine competitive advantage in public tenders.
It depends on your procurement exposure and current compliance maturity. We quote individually.
Usually three to five months, depending on intermediary and government relationship complexity.
No, but it provides evidenced anti-bribery controls that increasingly differentiate bidders in a documented high-corruption-risk sector.
Yes, Clause 8’s due diligence requirements extend to business associates acting on your behalf.
Documentation development can happen remotely; the certification audit typically requires at least a partial site visit.