GDPR Certification in Egypt
Quick Answer
GDPR is European Union law, not something ShineCert or any consultant certifies you against directly, but its Article 3 extraterritorial scope means it can apply to an Egyptian business that never opens a European office. If your company processes personal data of people located in the EU, whether through outsourced services, a website targeting European customers, or a European client relationship, GDPR obligations likely follow that data regardless of where your staff or servers sit. This sits alongside, not instead of, Egypt’s own Personal Data Protection Law No. 151/2020, whose licensing deadline falls October 31, 2026. We help you work out whether GDPR actually applies to your specific operations and build the compliance program if it does.
What Is GDPR?
The General Data Protection Regulation is the European Union’s comprehensive data protection law, governing how personal data of people in the EU is collected, processed, stored, and transferred. It grants individuals specific rights over their data, including access, correction, deletion, and portability, and requires organizations to demonstrate lawful, transparent, and secure processing.
What makes GDPR relevant well beyond EU borders is its Article 3 territorial scope, which applies the law to any organization processing personal data of people located in the EU, whether the organization offers goods or services to them or simply monitors their behavior, regardless of where that organization is based.
There is no GDPR “certificate.” Compliance is demonstrated through documented policies, technical controls, and evidence of accountability, which is where a structured compliance program becomes essential rather than optional.
Why GDPR Matters for Egyptian Businesses?
- Outsourced service delivery is the most common trigger : Egypt’s outsourcing sector is targeting $6 billion in exports in 2026, much of it serving European clients directly, and any Egyptian provider handling data on behalf of a European client is likely processing EU personal data, bringing Article 3 into play regardless of where the work is physically performed.
- Egypt’s own data protection law now has a real enforcement calendar : The Personal Data Protection Law’s Executive Regulations, issued November 2025, established the Personal Data Protection Center as the active supervisory authority, with a licensing grace period ending October 31, 2026, but compliance with the PDPL does not automatically satisfy GDPR obligations toward EU data subjects, and the reverse is also true.
- Contractual pressure from European clients is increasing : European businesses are themselves accountable for how their vendors handle EU personal data, so many now require Egyptian service providers to demonstrate GDPR-aligned practices contractually before work begins, independent of any Egyptian legal requirement.
- Cross-border data transfer rules add complexity on both sides : Where an Egyptian provider receives personal data from an EU client, GDPR’s international transfer rules apply on top of ordinary processing obligations, and PDPL’s own cross-border transfer licensing requirement adds a second layer businesses need to satisfy simultaneously.
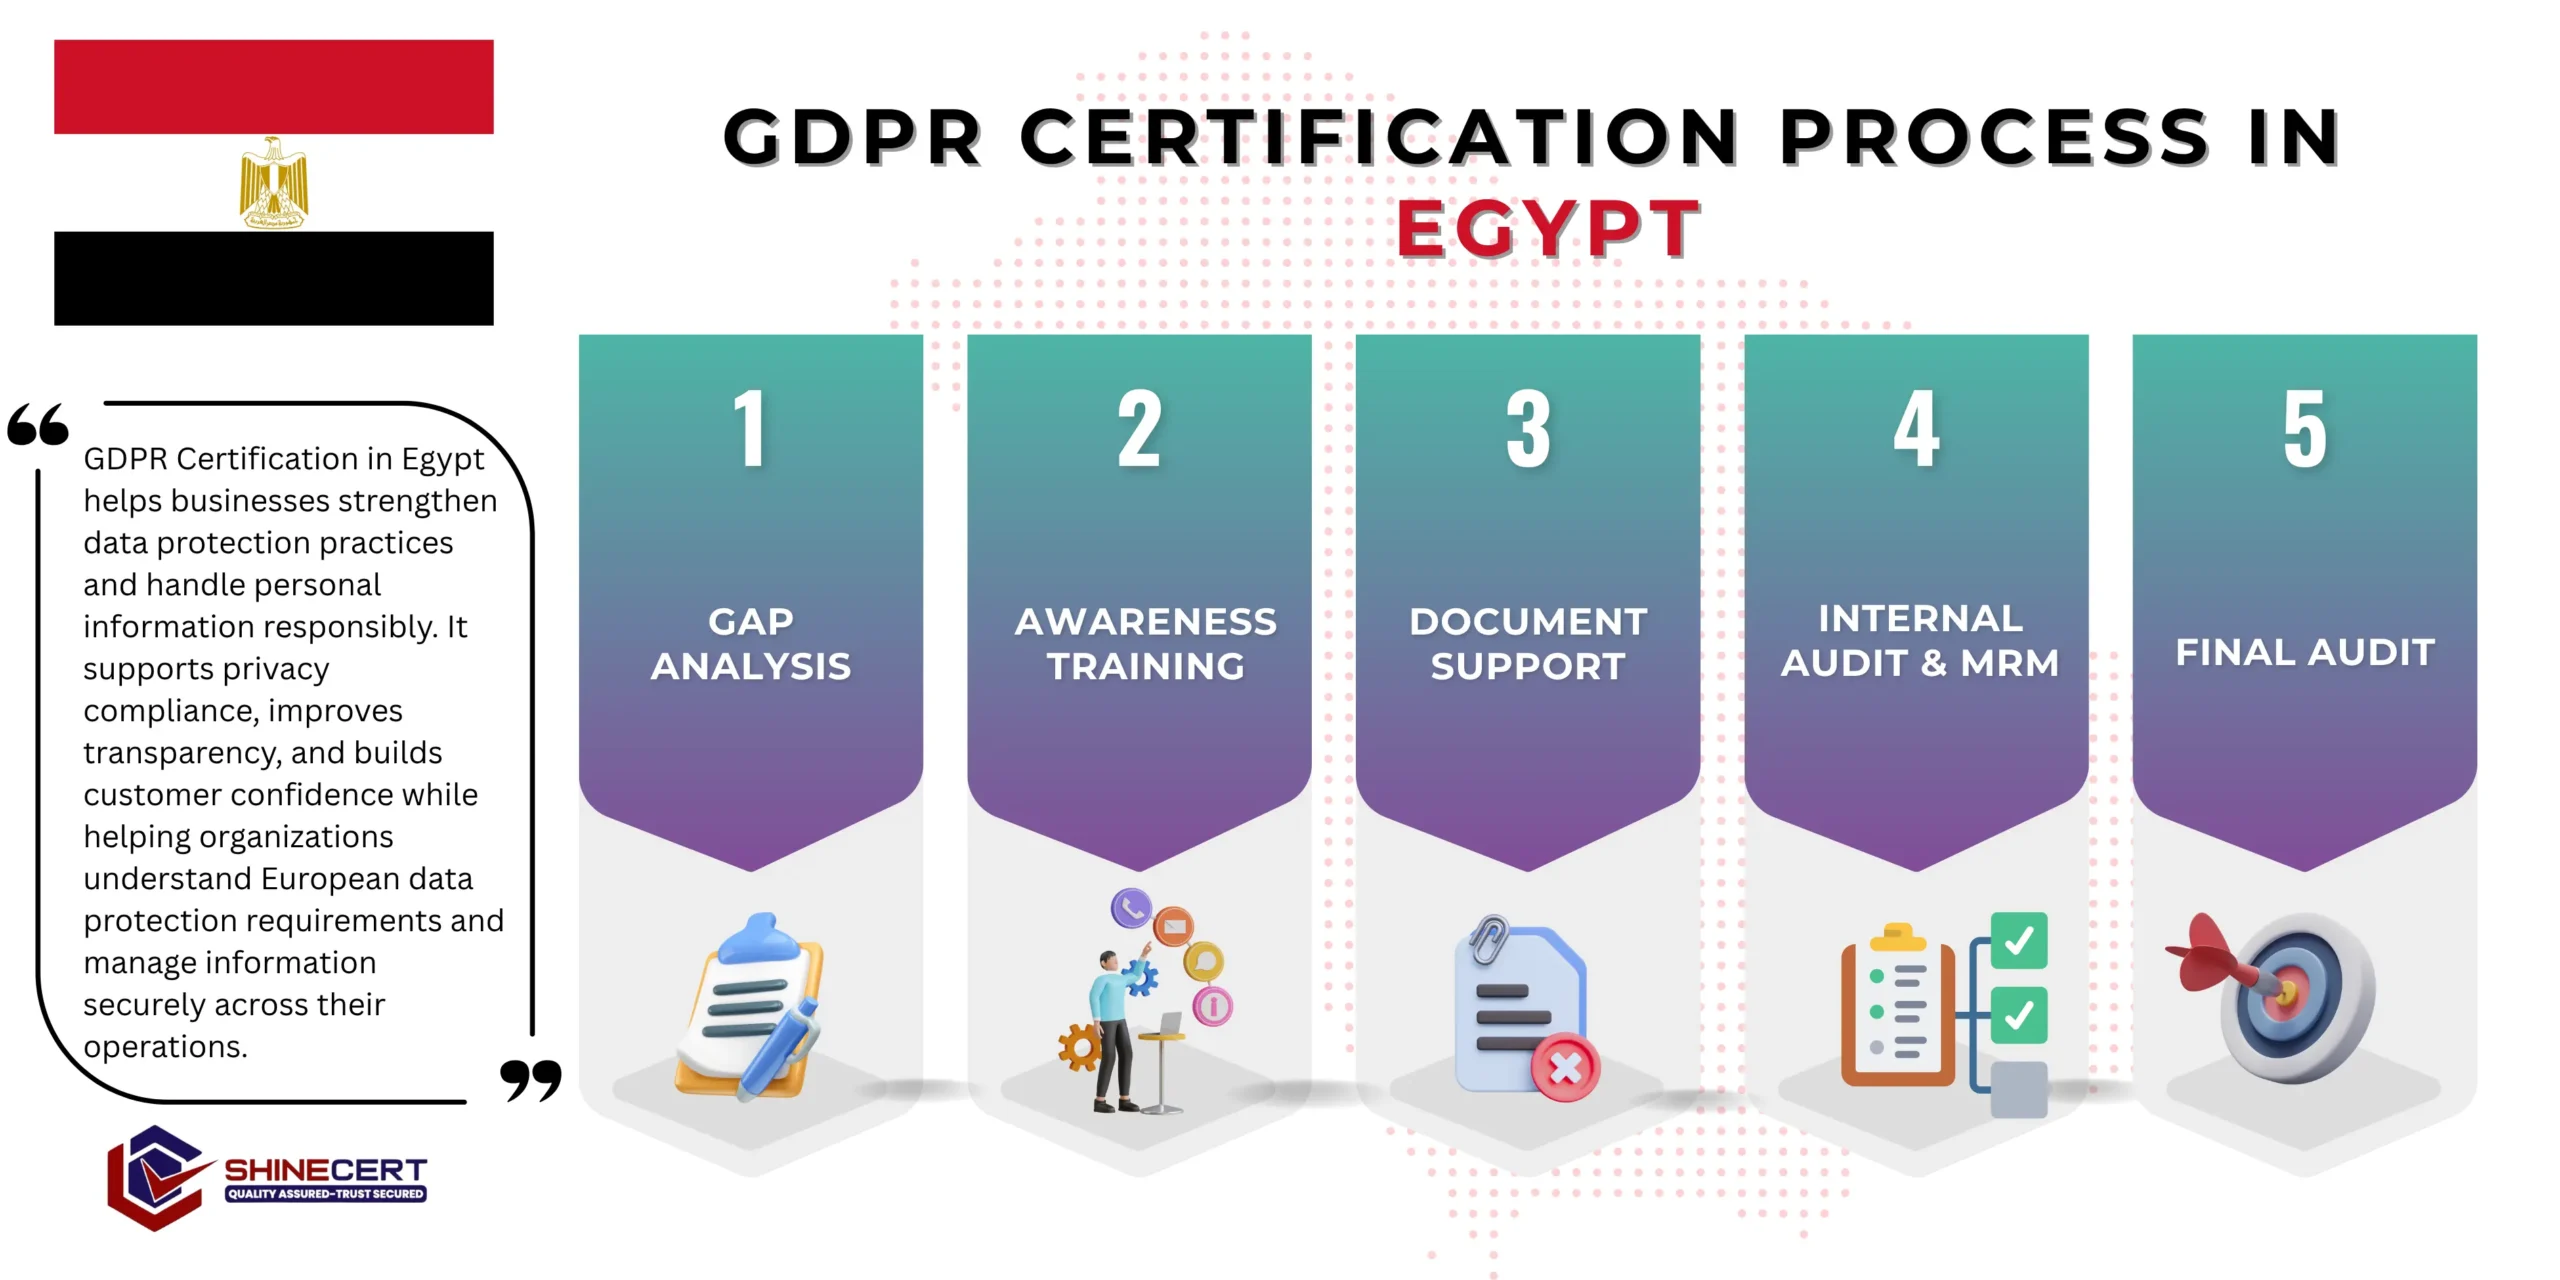
What are the steps to get GDPR Certification in Egypt?
our services
- ISO Certification Egypt
- ISO 9001 Certification Egypt
- ISO 14001 Certification Egypt
- ISO 27001 Certification Egypt
- ISO 22000 Certification Egypt
- ISO 27701 Certification Egypt
- ISO 45001 Certification Egypt
- ISO 20000-1 Certification Egypt
- ISO 13485 Certification Egypt
- ISO 17025 Certification Egypt
- ISO 31000 Certification Egypt
- ISO 42001 Certification Egypt
- ISO 37001 Certification Egypt
- ISO 22301 Certification Egypt
- ISO 50001 Certification Egypt
- CE Mark Certification Egypt
- GDPR Certification Egypt
- GMP Certification Egypt
- Halal Certification Egypt
The GDPR Compliance Process for Egyptian Businesses
Since there’s no certificate to pursue, compliance is built through five practical stages.
Applicability Assessment
We review your actual client base and data flows to determine honestly whether Article 3 applies, since not every Egyptian business serving international clients is automatically in scope.
Building a full GDPR program you don’t actually need wastes resources better spent elsewhere.
A clear, honest determination of your GDPR exposure.
Data Mapping
We document exactly what EU personal data flows through your organization, from which clients, processed by which systems and staff.
You cannot protect or evidence controls over data you haven’t mapped.
A complete data flow map specific to your EU-facing operations.
Policy and Contract Development
We help draft the privacy policies, data processing agreements, and international transfer clauses your specific client relationships require.
European clients increasingly ask for these documents before signing contracts, not after.
A complete GDPR policy and contract documentation set.
Technical and Organizational Controls
Access controls, encryption practices, and staff training are implemented to match what your policies actually commit to.
A policy that describes controls you haven’t implemented is a liability, not a protection.
Controls that genuinely match your documented commitments.
Ongoing Accountability
We help establish breach response procedures and a process for responding to client due-diligence questionnaires, which arrive far more often than actual incidents.
Most GDPR-related client interactions are documentation requests, not emergencies, so being ready to respond quickly matters commercially.
A repeatable process for client compliance evidence requests.
Applicability Assessment
We review your actual client base and data flows to determine honestly whether Article 3 applies, since not every Egyptian business serving international clients is automatically in scope.
Building a full GDPR program you don’t actually need wastes resources better spent elsewhere.
A clear, honest determination of your GDPR exposure.
Data Mapping
We document exactly what EU personal data flows through your organization, from which clients, processed by which systems and staff.
You cannot protect or evidence controls over data you haven’t mapped.
A complete data flow map specific to your EU-facing operations.
Policy and Contract Development
We help draft the privacy policies, data processing agreements, and international transfer clauses your specific client relationships require.
European clients increasingly ask for these documents before signing contracts, not after.
A complete GDPR policy and contract documentation set.
Technical and Organizational Controls
Access controls, encryption practices, and staff training are implemented to match what your policies actually commit to.
A policy that describes controls you haven’t implemented is a liability, not a protection.
Controls that genuinely match your documented commitments.
Ongoing Accountability
We help establish breach response procedures and a process for responding to client due-diligence questionnaires, which arrive far more often than actual incidents.
Most GDPR-related client interactions are documentation requests, not emergencies, so being ready to respond quickly matters commercially.
A repeatable process for client compliance evidence requests.
What Affects GDPR Compliance Cost in Egypt?
- Number of EU client relationships : More distinct client data flows mean more mapping and contract work.
- Current documentation maturity : A business with no existing privacy policy starts further back than one with basic data protection practices already in place.
- Whether ISO 27001 or ISO 27701 groundwork already exists : Businesses already certified to these standards typically need less additional work, since much of the technical control documentation overlaps directly.
- Volume and sensitivity of data processed : Handling larger volumes or more sensitive categories of EU personal data generally requires more robust controls.
Benefits of GDPR Compliance
Many European businesses simply won’t sign with a vendor that can’t demonstrate GDPR-aligned practices.
GDPR fines can be significant, and Article 3 makes Egyptian businesses processing EU data genuinely exposed, not merely theoretically.
Having documentation ready means responding to a client’s due-diligence questionnaire in days rather than scrambling for weeks.
Once the core program exists, extending it to new clients is far faster than starting fresh each time.
Building genuine data protection discipline supports meeting both frameworks rather than treating them as separate burdens.
How Long Does GDPR Compliance Take?
| Business Situation | Typical Timeline | Why |
|---|---|---|
| Limited EU exposure, basic controls needed | 6–8 weeks | Narrower scope, fewer client relationships to map |
| Established outsourcing operations with multiple EU clients | 2–3 months | More data flows and contract relationships to document |
| Complex, multi-client outsourcing operations | 3–4 months | Extensive mapping, contracts, and control implementation |
What Documentation Is Involved in GDPR Compliance?
- Assessment and Mapping : Document: Article 3 Applicability Assessment. Document: Data Flow Map.
- Policy Documentation : Document: Privacy Policy. Document: Data Processing Agreement Template.
- Transfer and Security Documentation : Document: International Data Transfer Safeguards. Document: Technical and Organizational Measures Record.
- Accountability Documentation : Document: Breach Response Procedure. Document: Staff Training Records.
Why Businesses Choose ShineCert in Egypt?
We’ve spent 10 years helping more than 10,000 businesses worldwide navigate data protection and certification requirements, coordinated through our Riyadh and India offices. As the best GDPR consultant in Egypt, ShineCert starts with an honest applicability assessment rather than selling a full compliance program to businesses that may not need one, then builds exactly what your actual client relationships require.
Case Study: A Cairo Outsourcing Provider
- A Cairo-based outsourcing company handling customer service for a European retail client received a detailed GDPR due-diligence questionnaire from that client’s legal team and had no formal way to answer it.
- We assessed the company’s actual data handling and found genuine GDPR exposure, since staff were processing European customers’ names, order histories, and contact details daily, but there was no data processing agreement in place and no documented breach response procedure.
- Over two months, we mapped the data flows specific to that client relationship, drafted a data processing agreement and privacy policy, and implemented access controls limiting data visibility to only the staff who needed it for their role.
- The company answered its client’s questionnaire with genuine supporting documentation, retained the contract, and has since used the same framework to onboard two additional European clients without the same scramble.
Ready to Get Started?
If you’re serving European clients or considering it, we’ll help you honestly assess whether GDPR applies to your operations and build exactly what’s needed if it does. Book a free consultation or contact us to get started.
Frequently Asked Questions
It can. Article 3’s extraterritorial scope applies GDPR to any organization processing personal data of people located in the EU, regardless of where that organization is based.
No, GDPR compliance is demonstrated through documented policies and controls, not a certificate; there is no accredited “GDPR certification” scheme.
No, they’re separate legal frameworks; compliance with one doesn’t automatically satisfy the other, though the underlying data protection discipline supports both.
Most commonly, outsourcing and IT-enabled services providers handle data on behalf of European clients, and any business whose website or services directly target EU customers.
It depends on the number of EU client relationships, current documentation maturity, and data volume. We assess your specific situation before quoting.
Typically six weeks to four months, depending on how many distinct EU client data flows need to be mapped and documented.