ISO 27701 Certification in Egypt
Quick Answer
ISO 27701 certification extends an existing ISO 27001 information security management system to cover privacy information management specifically, verified by an independent, accredited certification body. It cannot be certified standalone; you need ISO 27001 in place first. In Egypt, this matters directly because of the PDPL: Executive Regulations issued in November 2025 established the Personal Data Protection Center as the active supervisory authority, and the licensing grace period ends October 31, 2026. ISO 27701 builds the specific privacy-management documentation, data subject rights handling, consent management, that PDPL licensing assumes exists. Certification typically takes two to four months on top of an existing ISO 27001 system.
Why ISO 27701 Matters in Egypt?
PDPL licensing explicitly requires demonstrable data subject rights handling : The Personal Data Protection Center, now the active supervisory authority under Executive Regulations issued November 2025, expects businesses to show genuine processes for consent, access requests, and data correction, exactly what ISO 27701’s Annex A structures.
The grace period is closing on a fixed calendar : Businesses have until October 31, 2026 to secure mandatory PDPL licenses, including specific licenses for cross-border transfers and electronic marketing, both of which involve privacy-specific handling beyond general information security.
Businesses acting as processors face a distinct compliance angle : Many Egyptian outsourcing and technology businesses process personal data on behalf of international clients rather than as the primary data controller, and Annex B’s processor-specific requirements map directly onto the contractual data processing agreements those clients increasingly require.
Privacy and security are related but not identical obligations : A business can hold excellent ISO 27001 security certification and still lack the specific consent management and data subject rights processes PDPL licensing and Annex A both expect.
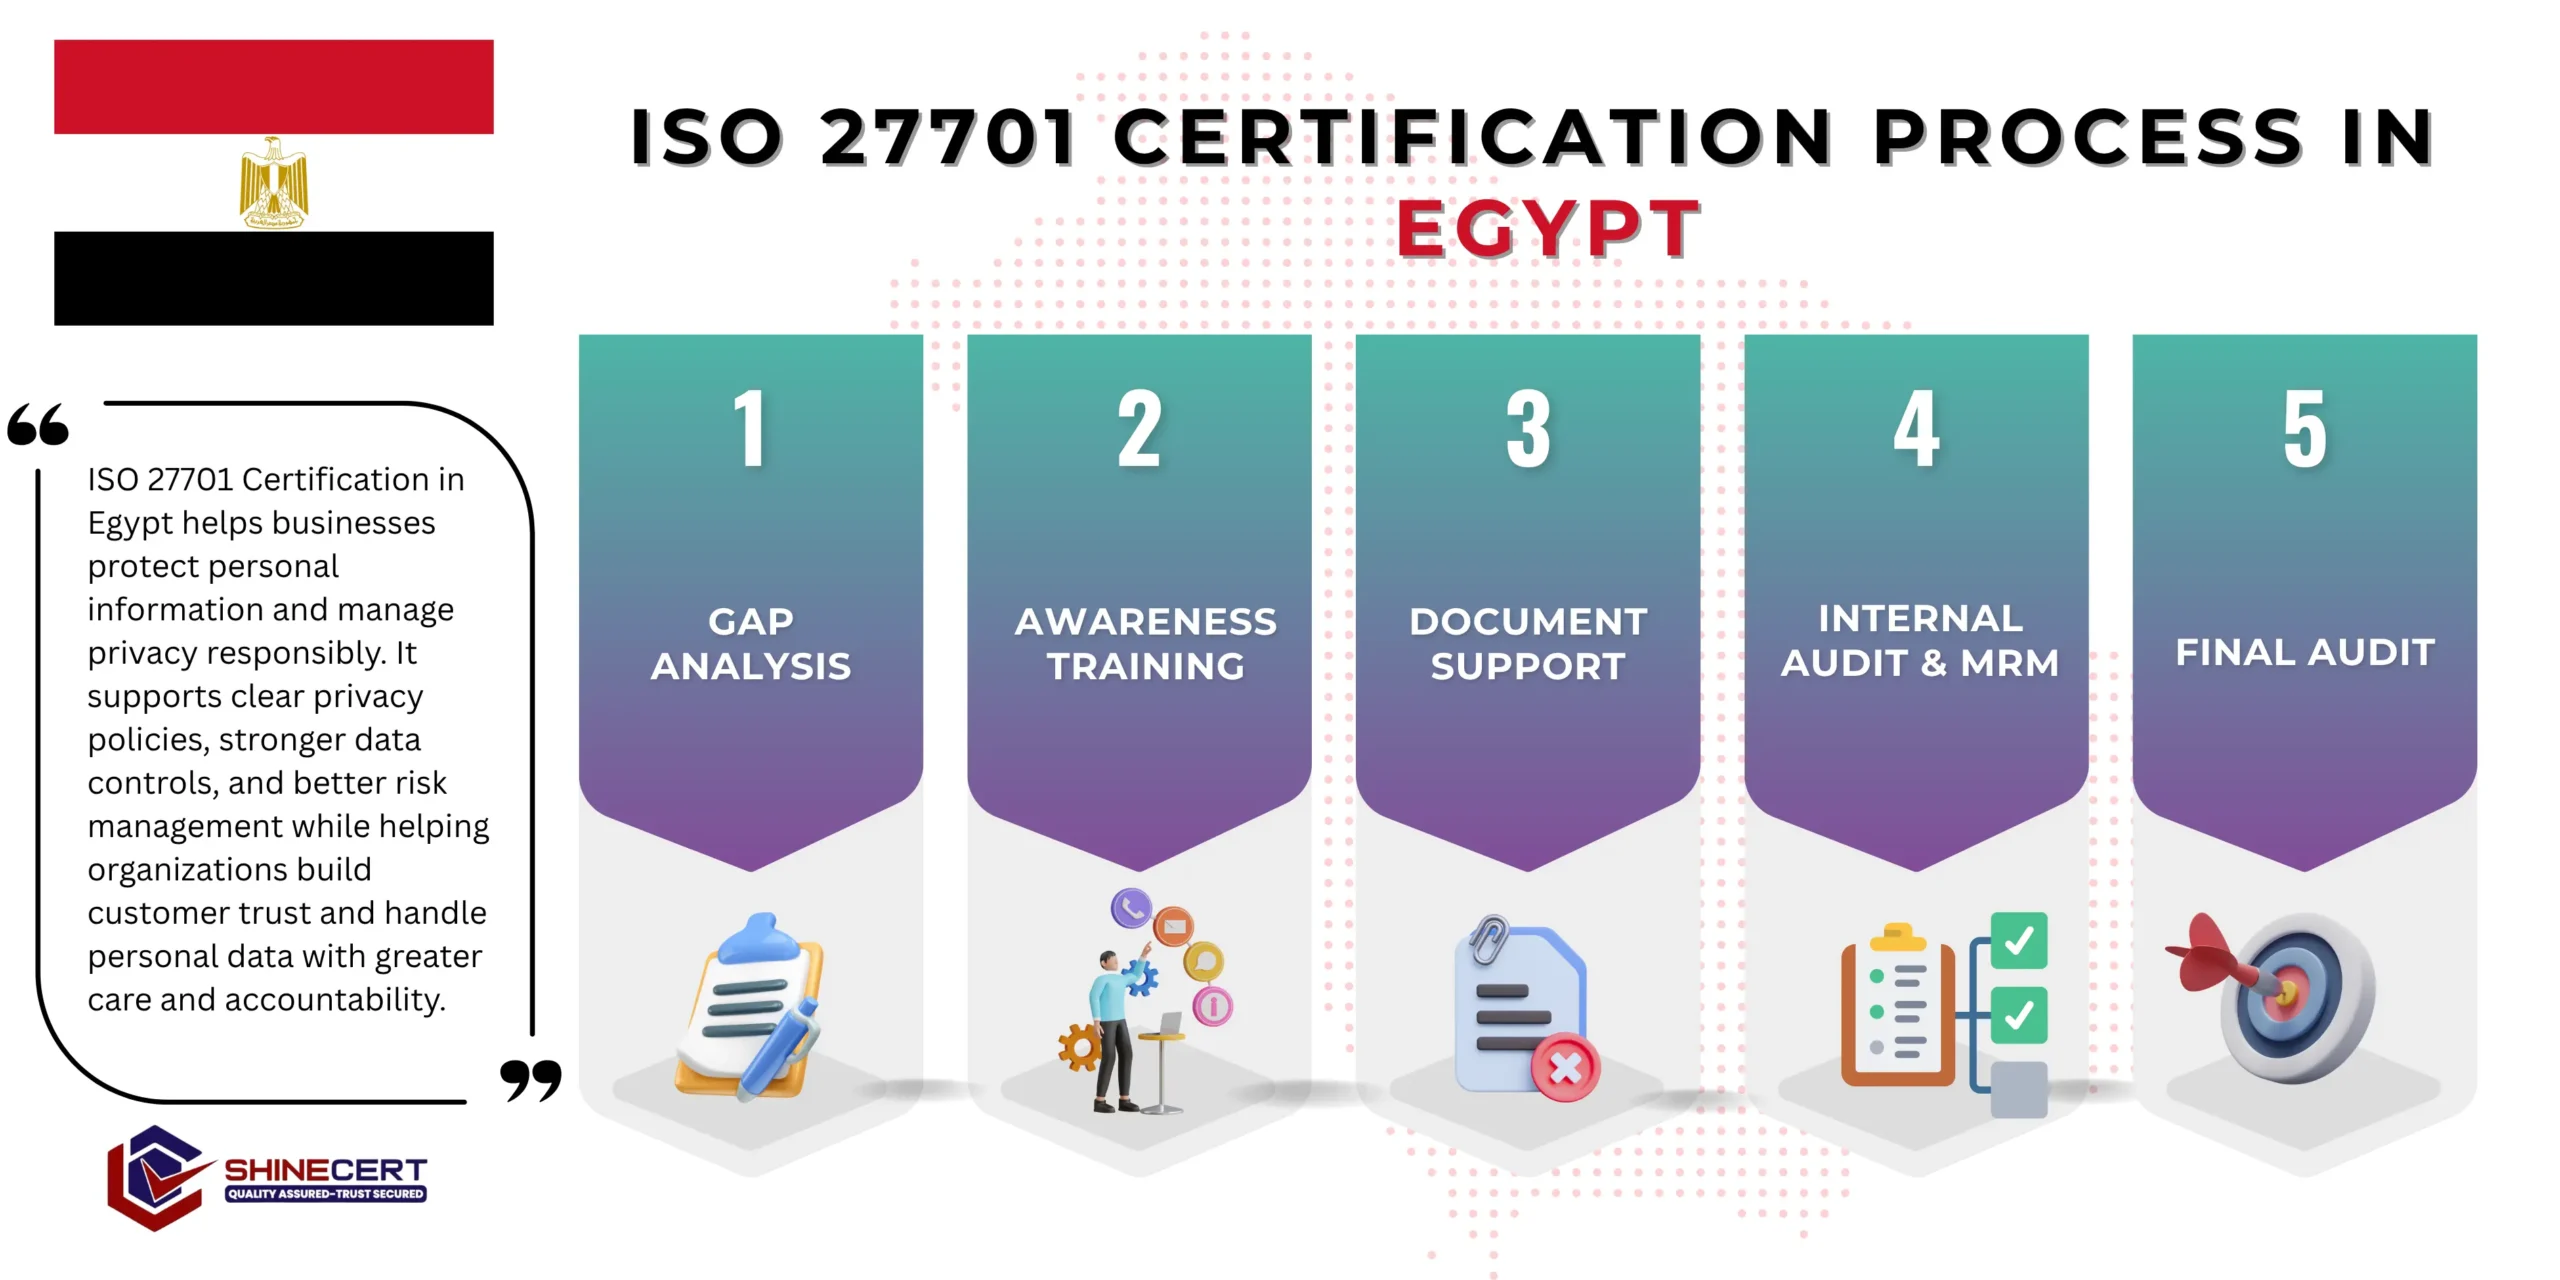
What are the steps to get ISO 27701 Certification in Egypt?
our services
- ISO Certification Egypt
- ISO 9001 Certification Egypt
- ISO 14001 Certification Egypt
- ISO 27001 Certification Egypt
- ISO 22000 Certification Egypt
- ISO 27701 Certification Egypt
- ISO 45001 Certification Egypt
- ISO 20000-1 Certification Egypt
- ISO 13485 Certification Egypt
- ISO 17025 Certification Egypt
- ISO 31000 Certification Egypt
- ISO 42001 Certification Egypt
- ISO 37001 Certification Egypt
- ISO 22301 Certification Egypt
- ISO 50001 Certification Egypt
- CE Mark Certification Egypt
- GDPR Certification Egypt
- GMP Certification Egypt
- Halal Certification Egypt
The ISO 27701 Certification Process in Egypt
Since ISO 27701 builds on an existing security system, the certification journey looks different from a first-time management system implementation.
Privacy Gap Mapping
We compare your existing ISO 27001 documentation against what ISO 27701 specifically requires for privacy, since good security controls don’t automatically cover consent and data subject rights.
Avoids duplicating security work you’ve already done while catching genuine privacy gaps.
A privacy-specific gap analysis.
Controller/Processor Determination
We establish whether you’re acting as a data controller, processor, or both across different client relationships, since this determines which annex governs your obligations.
Many businesses handle both roles simultaneously without realizing the distinction changes their obligations.
A clear determination mapped to each of your data relationships.
Privacy Documentation Build
We build consent management processes, data subject rights handling procedures, and, where you’re a processor, data processing agreement templates for client contracts.
This is the documentation PDPC licensing and international clients both specifically look for.
A complete privacy documentation set.
Rollout and Verification
Privacy processes go live, and we verify staff can actually execute a data subject access request or consent withdrawal end to end.
A documented process that nobody can execute under time pressure isn’t genuinely operational.
Verified, working privacy processes.
Extension Audit
Your certification body audits the privacy extension specifically and issues ISO 27701 certification alongside your existing ISO 27001 certificate.
This is the credential PDPL licensing and international clients both recognize.
Your ISO 27701 certification and an aligned surveillance schedule.
Privacy Gap Mapping
We compare your existing ISO 27001 documentation against what ISO 27701 specifically requires for privacy, since good security controls don’t automatically cover consent and data subject rights.
Avoids duplicating security work you’ve already done while catching genuine privacy gaps.
A privacy-specific gap analysis.
Controller/Processor Determination
We establish whether you’re acting as a data controller, processor, or both across different client relationships, since this determines which annex governs your obligations.
Many businesses handle both roles simultaneously without realizing the distinction changes their obligations.
A clear determination mapped to each of your data relationships.
Privacy Documentation Build
We build consent management processes, data subject rights handling procedures, and, where you’re a processor, data processing agreement templates for client contracts.
This is the documentation PDPC licensing and international clients both specifically look for.
A complete privacy documentation set.
Rollout and Verification
Privacy processes go live, and we verify staff can actually execute a data subject access request or consent withdrawal end to end.
A documented process that nobody can execute under time pressure isn’t genuinely operational.
Verified, working privacy processes.
Extension Audit
Your certification body audits the privacy extension specifically and issues ISO 27701 certification alongside your existing ISO 27001 certificate.
This is the credential PDPL licensing and international clients both recognize.
Your ISO 27701 certification and an aligned surveillance schedule.
What Is ISO 27701, Clause by Clause?
ISO 27701 doesn’t replace ISO 27001’s clause structure; it adds privacy-specific requirements on top of it, plus dedicated annexes for organizations acting as data controllers versus processors.
- Clauses 5-8 (extending ISO 27001): carry forward the context, leadership, planning, and support requirements from your existing information security system, extended to explicitly cover personal data and privacy risk, not just general security risk.
- Annex A (Controller-specific requirements): applies if your organization determines the purposes and means of processing personal data, covering consent management, data subject rights (access, correction, deletion), and privacy-by-design requirements for new products or processes.
- Annex B (Processor-specific requirements): applies if you process personal data on behalf of another organization, covering contractual obligations, limitations on data use, and support for the controller’s data subject rights obligations.
- Ongoing Operation: requires monitoring privacy-specific performance, including consent records and data subject request handling, alongside your existing ISO 27001 security monitoring.
What Does ISO 27701 Certification Cost in Egypt?
- Whether ISO 27001 is already in place : Businesses without an existing security management system need that foundation first, adding significantly to scope.
- Controller versus processor complexity : Businesses acting as controllers for their own customer data typically need more extensive consent and rights-handling infrastructure than pure processors working under a client’s instructions.
- Number of distinct data relationships : More client relationships, each potentially with different controller/processor arrangements, mean more documentation to build.
- Certification body fees : Typically lower as an extension audit than a full standalone certification, since much of the underlying system is already audited.
Benefits of ISO 27701 Certification
The consent and data subject rights documentation this certification builds is exactly what the PDPC licensing process expects to see.
Businesses stop guessing which privacy rules apply to which client relationship.
Clients increasingly require processor certifications like this before signing contracts involving personal data.
Structured consent and rights-handling processes catch gaps that pure security controls miss entirely.
Since it extends rather than duplicates your security system, the incremental cost and effort is meaningfully lower than a standalone certification.
How Long Does ISO 27701 Certification Take in Egypt?
| Business Situation | Typical Timeline | Why |
|---|---|---|
| Existing ISO 27001, simple data relationships | 2 months | Most groundwork already exists |
| Existing ISO 27001, multiple controller/processor relationships | 3 months | More documentation across different relationship types |
| No existing ISO 27001 | Add 3-5 months first | Security foundation must be built before the privacy extension |
What Documents Do You Need for ISO 27701 in Egypt?
- Foundation Documentation : Document: Existing ISO 27001 Statement of Applicability, extended to reference privacy-specific controls.
- Determination Documentation : Document: Controller/Processor Determination Record covering each data relationship.
- Controller Documentation (where applicable) : Document: Consent Management Records. Document: Data Subject Rights Handling Procedure.
- Processor Documentation (where applicable) : Document: Data Processing Agreement Templates. Document: Sub-processor Management Records.
- Ongoing Compliance : Document: Privacy Incident Records. Document: Privacy-Specific Internal Audit Reports.
Why Businesses Choose ShineCert in Egypt?
Businesses searching for the best ISO 27701 consultant in Egypt are usually trying to figure out exactly how much new work this really requires on top of existing security certification. We’ve spent 10 years helping more than 10,000 businesses worldwide get certified, coordinated through our Riyadh and India offices. We start by mapping precisely what your existing ISO 27001 system already covers, so you’re not paying to rebuild work that’s already done.
Case Study: A Cairo Fintech Platform
- A Cairo-based fintech platform holding ISO 27001 certification needed to demonstrate specific privacy compliance after a partner bank’s due-diligence process flagged the absence of formal consent management for customer financial data.
- Our gap mapping found the platform’s security controls were genuinely strong, but there was no documented consent withdrawal process, and customer data subject access requests had been handled informally on an ad hoc basis with no consistent response time.
- Over ten weeks, we determined the platform’s controller status for its own customer base, built a consent management system with clear withdrawal mechanics, and established a documented data subject rights response process with defined turnaround times. The extension audit passed with no nonconformities.
- The certification satisfied the partner bank’s due-diligence requirement, and the platform’s PDPL licensing application now references the same documentation directly.
Ready to Get Started?
If you already hold ISO 27001 and need to demonstrate specific privacy compliance ahead of Egypt’s PDPL licensing deadline, ShineCert will assess exactly what’s missing and give you a clear, honest quote. Book a free consultation or contact us to get started.
Frequently Asked Questions
No, ISO 27701 extends an existing ISO 27001 system; it cannot be certified standalone.
Not entirely; PDPL licensing is a separate legal process through the PDPC, but the documentation ISO 27701 builds directly supports that application.
It depends on your existing ISO 27001 status and data relationship complexity. We quote individually.
Usually two to four months if ISO 27001 is already in place; longer if it needs to be built first.
It depends on whether you determine the purposes of processing personal data yourself, or process it on another organization’s instructions; many businesses are both across different relationships.
Most of the documentation and verification work can be done remotely.