
ISO 37001 Certification in Angola
Quick Answer
ISO 37001 certification is an internationally recognized Anti-Bribery Management System credential confirming an organization has systematic controls in place to prevent, detect, and respond to bribery. In Angola it’s voluntary, verified through independent accredited audit, typically takes three to five months, and directly supports businesses navigating public procurement under the Public Contract Law and Angola’s active National Anti-Corruption Strategy.
About ISO 37001
ISO 37001 is the world’s leading anti-bribery management standard. It doesn’t guarantee an organization is bribery-free; it specifies how systematically you identify bribery risk, implement controls like due diligence and gift policies, and respond when concerns arise, through documented processes and independent verification.
Certification means an independent, accredited certification body has audited your actual anti-bribery controls, not just a written policy, and confirmed they genuinely meet the standard’s requirements. It’s reissued on a three-year cycle with annual surveillance audits in between.
A brief history of the standard : ISO 37001 was published in 2016, developed in response to growing international pressure for demonstrable anti-corruption compliance following high-profile bribery enforcement actions worldwide, including under laws like the US Foreign Corrupt Practices Act and the UK Bribery Act. It was one of the first ISO management standards written explicitly with a legal and compliance audience in mind, alongside traditional quality and operations management readers, reflecting how central anti-bribery due diligence had become to international business by the mid-2010s.
Why It Matters in Angola?
Angola has an active, documented anti-corruption push underway : The National Anti-Corruption Strategy, running 2024 to 2027, sets out government priorities for reducing corruption risk, with IGAE (the General Inspectorate of State Administration) and the PGR (Attorney General’s Office) both involved in oversight and enforcement. The Public Contract Law (41/20) and the National Public Procurement System (SNCP) govern how government contracts are awarded, and certified anti-bribery controls give you documented, auditable evidence relevant to this environment.
What not being certified actually costs you : Businesses without documented anti-bribery controls face greater scrutiny and slower processing in public procurement, and carry more exposure if a bribery allegation ever arises, with no internal controls to demonstrate good-faith prevention efforts. International partners and investors increasingly require anti-bribery due diligence evidence before entering into agreements. And the PGR has pursued significant asset recovery in recent years, reportedly linked to over three billion dollars in recovered assets between 2018 and 2022, signaling this isn’t an area of relaxed enforcement.
Why is this relevant in Angola right now? With the National Anti-Corruption Strategy actively running through 2027 and public procurement increasingly routed through the more transparent SNCP system, businesses bidding on government contracts or partnering with international investors are finding certified anti-bribery controls increasingly expected, not optional.
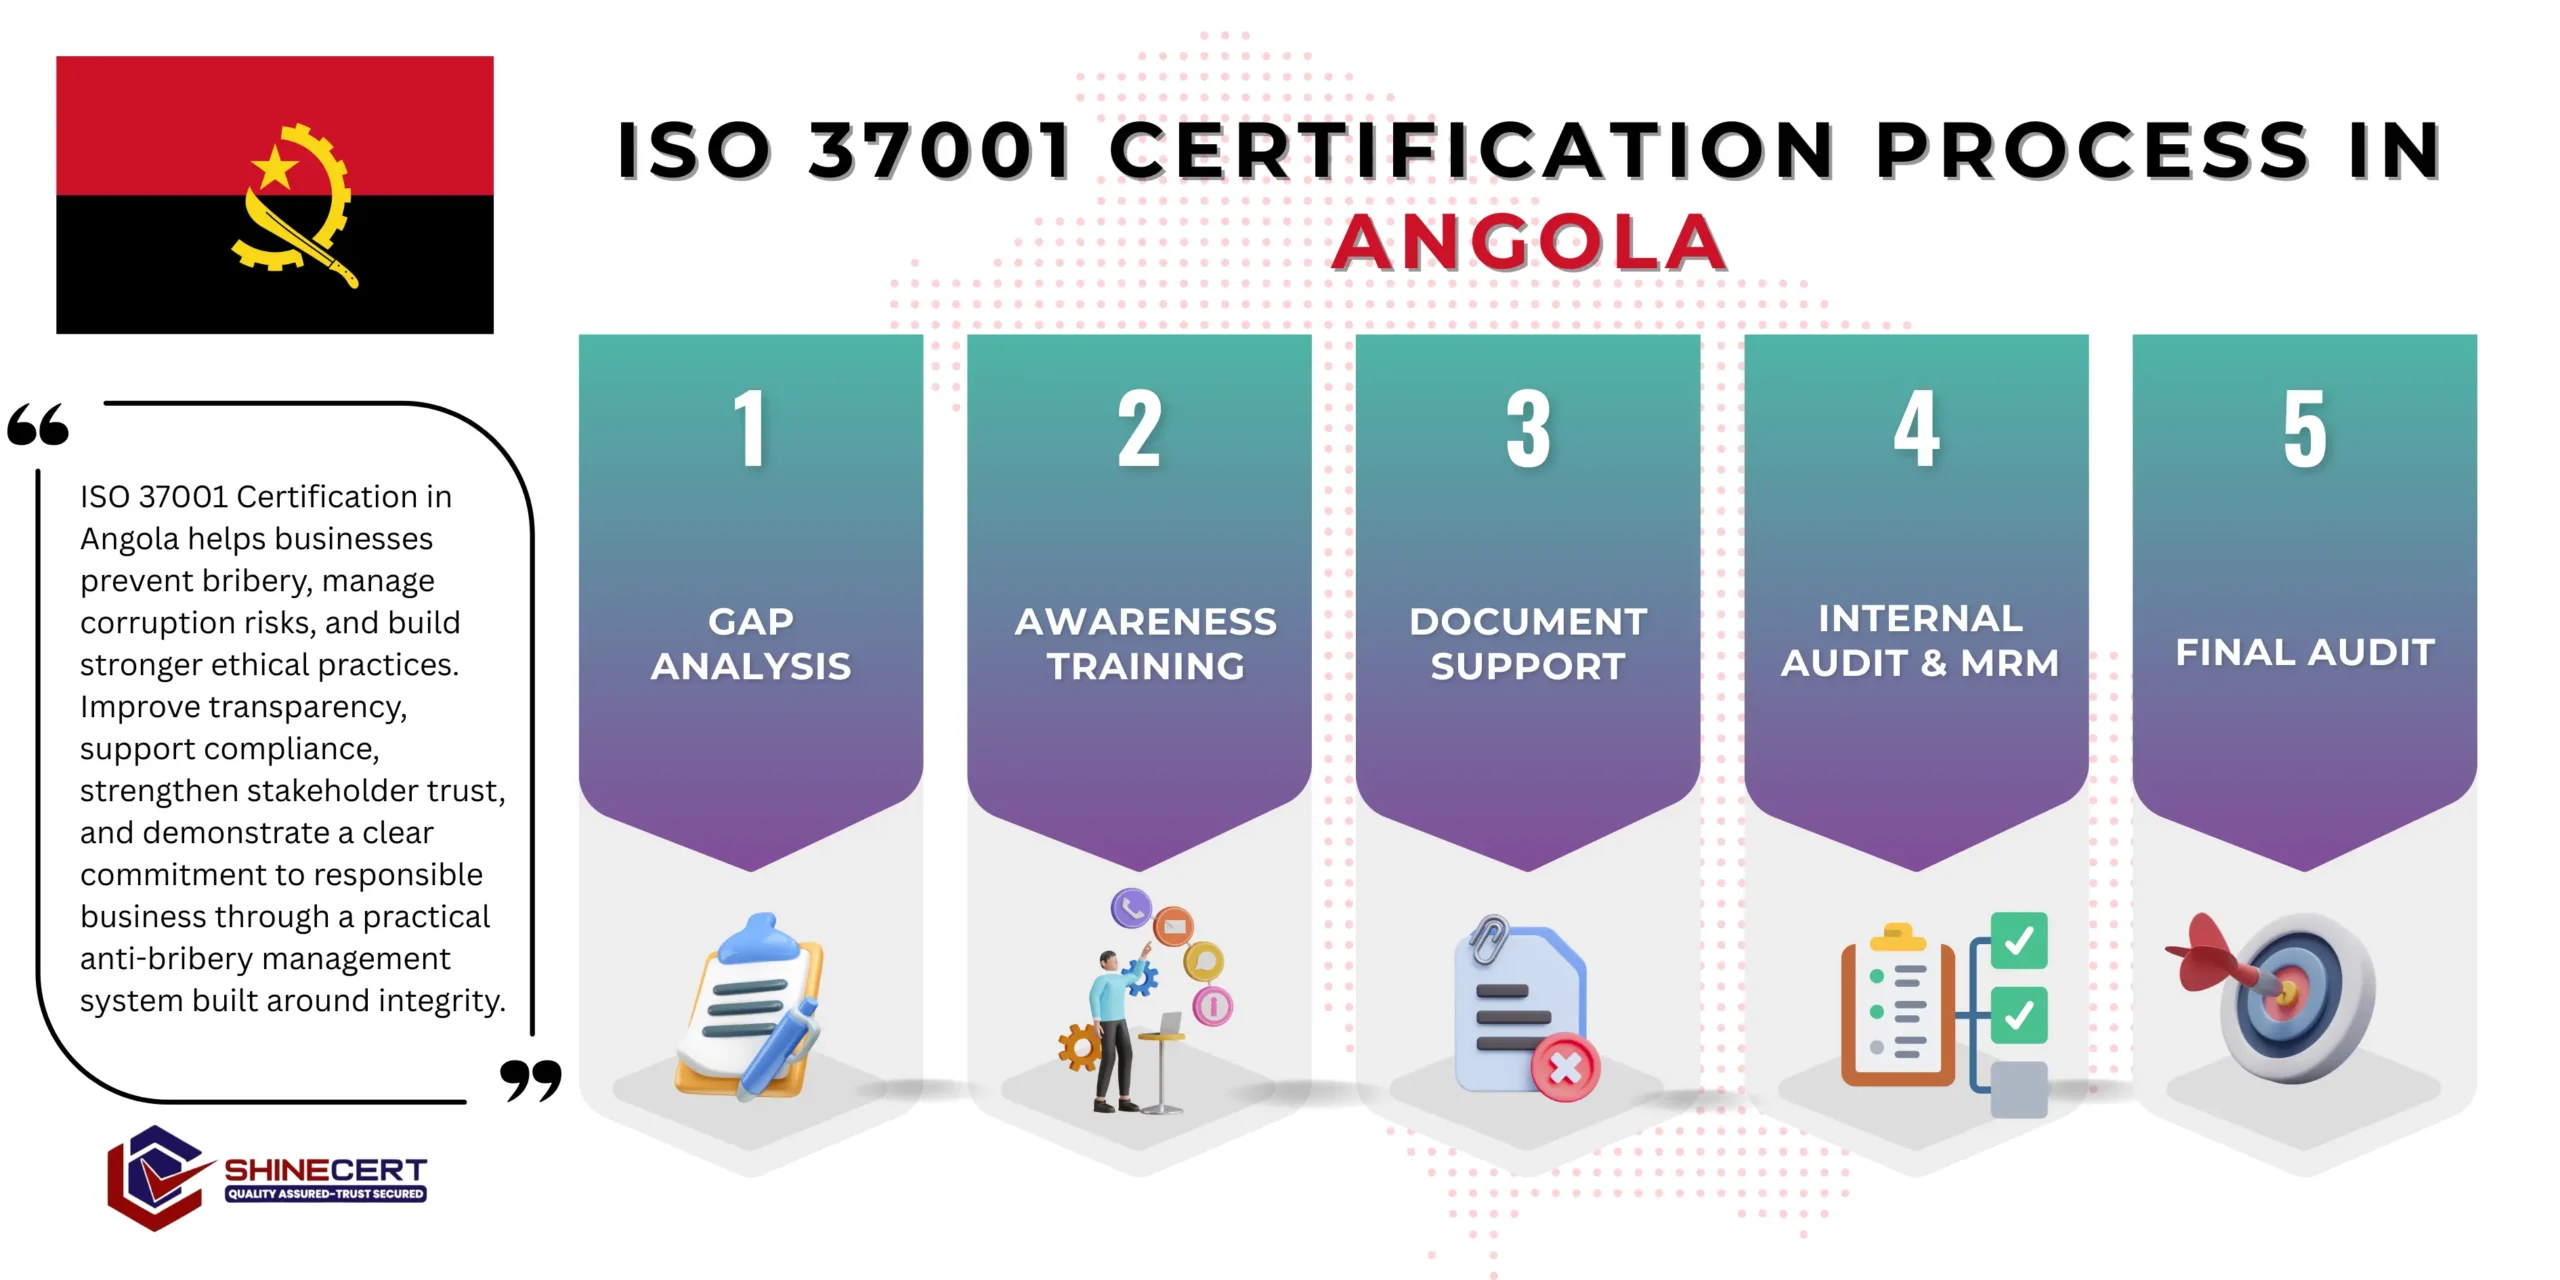
What are the steps to get ISO 37001 Certification in Angola?
our services
- ISO Certification Angola
- ISO 9001 Certification Angola
- ISO 14001 Certification Angola
- ISO 27001 Certification Angola
- ISO 22000 Certification Angola
- ISO 20000-1 Certification Angola
- ISO 45001 Certification Angola
- ISO 42001 Certification Angola
- ISO 13485 Certification Angola
- ISO 17025 Certification Angola
- ISO 31000 Certification Angola
- ISO 22301 Certification Angola
- ISO 27701 Certification Angola
- ISO 37001 Certification Angola
- ISO 50001 Certification Angola
- CE Mark Certification Angola
- GMP Certification Angola
- GDPR Certification Angola
- Halal Certification Angola
The Certification Process
Gap Assessment
Over one to two weeks, we review your current business relationships, government contract exposure, and any existing informal anti-bribery practices against the standard's requirements. You get an honest picture of where genuine bribery risk sits in your specific operations, government contracting, third-party agents, gift-giving practices, before any documentation begins.
Documentation Development
Over three to five weeks, we build your anti-bribery policy, bribery risk assessment, and due diligence procedures for business partners and third parties, grounded in your actual contract exposure rather than a generic compliance template.
Implementation and Training
Over three to six weeks, controls go live and staff, particularly those handling government contracts or third-party relationships, are trained on due diligence procedures and how to raise concerns. This phase requires genuine behavior change around gift-giving and third-party vetting practices.
Internal Audit and Management Review
Over two to three weeks, we run an internal audit against the same criteria the real auditor will use and complete a formal management review, catching documentation and control gaps before the external audit does.
Certification Audit
Over two to four weeks, an accredited certification body audits your actual anti-bribery controls, including due diligence records and any reporting mechanism, and issues the certificate once satisfied.
How Long Does Certification Take?
| Business Type | Typical Timeline | Why |
|---|---|---|
| Limited government or third-party exposure | 3 months | Fewer relationships to assess and document |
| Moderate exposure, some public contracts | 4 months | More due diligence and training coordination |
| Extensive public procurement or international dealings | 5 months | Broad third-party network requiring thorough due diligence |
- Businesses with limited government or third-party exposure (around 3 months) : Fewer external relationships mean a shorter due diligence process and a narrower risk assessment.
- Businesses with moderate exposure, including some public contracts (around 4 months) : More third-party relationships and some government contracting mean a broader due diligence exercise and more staff needing training.
- Businesses with extensive public procurement or international dealings (around 5 months) : These organizations typically have the widest network of third-party agents and government touchpoints, requiring the most thorough due diligence documentation.
- The variable that matters most: how many third-party relationships you actually have to vet : A business with a handful of direct government relationships moves through certification faster than one relying on multiple agents or intermediaries, each of whom needs individual due diligence documentation.
- A real example : A construction contractor we worked with had a dozen active subcontractor relationships, several involving government-adjacent work, but no formal due diligence records on any of them; building genuine due diligence documentation for each relationship, not a boilerplate check-box exercise, took an additional four weeks beyond the standard timeline, but this exact documentation is what auditors focus on most closely.
What Affects the Cost?
- Number of third-party and government relationships : More relationships requiring due diligence mean more documentation work.
- Current anti-bribery practice maturity : A business with existing informal controls starts from a stronger position.
- Extent of public procurement or international contract exposure : More exposure generally means a more thorough risk assessment is warranted.
- Certification body fees, separate from consulting costs.
Answering the Objections Every Owner Has
- We don’t pay bribes, so why do we need this? Certification isn’t an admission of a problem; it’s documented, independently verified evidence of the systematic controls that demonstrate genuine prevention, which matters significantly if an allegation ever arises regardless of your actual conduct.
- Isn’t this just paperwork? Only if implemented badly. Done properly, it documents due diligence and gift-handling practices you should already have in some form, structured so an auditor and a new employee can both follow them.
- We’re too small for this : Scope and cost scale with your contract exposure and risk profile, not the other way around, and smaller businesses often move through certification faster.
- Can’t we just write an anti-bribery policy ourselves? A policy alone rarely satisfies the standard’s due diligence, risk assessment, and internal reporting mechanism requirements, which are exactly what auditors scrutinize most closely.
Benefits of ISO 37001 Certification
- Stronger standing in public procurement under the Public Contract Law : Certification gives documented evidence of anti-bribery controls relevant to SNCP-routed tenders.
- Reduced exposure if a bribery allegation arises : Documented due diligence and controls matter significantly in demonstrating good-faith prevention efforts.
- Access to international partnerships requiring anti-bribery compliance evidence : Foreign investors and partners increasingly require this as a due diligence condition.
- Clearer internal accountability for anti-bribery controls : The standard requires defined roles and responsibilities, reducing ambiguity about who owns this risk area.
- Stronger reputation in a market under active anti-corruption reform : Certification signals genuine commitment in an environment where the government itself is prioritizing this issue.
- A foundation for integrating with ISO 9001 or ISO 27001 : These standards share complementary management-system structures.
Required Documentation
The scope statement defines exactly which business units and activities the certification covers. The anti-bribery policy sets top management’s genuine commitment, not generic compliance language.
The bribery risk assessment identifies where genuine risk sits in your specific operations, government contracting, agents, gift-giving. Due diligence procedures document how you vet business partners, agents, and third parties before engaging them.
Anti-bribery training records prove staff, particularly those handling government or third-party relationships, understand their responsibilities. The document control procedure keeps outdated anti-bribery procedures from circulating.
Gift, hospitality, and donation procedures document what’s permitted and what requires approval. The reporting and investigation procedure documents how bribery concerns are raised and investigated, one of the most scrutinized elements during an audit.
The internal audit program and reports and management review minutes demonstrate ongoing oversight of anti-bribery controls, not a one-time policy exercise.
Standards and Clauses: What ISO 37001 Actually Requires
- Context of the Organization (Clause 4) : requires identifying bribery risk issues relevant to your operations and understanding interested-party expectations, including government and international partner expectations.
- Leadership (Clause 5) : requires top management to set an anti-bribery policy and take visible ownership, with auditors specifically looking for evidence leadership genuinely champions the policy, not just signs it.
- Planning (Clause 6) : requires bribery risk assessment and planning actions to address identified risks, the clause underpinning your due diligence and control choices.
- Support (Clause 7) : covers competence, awareness, and documented information needed to run the system, including specific training for staff in higher-risk roles.
- Operation (Clause 8) : covers due diligence, financial controls, gift and hospitality management, and the reporting mechanism, the clause where most day-to-day anti-bribery documentation lives.
- Performance Evaluation (Clause 9) : requires monitoring anti-bribery performance, internal audits, and management review, checking whether controls are actually functioning.
- Improvement (Clause 10) : requires acting on nonconformities and continually improving the anti-bribery management system.
Case Study: A Construction Contractor Bidding on Public Infrastructure
- A construction contractor pursuing public infrastructure contracts routed through the SNCP system needed ISO 37001 certification to strengthen its position against competitors and satisfy an international co-financier’s due diligence requirement.
- Our gap assessment found the contractor had informal anti-bribery awareness but no documented risk assessment, no formal due diligence process for its subcontractors, and no reporting mechanism.
- Over four months, we built the bribery risk assessment, established due diligence procedures for the contractor’s subcontractor network, and set up a confidential reporting mechanism. The certification audit found no major nonconformities.
- The contractor secured its certificate and used it to satisfy the co-financier’s due diligence requirement ahead of the bid deadline.
Common Mistakes We See
- Writing an anti-bribery policy without a genuine risk assessment behind it : Auditors expect to see risk-based justification for your specific controls, not generic compliance language.
- Superficial due diligence on third parties : A checkbox exercise rather than genuine vetting is one of the most common findings during a certification audit.
- No functioning reporting mechanism : Staff need a genuine, safe way to raise concerns, not just a policy stating one exists.
- Choosing a certifier based on speed alone : An unusually fast timeline is often a shortcut on rigor, not efficiency.
Who Actually Needs This?
Construction and infrastructure contractors
frequently engaging with government contracts and public procurement.
Read moreBusinesses bidding on public tenders
routed through the SNCP system under the Public Contract Law.
Read moreCompanies seeking international investment or partnership
where anti-bribery due diligence is increasingly a prerequisite.
Read moreImport-export businesses
where cross-border transactions carry elevated bribery risk exposure.
Read moreWhich Certification Body Should You Choose?
Confirm the certification body holds recognized international accreditation. Be skeptical of unusually fast timelines given the due diligence depth the standard requires. Ask whether the consultant can explain how due diligence would work for your specific third-party relationships, not a generic compliance package. Confirm the audit reviews actual due diligence records, not just policy documents.
Choosing the Right Partner?
| DIY | Generic Consultant | ShineCert | |
|---|---|---|---|
| Risk assessment | Often incomplete | Templated, generic | Mapped to your actual contract and third-party exposure |
| Timeline realism | Often underestimated | Sometimes overpromised | Set to your real starting point |
| Angola regulatory alignment | Not considered | Rarely integrated | Built around Public Contract Law and SNCP context |
| Post-certification support | None | Ends at the certificate | Supports ongoing surveillance audits |
Why Businesses Choose ShineCert in Angola?
Across 10 years of ISO consulting and more than 10,000 organizations certified worldwide, coordinated through our Riyadh and India offices, we build anti-bribery systems with ShineCert as the best ISO 37001 consultant in Angola, grounded in Angola’s actual public procurement and anti-corruption reform context, not a generic compliance template.
Ready to Get Started?
Whether you’re strengthening your public procurement position or satisfying an international partner’s due diligence requirement, we’ll assess your real situation and give you a clear, honest quote. Book a free consultation or contact us to get started.
Frequently Asked Questions
No, but the National Anti-Corruption Strategy and Public Contract Law create a strong practical foundation certification that demonstrates alignment with more credibility.
It depends on the number of third-party and government relationships requiring due diligence. We quote individually.
Usually three to five months, depending heavily on how many third-party relationships need genuine due diligence documentation.
No, it demonstrates systematic, good-faith prevention controls, which matters significantly if an allegation ever does arise.
Construction, businesses bidding on public tenders, companies seeking international investment, and import-export businesses.
Most of the process can happen remotely; the certification audit may include a site visit depending on the certification body.
In 2016, developed in response to growing international pressure for demonstrable anti-corruption compliance.