
ISO 31000 Certification in Kenya
Quick Answer
ISO 31000 is not a certifiable standard, no auditor issues an ISO 31000 certificate, and any consultant offering one is selling something that doesn’t exist. What ISO 31000 actually is: internationally recognized guidance for building a structured risk management framework, and in Kenya’s genuinely volatile operating environment, where currency exposure, drought-linked power disruption, and compounding economic shocks can hit within a single quarter, that structure has real practical value. We help Kenyan businesses implement ISO 31000’s principles as an honest framework for identifying, assessing, and managing risk, not as a marketing credential.
Understanding ISO 31000
ISO 31000 is an international standard, published by the International Organization for Standardization, that provides principles and generic guidelines on risk management. Unlike management system standards such as ISO 9001 or ISO 27001, it is explicitly not intended for certification purposes, the standard itself states this. What it offers instead is a coherent framework for how an organization should approach risk: establishing context, identifying risks, analyzing and evaluating them, treating them, and continually monitoring and reviewing the whole process. Implementing ISO 31000 means building this framework into how your organization actually makes decisions, not producing a document to hang on the wall.
Why It’s Becoming Essential for Kenyan Businesses Right Now?
- Currency exposure genuinely affects a wide range of Kenyan businesses, not just importers and exporters : With a meaningful share of Kenya’s liabilities denominated in foreign currency and Kenyan Shilling volatility a persistent feature of the operating environment, businesses with foreign-currency supplier payments, loans, or receivables face genuine margin risk that a structured framework helps manage systematically rather than reactively.
- Compounding disruption chains are a genuinely distinctive feature of Kenya’s current risk landscape : Analysts have specifically flagged how drought can decimate agriculture, reduce hydropower generation, weaken the shilling, and strain consumer spending within a single quarter, traditional single-risk models struggle to capture this kind of cascading exposure, which is precisely what ISO 31000’s framework-based approach is built to address.
- A meaningful share of Kenyan firms are already increasing risk-related investment, and a structured framework prevents that spend from being scattered : With a substantial majority of Kenyan firms reportedly planning to increase security and risk-related budgets, ISO 31000 gives that investment a coherent structure rather than a series of disconnected point solutions.
- Kenya has an active professional risk management community that increasingly expects structured practice : The Institute of Risk Management Kenya chapter’s continued activity reflects a genuinely growing expectation among Kenyan business leaders that risk management be practiced as a discipline, not treated as an afterthought.
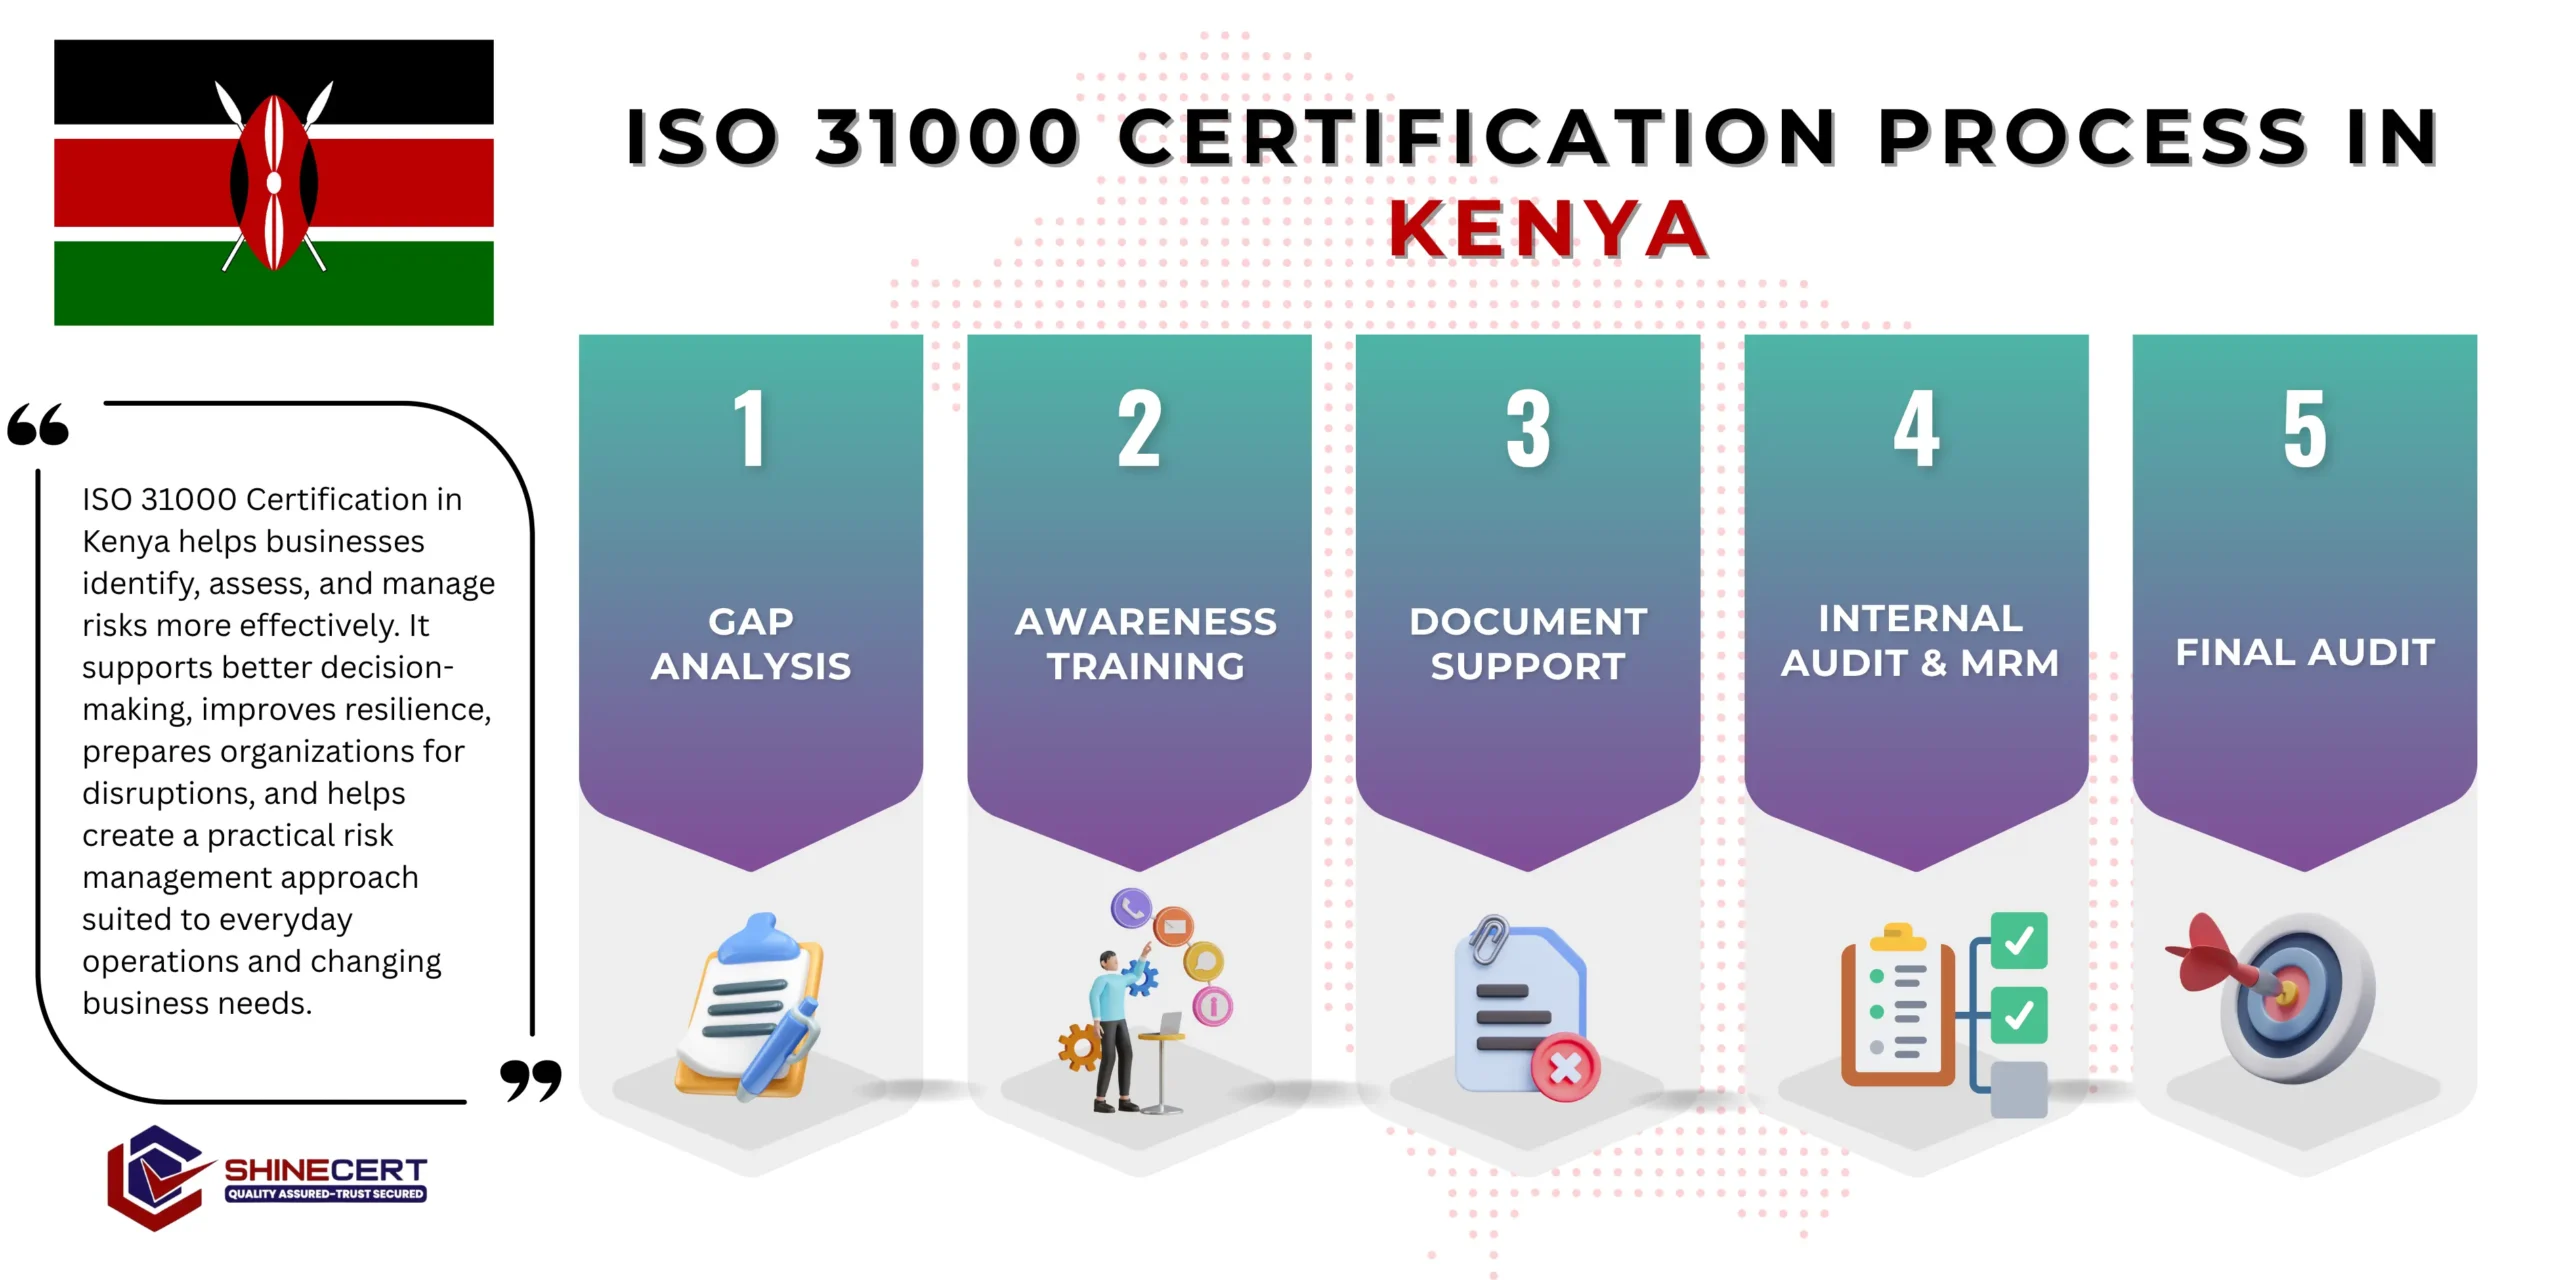
What are the steps to get ISO 31000 Certification in Kenya?
our services
- ISO Certification Kenya
- ISO 9001 Certification Kenya
- ISO 14001 Certification Kenya
- ISO 27001 Certification Kenya
- ISO 22000 Certification Kenya
- ISO 27701 Certification Kenya
- ISO 45001 Certification Kenya
- ISO 20000-1 Certification Kenya
- ISO 13485 Certification Kenya
- ISO 17025 Certification Kenya
- ISO 31000 Certification Kenya
- ISO 42001 Certification Kenya
- ISO 37001 Certification Kenya
- ISO 22301 Certification Kenya
- ISO 50001 Certification Kenya
- CE Mark Certification Kenya
- GDPR Certification Kenya
- GMP Certification Kenya
- Halal Certification Kenya
ISO 31000 Implementation Process in Kenya
Risk Landscape Assessment
We look at your actual operations, sector, and exposure, currency, supply chain, climate, regulatory, rather than starting from a generic risk checklist.
A risk landscape report specific to your business and Kenya’s current operating environment.
Framework Design
We design a risk management policy and governance structure sized to your actual organization, not an oversized framework built for a much larger business.
A documented risk management policy and clear ownership structure.
Risk Identification and Analysis
We work through your operations systematically, building a risk register that captures genuine likelihood and impact, including compounding risk chains relevant to Kenya’s environment.
A populated, prioritized risk register.
Treatment Planning
For your highest-priority risks, we build genuine treatment plans, not generic mitigation language, but specific, actionable steps.
Documented treatment plans tied to your actual risk register.
Embedding and Review
We help build risk review into your genuine decision-making cadence, whether that’s board meetings, management reviews, or operational planning cycles.
A functioning risk management framework with a review cadence your team will actually sustain.
Staying Current: Ongoing Review
Because ISO 31000 isn’t certifiable, there’s no surveillance audit cycle to maintain. What matters instead is genuine, ongoing use, a risk register that gets revisited quarterly at minimum, treatment plans that get updated as circumstances change, and leadership that continues treating risk management as a live discipline rather than a one-time project. We recommend a formal framework review annually, or sooner if your risk landscape shifts meaningfully, such as entering a new market or facing a major currency movement.
ISO 31000 Implementation Cost in Kenya
| Business Profile | Relative Investment Level | Why |
|---|---|---|
| Small business, single location | Lower | Narrower risk landscape and simpler framework |
| Medium business, moderate complexity | Moderate | Broader risk register across multiple risk categories |
| Larger or multi-site business | Higher | Extensive risk landscape across sites and business lines |
| Bundled with ISO 9001 or ISO 27001 | Moderate-to-higher combined, lower than separate engagements | Shared risk-thinking foundations reduce combined cost |
There’s no flat price for ISO 31000 implementation in Kenya, and because it’s not certifiable, there’s no certification body fee to factor in either, which genuinely changes the cost structure compared to certifiable standards. Cost comes down to six factors:
- Breadth of your risk landscape. A business with currency exposure, physical supply chains, and multi-site operations faces a genuinely broader risk register than a simpler operation.
- Existing risk management maturity : Businesses with informal but genuinely thoughtful risk practices already in place aren’t starting from zero.
- Number of stakeholders in governance : A framework spanning multiple departments or business units requires more coordination to design and embed.
- Depth of treatment planning required. High-priority risks needing genuinely detailed treatment plans take more time than lower-priority risks needing lighter documentation.
- Whether you’re bundling with a certifiable standard : Building ISO 31000 alongside ISO 9001 or ISO 27001 shares meaningful risk-thinking infrastructure, reducing combined cost.
- How deeply the framework needs to embed into decision-making : A framework meant to genuinely influence board-level and operational decisions requires more design work than a lighter documentation exercise.
Benefits of ISO 31000 Implementation for Kenyan Organizations
Kenyan organizations that genuinely implement ISO 31000 gain considerably more than a document sitting in a drawer. Here is what businesses genuinely gain:
A formal risk framework gives you a systematic way to assess and respond to shilling volatility rather than reacting only after margins are already affected.
Demonstrable, structured risk management is a genuine differentiator when engaging investors, lenders, or board members who expect mature governance.
Understanding how risks like drought, power disruption, and currency weakness interact lets you build contingency plans that address root causes rather than isolated symptoms.
ISO 31000’s risk-based thinking underpins the risk assessment clauses in ISO 9001, ISO 27001, and ISO 45001, making it a genuinely efficient starting point for organizations pursuing multiple certifications.
A structured framework helps ensure risk-related spending, including security and resilience investment, is genuinely prioritized rather than allocated reactively.
Insurers and lenders increasingly respond favorably to documented risk management practice when assessing terms.
When a disruption does occur, an organization with an established framework responds with a genuinely coordinated plan rather than an improvised one.
A Kenyan Business We’ve Worked With
- A Mombasa-based manufacturer importing raw materials for packaging production, selling primarily in Kenyan Shillings to domestic retailers, approached us after a particularly difficult quarter where shilling depreciation against the currencies used for their raw material purchases significantly compressed margins with no advance warning to leadership.
- Our risk landscape assessment found the business had genuinely sound operational practices but no formal mechanism for monitoring currency exposure or planning for its impact, decisions about pricing and procurement timing were made reactively, quarter to quarter.
- We built a risk register that specifically tracked currency exposure alongside their raw material supply chain risk, and a treatment plan that included forward-looking procurement timing and pricing review triggers tied to currency movement thresholds. The framework took about ten weeks to build and embed into their quarterly management review cycle.
- This reflects a pattern we see often, genuinely capable operational leadership that hadn’t yet built currency and supply risk into a structured decision-making process, rather than a single specific engagement.
Where Implementation Matters Most Across Kenya’s Economy?
Import and export businesses
Currency exposure is a genuinely direct, ongoing risk; ISO 31000 provides the structured framework to manage it systematically.
Read moreAgriculture and agro-processing
Drought, climate variability, and power reliability are genuinely direct operational risks; ISO 31000 addresses the compounding nature of these exposures.
Read moreManufacturing with imported inputs
Currency and supply chain risk compound directly; a structured framework helps manage both together rather than in isolation.
Read moreFinancial services and lending
Risk management is genuinely core to the business model; ISO 31000 principles complement sector-specific regulatory risk frameworks.
Read moreTechnology and Silicon Savannah businesses
Rapid growth and investor scrutiny make demonstrable risk governance a genuine differentiator when raising capital.
Read moreRealistic Timelines for Kenyan Businesses
| Business Profile | Typical Total Timeline | What Drives This |
|---|---|---|
| Small business, single location | 6–9 weeks | Narrower risk landscape and simpler governance structure |
| Medium business, moderate complexity | 9–14 weeks | Broader risk register and more stakeholders in governance |
| Larger or multi-site business | 14–20 weeks | Extensive risk landscape across sites, currencies, and business lines |
| Bundled with ISO 9001 or ISO 27001 | Add roughly 2-4 weeks to the relevant tier above | Shared risk-thinking foundations meaningfully shorten the combined path |
Beyond company size, the single biggest timeline driver is how many distinct risk categories genuinely apply to your business, a business with foreign-currency exposure, physical supply chains, and regulatory complexity takes longer than a simpler operation.
The Documentation a Genuine Framework Requires
A documented statement, endorsed by leadership, of your organization’s genuine commitment to structured risk management and its role in decision-making.
A living, actively maintained document identifying specific risks relevant to your operations, currency exposure, supply chain disruption, power reliability, regulatory change, with assessed likelihood and impact.
Documented plans for how identified risks are genuinely being addressed, whether through mitigation, transfer, acceptance, or avoidance.
Clear documentation of who owns which risk category and how escalation genuinely works within your organization.
Evidence that the risk register and treatment plans are genuinely revisited on a regular cadence, not created once and forgotten.
Documentation showing risk considerations are genuinely built into real business decisions, new market entry, major procurement, capital investment, rather than treated as a separate exercise.
The Real Challenges Organizations Face While Implementing ISO 31000
- Treating the risk register as a one-time exercise : A common gap is building a thorough risk register during initial implementation, then letting it go stale as circumstances genuinely change.
- Underestimating compounding risk chains : Businesses sometimes assess risks individually without considering how they interact, Kenya’s drought-hydropower-currency-consumer spending chain is a genuine example of exposure that single-risk thinking misses.
- Risk management staying separate from real decisions : The most common failure mode is a well-designed framework that never actually influences board or operational decision-making, existing as a parallel process rather than an embedded one.
- Confusing ISO 31000 with a certifiable standard : Some organizations approach ISO 31000 expecting a certificate at the end, and are genuinely surprised to learn implementation, not certification, is the actual deliverable.
Why Businesses Choose ShineCert in Kenya?
ShineCert brings 10 years of ISO consulting and certification experience to Kenya’s market, coordinated through our Riyadh and India offices with services delivered remotely or on-site depending on what your engagement genuinely needs. We’ve guided more than 10,000 organizations through ISO implementation and certification worldwide, and we’re upfront that ISO 31000 isn’t certifiable, this is why Kenyan businesses increasingly choose ShineCert as the best ISO 31000 consultant in Kenya for honest, genuinely useful risk framework implementation.
Choosing an Advisor in Kenya?
What to Check | Why It Matters |
Genuine transparency that ISO 31000 is not certifiable | A consultant offering an “ISO 31000 certificate” is misrepresenting the standard |
Real understanding of Kenya’s specific risk landscape | Currency, climate, and power-related risk chains require genuine local context, not generic risk templates |
Experience embedding frameworks into actual decision-making | The value is in genuine use, not documentation alone |
Sector-specific risk experience relevant to your business | Import-exposed manufacturing and financial services face genuinely different risk profiles |
Start Your Certification Journey
Whether you’re managing currency exposure, climate-linked disruption, or broader operational risk, we’ll walk through your specific risk landscape and cost factors before proposing a fixed-scope plan, delivered remotely, on-site, or however genuinely fits your project. Book a free consultation or contact us directly to get started.
Frequently Asked Questions
Look for a consultant upfront that ISO 31000 isn’t certifiable, with real Kenya-specific risk experience and transparent scoping. ShineCert scopes every Kenya engagement individually.
No, ISO 31000 is explicitly not intended for certification. Any consultant offering an ISO 31000 certificate is misrepresenting the standard. What we deliver is genuine framework implementation.
It genuinely depends on your risk landscape breadth, existing maturity, and how deeply the framework needs to embed into decision-making, we scope every project individually.
Typically six to twenty weeks depending on organization size and risk landscape complexity, see our detailed timeline breakdown above.
Yes, while currency risk is a genuinely common driver in Kenya, ISO 31000’s framework applies to any organizational risk category, including operational, regulatory, and reputational risk.
No, it’s a framework for identifying and managing risk systematically, which genuinely complements insurance and other transfer mechanisms rather than replacing them.
Framework design and documentation run effectively over remote sessions, though embedding the framework into real decision-making genuinely benefits from in-person workshops with your leadership team.
ShineCert doesn’t maintain a standalone Kenya office; we coordinate Kenya engagements from our Riyadh and India offices, with services delivered remotely or on-site as your project requires.