
ISO 27001 Certification in Kenya
Quick Answer
ISO 27001 is the international standard for information security management systems, and in Kenya it maps closely onto genuinely enforced legal obligations: the Office of the Data Protection Commissioner (ODPC) requires most data controllers and processors, businesses with turnover above KSh 5 million, more than 10 employees, or processing 10,000+ data subjects’ records annually, to register, and issued roughly 96-127 enforcement determinations in 2025 alone, bringing its cumulative total to around 357 determinations and 20 penalty notices. Non-compliance carries administrative fines up to KSh 5 million or 1% of annual turnover, and criminal penalties up to 10 years imprisonment for unregistered processing. Certification typically takes three to five months, and cost depends on real factors like data volume and systems complexity, never a flat number quoted upfront.
Understanding ISO 27001
ISO 27001 is an international standard, published by the International Organization for Standardization, that sets out requirements for an information security management system, a structured way an organization identifies information security risks, implements controls to manage them, and continually improves data protection. It covers the full range of information assets, from customer personal data to internal business systems, addressing people, process, and technology together. Certification means an independent, accredited body has formally verified your security management system meets the standard’s requirements, giving customers, regulators, and partners genuine confidence your organization protects data systematically, not just when the ODPC happens to be reviewing a complaint.
Why It’s Becoming Essential for Kenyan Businesses Right Now?
- ODPC registration is now a genuine, enforced legal obligation with real teeth, not a formality : Businesses meeting specific thresholds, annual turnover above KSh 5 million, more than 10 employees, processing sensitive personal data, or handling 10,000 or more data subjects’ records within a year, must register as data controllers or processors, with certificates valid for 24 months and renewable. Processing without registration, or continuing to process after a certificate expires, is a criminal offense carrying up to 10 years imprisonment or a fine up to KSh 3 million.
- ODPC’s enforcement activity has genuinely accelerated, not just expanded on paper : The ODPC issued roughly 96 to 127 formal determinations in 2025 alone, about double 2024’s volume, bringing its cumulative enforcement total to around 357 determinations and 20 penalty notices, a real, growing body of enforcement precedent Kenyan businesses now need to take seriously.
- The technical controls ODPC expects closely mirror what ISO 27001 already requires you to build : Kenya’s data protection regime, including draft Compliance Audit Regulations and a Data Sharing Code issued in December 2024, is explicitly aligning more closely with international standards like the EU’s GDPR, meaning the encryption, access control, and breach response practices ISO 27001 certification builds are directly relevant to demonstrating genuine ODPC compliance.
- Kenya’s data center and cloud infrastructure boom is raising the stakes for genuine security practice : With Kenya’s cloud and data-center capacity moving from basic colocation to genuine hyperscale facilities, and international technology companies expanding investment in Nairobi’s “Silicon Savannah,” Kenyan businesses handling data at increasing scale face genuinely higher security expectations from both regulators and international partners.
What are the steps to get ISO 27001 Certification in Kenya?
our services
- ISO Certification Kenya
- ISO 9001 Certification Kenya
- ISO 14001 Certification Kenya
- ISO 27001 Certification Kenya
- ISO 22000 Certification Kenya
- ISO 27701 Certification Kenya
- ISO 45001 Certification Kenya
- ISO 20000-1 Certification Kenya
- ISO 13485 Certification Kenya
- ISO 17025 Certification Kenya
- ISO 31000 Certification Kenya
- ISO 42001 Certification Kenya
- ISO 37001 Certification Kenya
- ISO 22301 Certification Kenya
- ISO 50001 Certification Kenya
- CE Mark Certification Kenya
- GDPR Certification Kenya
- GMP Certification Kenya
- Halal Certification Kenya
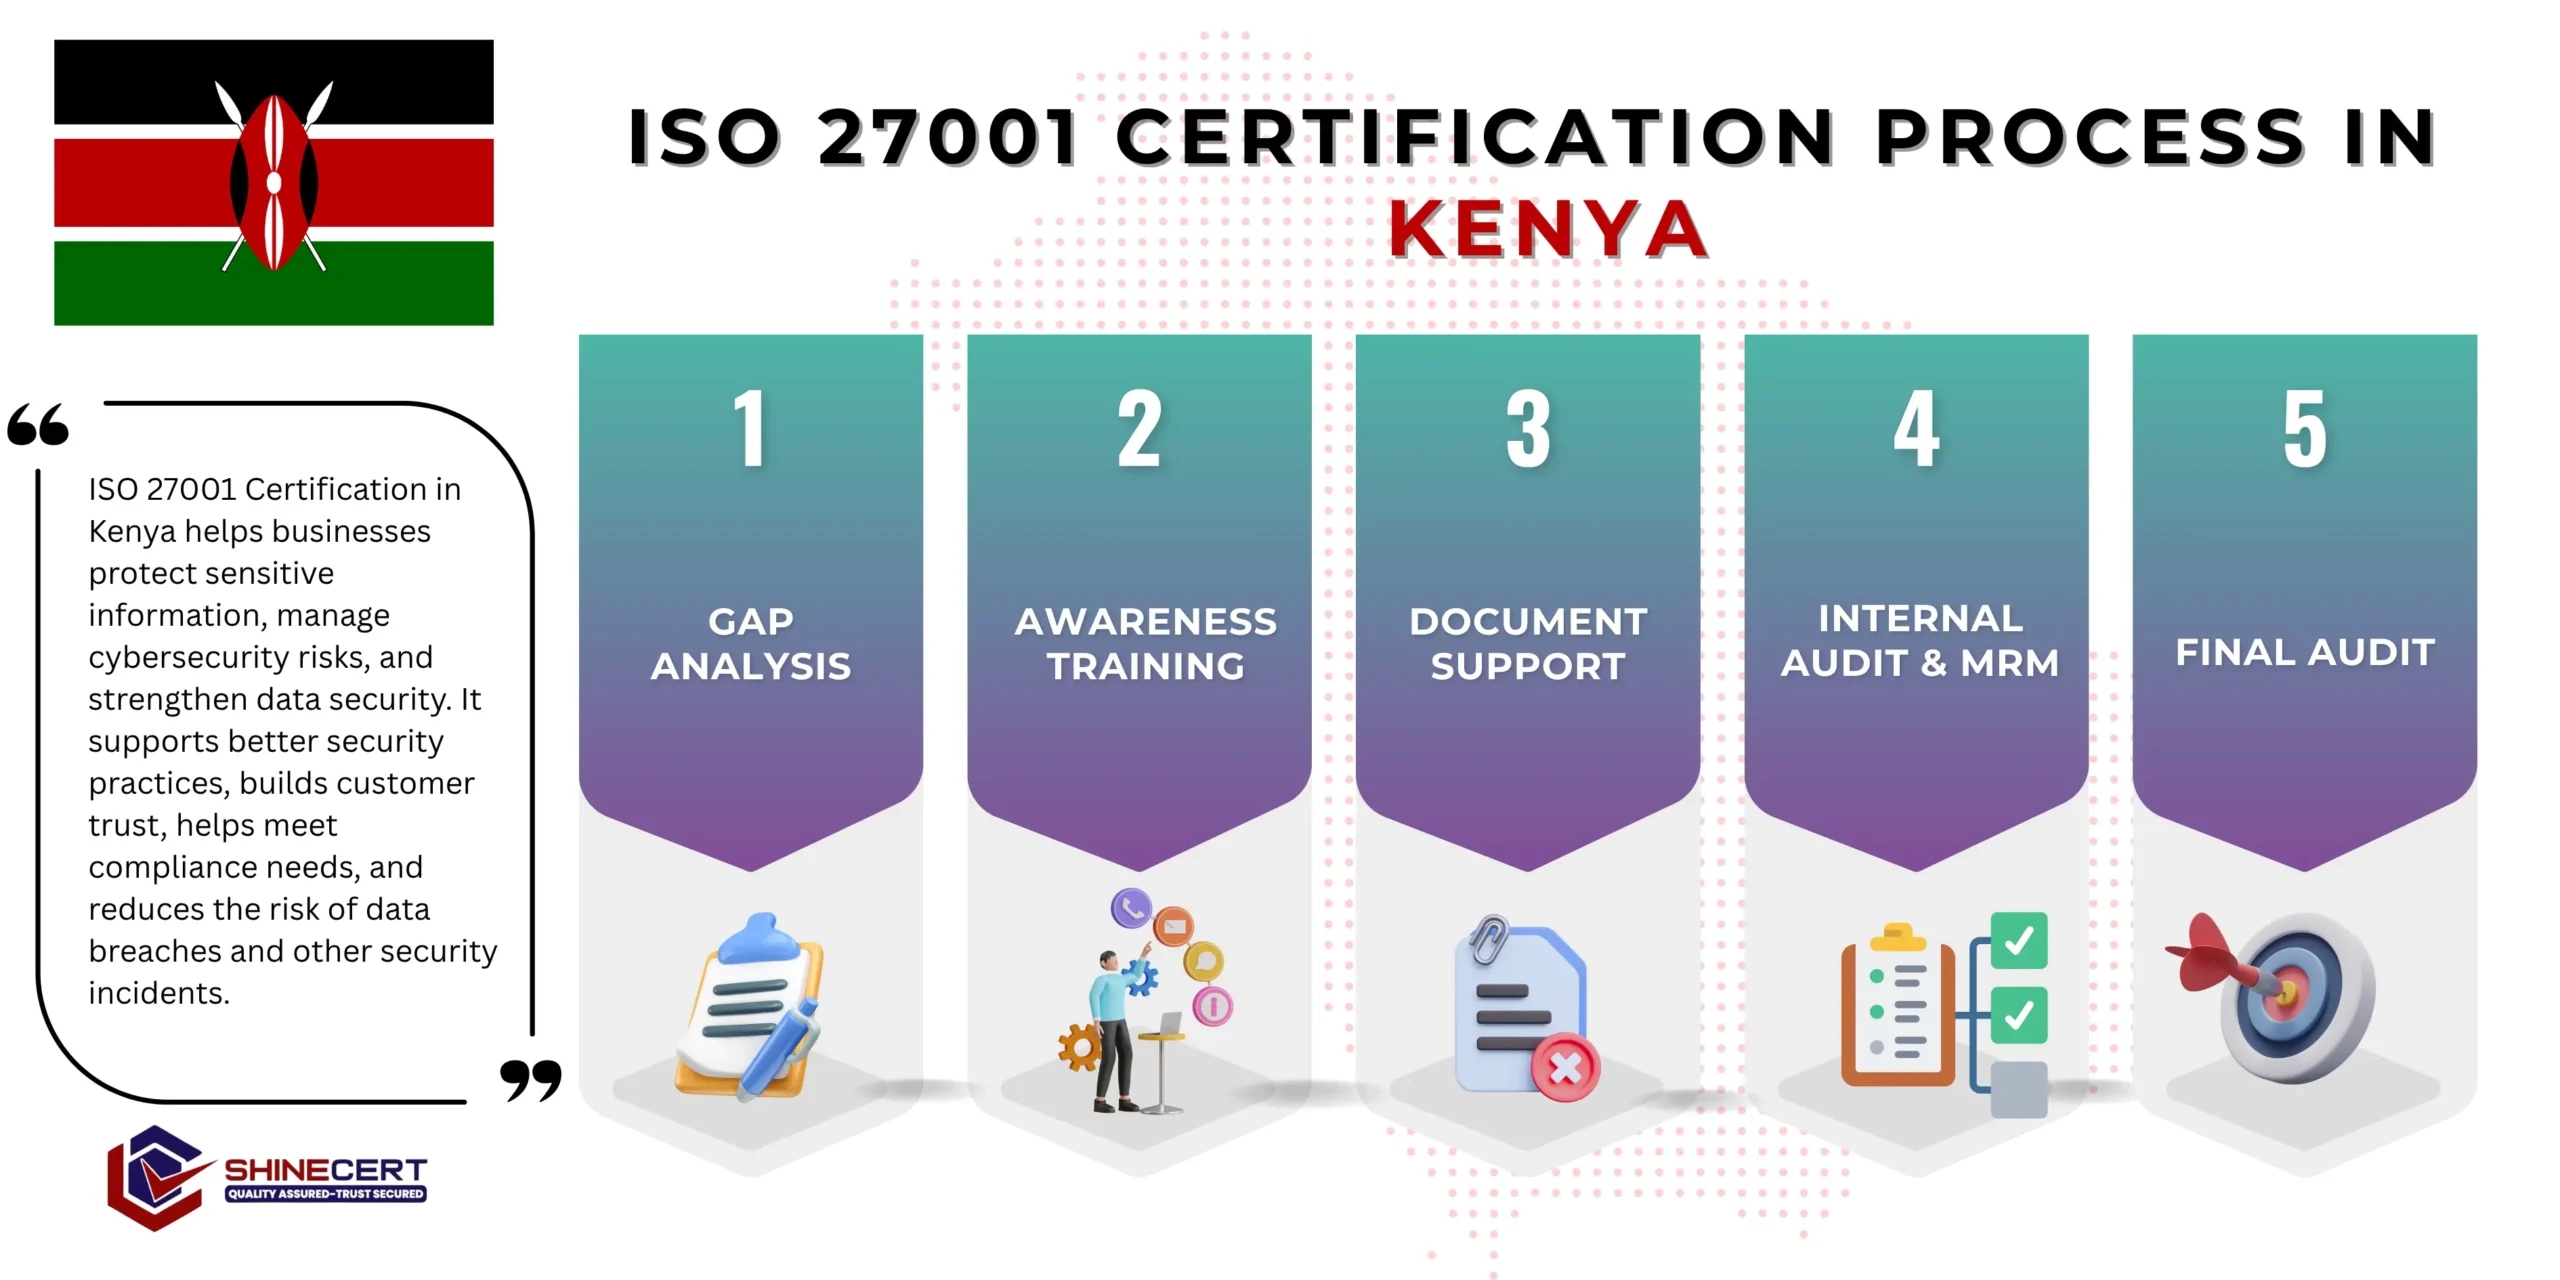
ISO 27001 Certification Process in Kenya
Gap Assessment
We review your current systems, data flows, and existing security practices against both ISO 27001’s requirements and your genuine ODPC registration status, since building toward both simultaneously avoids duplicated effort later.
A gap report mapping your actual security posture against ISO 27001 requirements and your ODPC compliance status side by side.
Documentation
We build your ISMS policy, risk assessment methodology, and Statement of Applicability around your organization’s genuine data footprint, a fintech handling payment data has a meaningfully different risk profile than a professional services firm.
A complete ISMS documentation set, including a Statement of Applicability with real, defensible justifications.
Implementation
Technical controls, access management, encryption, network segmentation, and organizational controls move into genuine daily operation, with staff trained on their specific responsibilities.
A functioning ISMS with real controls operating, not just documented.
Internal Audit and Management Review
We audit against every ISO 27001 clause and Annex A control, and cross-check against ODPC obligations specifically, surfacing gaps while stakes are low.
An internal audit report and corrective actions closed out before the certification audit.
Certification Audit
Stage 1 confirms your ISMS documentation is genuinely audit-ready; Stage 2 verifies controls are actually operating as documented. We stay engaged through both stages.
Your ISO 27001 certificate, valid for three years, plus a surveillance audit schedule.
Staying Certified: Surveillance and Renewal
An ISO 27001 certificate is valid for three years. During years one and two, your certification body conducts an annual surveillance audit, narrower in scope, sampling a portion of your controls. Before the three-year mark, a full recertification audit confirms your ISMS has continued functioning throughout the cycle, including that your risk assessment and Statement of Applicability were kept genuinely current. Passing recertification issues a new three-year certificate. Note this runs independently of your ODPC registration certificate, which is valid for 24 months and needs separate renewal.
ISO 27001 Certification Cost in Kenya
| Business Profile | Relative Investment Level | Why |
|---|---|---|
| Small, single-system operation | Lower | Narrower asset inventory, fewer applicable controls |
| Medium, multiple-systems operation | Moderate | Broader risk assessment and control implementation scope |
| Larger, multi-department operation with sensitive data | Higher | Extensive systems mapping and complex access management |
| Bundled with a second standard | Moderate-to-higher combined, lower than separate engagements | Shared implementation infrastructure reduces combined cost |
There’s no flat price for ISO 27001 certification in Kenya. Cost genuinely comes down to six factors:
- Nature of business and data sensitivity : A fintech or healthtech handling sensitive personal or financial data faces a genuinely more extensive risk assessment than a business handling limited, low-sensitivity data.
- Number of systems and data flows : Each additional system, application, or third-party integration expands the asset inventory and risk assessment work.
- ODPC registration category : Businesses meeting higher registration thresholds under the Data Protection Act typically face broader corresponding ISO 27001 scope.
- Existing security maturity : Businesses with some documented security controls already in place aren’t starting from zero.
- Certification body fees, tracked separately from our consulting fees. The certification audit itself is invoiced directly by the accredited certification body.
- Whether you’re bundling standards : Building ISO 27001 alongside ISO 27701 or ISO 9001 shares meaningful implementation infrastructure, reducing combined cost.
Benefits of ISO 27001 Certification for Kenyan Organizations
Kenyan organizations that complete certification gain considerably more than a document proving security compliance. Here is what certified businesses genuinely gain:
Because ISO 27001’s control requirements substantially overlap with what the ODPC expects technically, certified organizations find registration renewal and any compliance audit considerably more straightforward.
Systematic risk assessment and layered controls meaningfully reduce the likelihood of a breach that could trigger ODPC’s administrative fines or criminal liability provisions.
ISO 27001 is understood and trusted globally, giving Kenyan businesses, particularly in fintech and BPO, a credential that satisfies international client due diligence directly.
A documented incident response process makes meeting ODPC notification expectations realistic rather than a genuine scramble under pressure.
Financial services, government-adjacent, and international outsourcing contracts increasingly list information security certification as a genuine evaluation criterion.
Demonstrable, independently verified security practice is a genuine differentiator in sectors handling sensitive personal or financial data.
ISO 27001 requires genuinely identifying the specific security risks your actual systems and data flows face, not generic threats, and building real, prioritized controls.
ISO 27001’s Harmonized Structure and its natural extension, ISO 27701, make pursuing additional privacy-specific certification considerably more efficient once the core ISMS is in place.
The standard requires assessing security risk in your supply chain, an area many Kenyan organizations manage informally until a certified system forces genuine structure onto it.
A Kenyan Business We’ve Worked With
- A Nairobi-based mobile lending platform approached us after crossing the ODPC’s registration threshold as their user base grew past 10,000 data subjects, triggering a mandatory registration obligation the business hadn’t previously had to navigate, and prompting genuine concern about whether their existing security practices could withstand real regulatory scrutiny.
- Our gap assessment found the engineering team had implemented reasonably solid technical controls already, but there was no formal risk assessment, no Statement of Applicability, and no documented incident response procedure, meaning a real breach would have found the organization improvising rather than executing a rehearsed plan.
- We built the ISMS documentation directly around their existing technical controls, considerably shortening implementation.
- Certification took just under four months, and the Statement of Applicability became the direct backbone of their ODPC registration renewal submission.
- This reflects a pattern we see often, strong technical security undermined by a lack of documented, auditable structure, rather than a single specific engagement.
Where Certification Matters Most Across Kenya’s Economy?
Fintech and mobile money platforms
ISO 27001 is close to essential given the sensitive financial data these businesses handle; pair with ISO 27701 for privacy management given direct ODPC exposure.
Read moreBusiness process outsourcing and IT services
ISO 27001 is frequently a genuine client contractual requirement given international client data processed; pair with ISO 9001 for service quality.
Read moreHealthtech and health data platforms
ISO 27001 addresses genuinely sensitive health data risk; pair with ISO 13485 if the business also handles medical devices.
Read moreBanking and financial services
ISO 27001 addresses core information security risk; pair with ISO 22301 for business continuity.
Read moreTelecommunications
ISO 27001 addresses substantial customer data risk; pair with ISO 20000-1 for IT service management.
Read moreE-commerce and digital platforms
ISO 27001 addresses payment and customer data risk central to this sector’s trust; pair with ISO 9001 for service quality.
Read moreRealistic Timelines for Kenyan Businesses
| Business Profile | Typical Total Timeline | What Drives This |
|---|---|---|
| Small, single-system operation | 2.5–3.5 months | Narrower asset inventory and simpler risk landscape |
| Medium, multiple-systems operation | 3.5–5.5 months | Broader risk assessment scope, more Annex A controls applicable |
| Larger, multi-department operation with sensitive data | 5.5–8 months | Extensive systems mapping, complex access control requirements |
| Bundled with a second standard | Add roughly 3-5 weeks to the relevant tier above | Shared documentation infrastructure meaningfully shortens the combined path |
Beyond company size, the single biggest timeline driver is how well-documented and centralized your existing IT systems and data flows already are.
The Documentation ODPC and Auditors Expect
A documented statement defining which systems, data, and business units the information security management system covers, aligned with your actual data processing footprint under the Data Protection Act.
A documented policy, approved by top management, expressing genuine commitment to protecting information assets and complying with applicable legal requirements including ODPC registration.
A documented, actively maintained process for identifying information security risks and recording the controls chosen to treat each one.
A document mapping every Annex A control to whether it applies to your organization, with genuine justification for any exclusions.
A documented list of applicable requirements, Data Protection Act 2019 obligations, ODPC registration status, sector-specific regulations, along with evidence of how each is being met.
Documentation and evidence of role-based access controls ensuring personal data is genuinely accessible only to those with a legitimate business need.
A documented procedure for detecting, reporting, and responding to security incidents, including internal steps supporting ODPC notification expectations.
Documented, tested backup and recovery procedures demonstrating your organization can genuinely restore data after a disruptive incident.
A planned internal audit cycle and documented management review decisions on security priorities and resourcing.
The Real Challenges Organizations Face While Implementing ISO 27001
- Underestimating the documentation requirement beyond technical controls : Businesses with genuinely strong technical security sometimes underestimate how much formal risk assessment and documentation ISO 27001 actually requires beyond firewall configuration and access controls alone.
- Treating the risk assessment as a one-time exercise : A common gap is completing the risk assessment for certification and never genuinely revisiting it as new systems, vendors, and data flows are introduced.
- Weak justification in the Statement of Applicability : Auditors specifically probe excluded controls for genuine justification, an excluded control without real reasoning is a common, avoidable finding.
- Security practice drifting after initial certification : New applications get adopted without going through access control or risk assessment review, and the asset inventory quietly falls out of date.
Why Businesses Choose ShineCert in Kenya?
ShineCert brings 10 years of ISO consulting and certification experience to Kenya’s market, coordinated through our Riyadh and India offices with services delivered remotely or on-site depending on what your engagement genuinely needs. We’ve guided more than 10,000 organizations through ISO certification worldwide, and we build every Kenya engagement around your actual systems and ODPC registration status, not a generic template, this is why data-driven Kenyan businesses increasingly choose ShineCert as the best ISO 27001 consultant in Kenya.
Choosing a Certification Body in Kenya?
What to Check | Why It Matters |
Accreditation under a recognized international accreditation framework | Confirms genuine, internationally recognized certification |
Genuine familiarity with Kenya’s Data Protection Act and ODPC framework | Ensures the auditor understands how your ISMS connects to your actual regulatory obligations |
Experience with your specific sector’s data risk profile | Fintech, healthtech, and BPO involve genuinely different data sensitivity levels |
A genuine technical-controls-verification audit approach | Confirms the auditor checks real system configuration, not just documentation |
Start Your Certification Journey
Whether you’re responding to a new ODPC registration obligation or strengthening security proactively, we’ll walk through your specific systems and cost factors before proposing a fixed-scope plan, delivered remotely, on-site, or however genuinely fits your project. Book a free consultation or contact us directly to get started.
Frequently Asked Questions
Look for genuine familiarity with the Data Protection Act and ODPC compliance framework, sector-specific data risk experience, and transparent scoping rather than flat package pricing. ShineCert scopes every Kenya engagement individually.
Not automatically, but the overlap is substantial, a certified ISMS gives you most of the documentation and technical controls ODPC expects, considerably simplifying registration and any compliance review.
It genuinely depends on your systems complexity, data sensitivity, and ODPC registration category, we scope every project individually.
Typically two and a half to eight months depending on organization size and systems complexity, see our detailed timeline breakdown above.
ODPC registration and ISO 27001 certification are separate but complementary, certification gives you a genuinely stronger, internationally recognized foundation for meeting your registration obligations consistently.
Certification means your organization has a documented, tested incident response process, meaningfully improving your ability to respond and demonstrate accountability to the ODPC.
Much of the documentation and risk assessment work runs effectively over remote sessions, though certain technical verification benefits from on-site presence.
ShineCert doesn’t maintain a standalone Kenya office; we coordinate Kenya engagements from our Riyadh and India offices, with services delivered remotely or on-site as your project requires.