
ISO 27701 Certification in Kenya
Quick Answer
ISO 27701 extends ISO 27001 with specific requirements for a privacy information management system, and Kenya’s 2026 enforcement environment gives it real practical weight. The Office of the Data Protection Commissioner (ODPC) has issued 184 compensation orders to Kenyans whose data was mishandled, a genuine milestone enforcement action, against a backdrop of over 9,000 complaints received since the Data Protection Act, 2019 took effect. ISO 27701 requires an existing or simultaneously built ISO 27001 foundation, then adds privacy-specific controls covering consent management, data subject rights, and cross-border transfer safeguards that map directly onto what the Data Protection Act expects. Certification typically takes four to seven months, and cost depends on real factors like whether ISO 27001 is already in place.
Understanding ISO 27701
ISO 27701 is an international standard, published by the International Organization for Standardization, that extends ISO 27001’s information security management system with specific requirements for managing personal data as a privacy information management system. It cannot be certified standalone, it requires an existing or simultaneously implemented ISO 27001 certification as its foundation, then layers on privacy-specific controls: how you manage consent, respond to data subject access requests, handle cross-border data transfers, and demonstrate accountability for personal data processing. Certification means an independent, accredited body has formally verified both your underlying security controls and your privacy-specific management practices meet the standard’s requirements.
Why It’s Becoming Essential for Kenyan Businesses Right Now?
- ODPC’s 184 compensation orders mark a genuine shift from a developing regulator to an actively enforcing one : This milestone enforcement action, alongside 357 cumulative determinations, 134 enforcement notices, and 20 penalty notices issued since the Data Protection Act took effect, shows Kenyan businesses that mishandled personal data now carries genuine financial and reputational consequences, not just theoretical regulatory risk.
- The Data Protection (Amendment) Bill 2025 proposes requiring organizations to demonstrate ongoing compliance, not just implement it once : Under the proposed amendments, data controllers and processors would need to show continuous, demonstrable compliance with security obligations, precisely the kind of documented, auditable evidence a certified privacy information management system provides.
- Kenya’s EU adequacy dialogue, the first of its kind on the African continent, signals where compliance expectations are genuinely heading : With Kenya and the European Union having launched formal adequacy dialogue, Kenyan businesses handling data tied to European partners or customers benefit from privacy practices that align with internationally recognized frameworks like ISO 27701.
- Over 9,000 cumulative ODPC complaints show data subjects are genuinely exercising their rights, not staying passive : With this volume of complaints filed since the Act’s enactment, Kenyan businesses face a genuinely active complainant base that requires functioning data subject request and complaint-handling processes, not just policy documents.
What are the steps to get ISO 27701 Certification in Kenya?
our services
- ISO Certification Kenya
- ISO 9001 Certification Kenya
- ISO 14001 Certification Kenya
- ISO 27001 Certification Kenya
- ISO 22000 Certification Kenya
- ISO 27701 Certification Kenya
- ISO 45001 Certification Kenya
- ISO 20000-1 Certification Kenya
- ISO 13485 Certification Kenya
- ISO 17025 Certification Kenya
- ISO 31000 Certification Kenya
- ISO 42001 Certification Kenya
- ISO 37001 Certification Kenya
- ISO 22301 Certification Kenya
- ISO 50001 Certification Kenya
- CE Mark Certification Kenya
- GDPR Certification Kenya
- GMP Certification Kenya
- Halal Certification Kenya
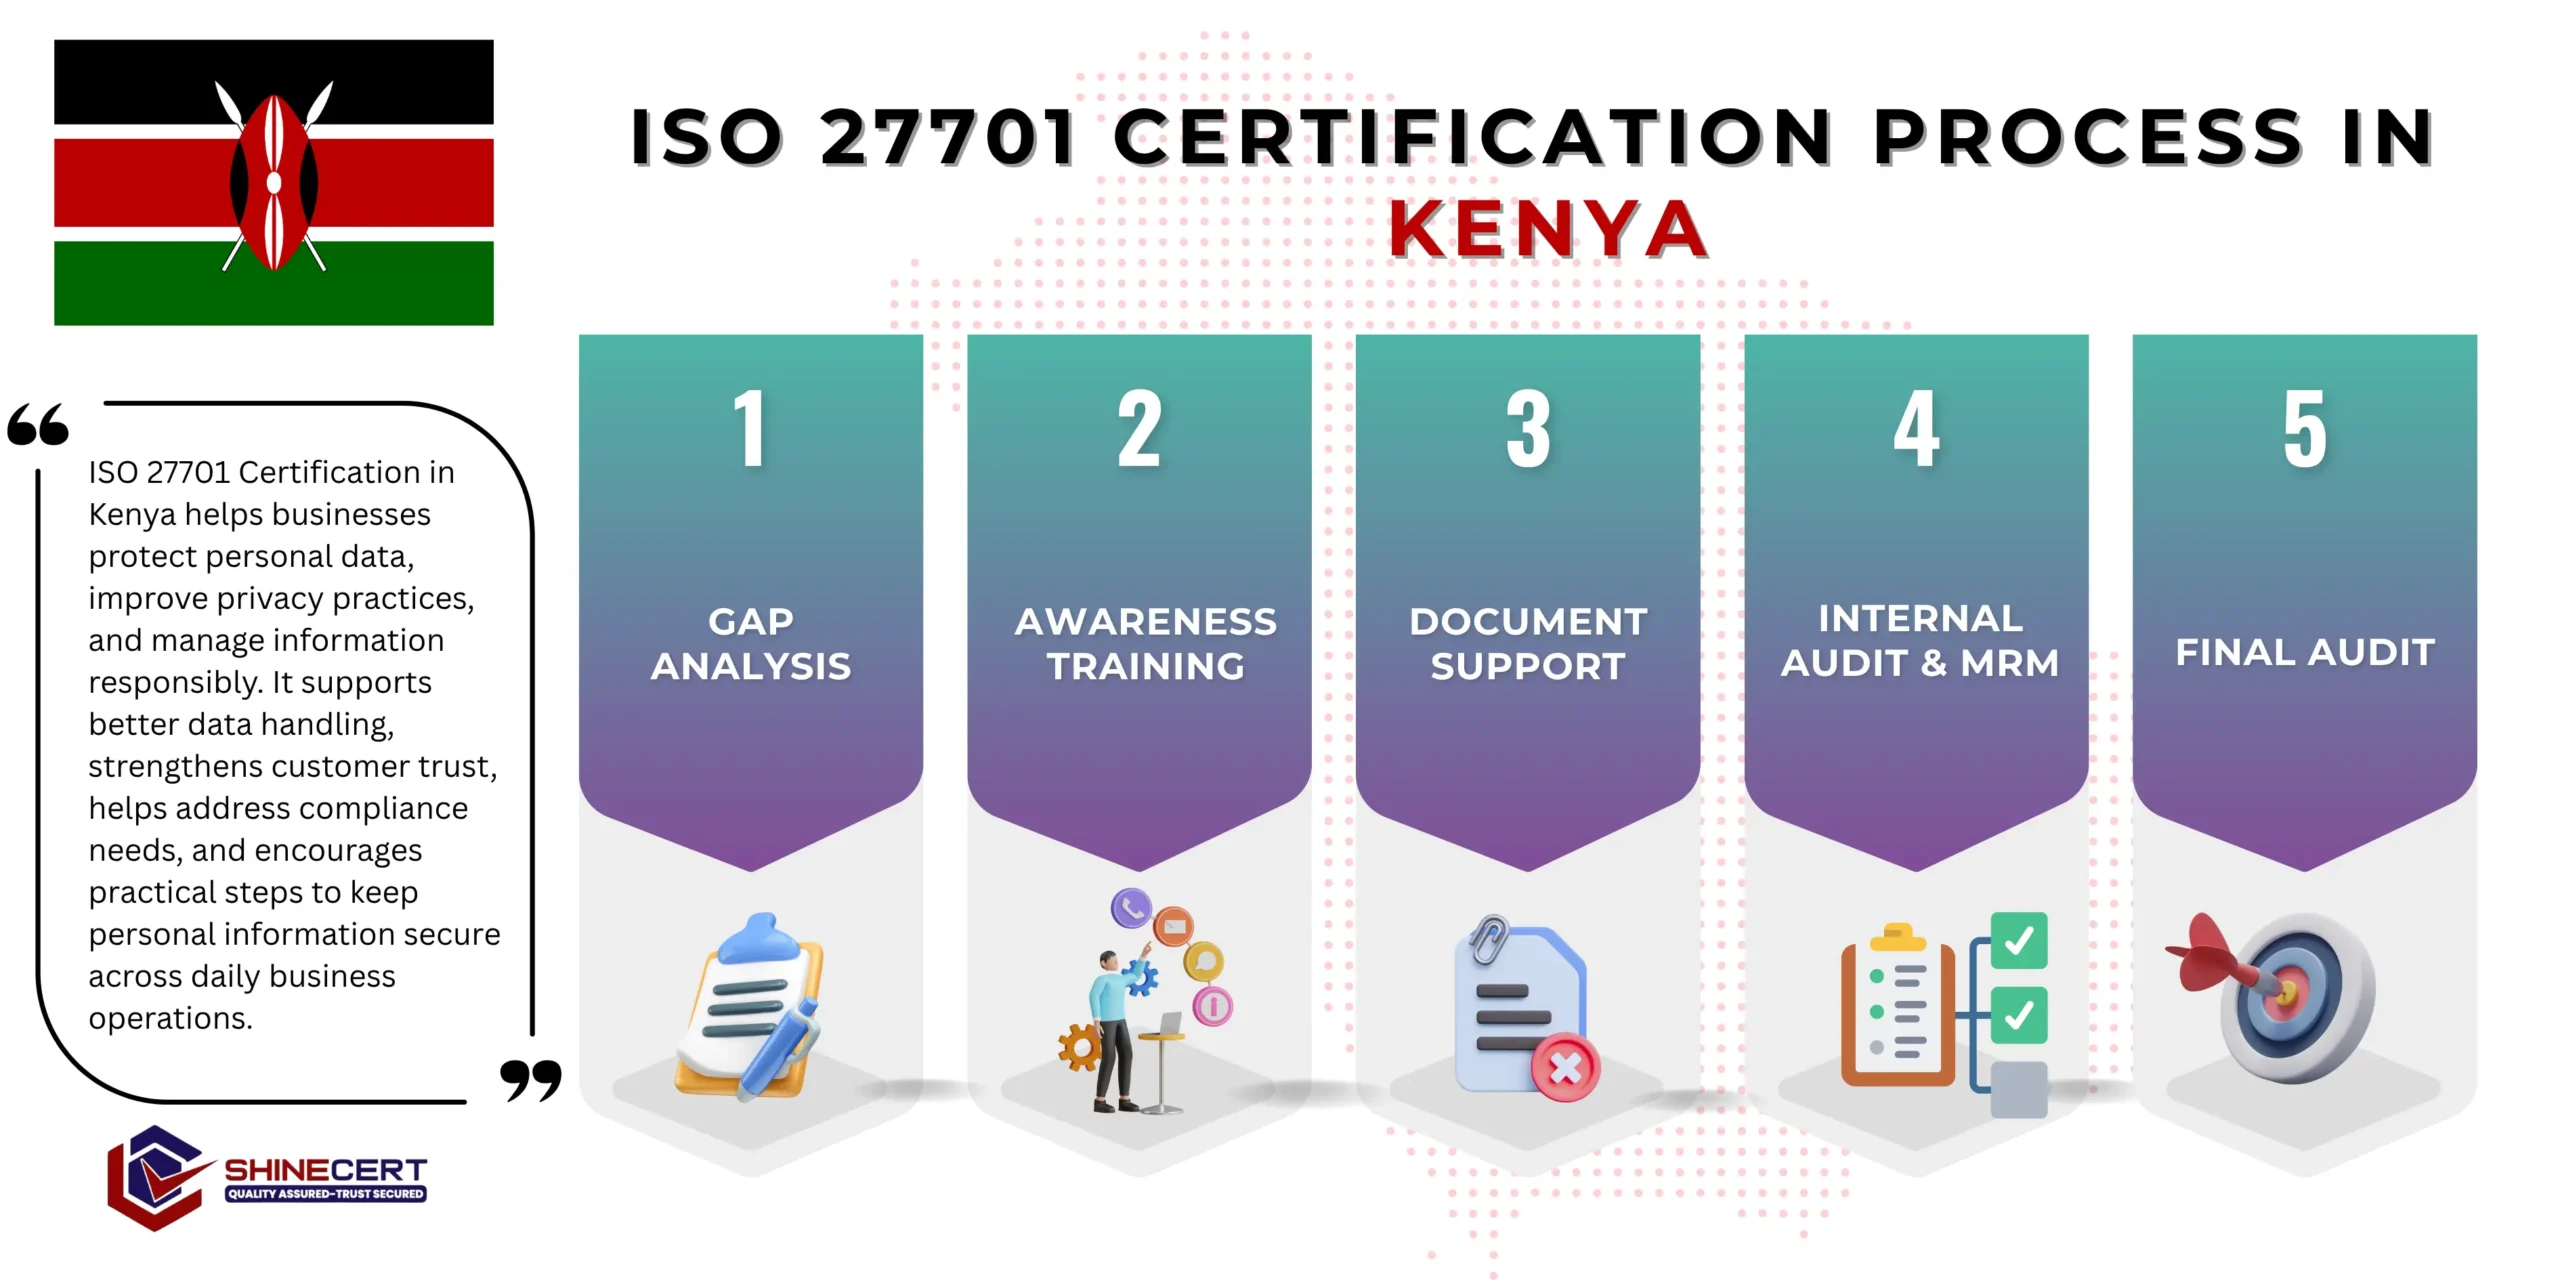
ISO 27701 Certification Process in Kenya
Gap Assessment
We review your existing ISO 27001 status, if any, along with your current data processing practices and ODPC compliance position, mapping what we find against ISO 27701’s requirements.
A gap report mapping your real privacy practices against ISO 27701 requirements and your Data Protection Act compliance position side by side.
Documentation
We build your privacy policy, records of processing, and data subject rights procedures around your actual data flows and systems.
A complete PIMS documentation set, tied to your real processing activities and legal bases.
Implementation
Consent management, breach notification, and data subject request handling move into genuine daily operational use.
A functioning PIMS with real privacy controls actively used and recorded.
Internal Audit and Management Review
We audit against every ISO 27701 clause and your Data Protection Act obligations, surfacing gaps while stakes are low.
An internal audit report and corrective actions closed out before the certification audit.
Certification Audit
Stage 1 confirms your PIMS documentation is genuinely audit-ready, alongside your underlying ISO 27001 controls; Stage 2 has the auditor review your actual operational records. We stay engaged through both stages.
Your ISO 27701 certificate, valid for three years alongside your ISO 27001 certificate, plus a surveillance audit schedule.
Staying Certified: Surveillance and Renewal
An ISO 27701 certificate is valid for three years, running alongside your ISO 27001 certificate’s own three-year cycle. During years one and two, your certification body conducts an annual surveillance audit, sampling your consent records, data subject request logs, and breach notification readiness. Before the three-year mark, a full recertification audit confirms your PIMS has continued functioning throughout the cycle. Given Kenya’s increasingly active enforcement environment, we recommend reviewing your privacy documentation whenever ODPC issues new guidance or the Data Protection Act is amended.
ISO 27701 Certification Cost in Kenya
| Business Profile | Relative Investment Level | Why |
|---|---|---|
| Distributor, no manufacturing | Lower | Scope excludes design control and manufacturing-specific requirements |
| Small manufacturer, single device category | Moderate | Design control and risk management for one device line |
| Larger manufacturer, multiple device categories | Higher | Broader design control scope and multiple risk management files |
| Bundled with ISO 9001 | Moderate-to-higher combined, lower than separate engagements | Shared implementation infrastructure reduces combined cost |
There’s no flat price for ISO 27701 certification in Kenya. Cost genuinely comes down to six factors:
- Whether ISO 27001 is already in place : Organizations already certified add the privacy layer considerably more efficiently than those building both systems simultaneously.
- Volume and sensitivity of personal data processed : Businesses processing large volumes or sensitive categories of personal data face genuinely broader documentation requirements.
- Whether you transfer data across borders : Cross-border transfer documentation adds meaningful scope for businesses working with international partners, cloud providers, or parent companies.
- Existing ODPC compliance maturity : Businesses already registered with ODPC and managing data subject requests aren’t starting from zero.
- Certification body fees, tracked separately from our consulting fees : The certification audit itself is invoiced directly by whichever accredited body conducts your audit.
- Number of systems and processes in scope : A privacy management system spanning multiple business units or IT systems requires more coordination to document and implement.
Benefits of ISO 27701 Certification for Kenyan Organizations
Kenyan organizations that complete certification gain considerably more than a document proving privacy compliance. Here is what certified businesses genuinely gain:
A certified privacy information management system gives you documented, systematic evidence of accountability that considerably strengthens your position under ODPC’s compliance audit framework.
Systematic consent management and data subject rights processes catch privacy gaps before they escalate into complaints or enforcement action.
ISO 27701 is recognized well beyond Kenya, relevant for businesses handling data from European or other international partners amid Kenya’s EU adequacy dialogue.
A documented process for responding to access, correction, and deletion requests means your organization can genuinely meet these obligations without scrambling each time.
ISO 27701’s transfer safeguard requirements give you a structured way to document and justify cross-border data flows under Kenyan law.
Larger institutional clients and international partners increasingly require demonstrable privacy management as a genuine condition of data-sharing agreements.
Because ISO 27701 builds directly on ISO 27001’s structure, organizations already certified to ISO 27001 add privacy management considerably more efficiently than starting from scratch.
Demonstrable, independently verified privacy practice is a genuine differentiator as Kenyan consumer awareness of data rights continues to grow.
A Kenyan Business We’ve Worked With
- A Nairobi-based digital lending platform, processing loan applications involving sensitive financial and identity data for thousands of customers monthly, approached us after receiving a data subject access request they struggled to fulfill within the required timeframe due to data being scattered across multiple systems with no central tracking.
- Our gap assessment found the company’s ISO 27001 security controls were solid, but there was no formal records-of-processing inventory, and consent language in their loan application flow hadn’t been reviewed against current Data Protection Act requirements in some time.
- We built the records of processing inventory, updated consent flows, and a data subject rights procedure with clear internal ownership and tracked response timelines. Certification took just under five months, building on their existing ISO 27001 foundation, and the company now handles data subject requests within a fraction of the previous response time.
- This reflects a pattern we see often, genuinely strong security controls that hadn’t yet been extended into structured privacy-specific practice, rather than a single specific engagement.
Where Certification Matters Most Across Kenya’s Economy?
Fintech and digital lending
ISO 27701 is close to essential given direct handling of sensitive financial and personal data; pair with ISO 27001 as the required security foundation.
Read moreHealthtech and telemedicine
ISO 27701 addresses genuine health data sensitivity; pair with ISO 27001 for the underlying security controls health data demands.
Read moreHR and recruitment platforms
ISO 27701 directly addresses employee and candidate data handling expectations increasingly scrutinized by ODPC.
Read moreBusiness process outsourcing and call centers
ISO 27701 supports the data handling assurances international clients increasingly require as a contractual condition.
Read moreE-commerce and digital marketing
ISO 27701 addresses customer data and consent management expectations central to online retail and marketing operations.
Read moreRealistic Timelines for Kenyan Businesses
| Business Profile | Typical Total Timeline | What Drives This |
|---|---|---|
| Already ISO 27001 certified | 2.5–4 months | Privacy-specific layer added on top of an existing security foundation |
| Building ISO 27001 and ISO 27701 together | 5–7.5 months | Full security and privacy management system built from scratch |
| Larger organization with complex data flows | 6–9 months | Extensive records of processing and cross-border transfer documentation |
Beyond company size, the single biggest timeline driver is whether you already hold ISO 27001 certification, building the privacy layer on top of an existing security foundation is considerably faster than building both simultaneously.
The Documentation ODPC and Auditors Expect
A documented statement defining which personal data processing activities, systems, and roles the privacy information management system covers, aligned with your ODPC registration if applicable.
A documented policy, approved by top management, expressing genuine commitment to privacy and compliance with the Data Protection Act and ODPC guidance.
A documented, actively maintained inventory of what personal data you process, why, and under what legal basis.
Documentation showing how consent is genuinely obtained, recorded, and can be withdrawn, aligned with Data Protection Act requirements.
A documented, actively used process for handling access, correction, deletion, and objection requests within required timeframes.
Records showing any international data transfers are genuinely assessed and safeguarded in line with Kenyan legal requirements.
Documentation showing high-risk processing activities have genuinely been assessed for privacy impact before implementation.
A documented process for detecting, assessing, and notifying ODPC and affected individuals of personal data breaches within required timeframes.
A planned internal audit cycle and documented management review decisions on privacy priorities.
The Real Challenges Organizations Face While Implementing ISO 27701
- Underestimating how much ISO 27701 depends on ISO 27001 maturity : Organizations sometimes approach ISO 27701 without a genuinely solid ISO 27001 foundation already in place, which considerably slows the privacy-specific work.
- Records of processing that don’t reflect actual data flows : A common gap is documenting processing activities as they were originally designed rather than as systems and integrations have genuinely evolved over time.
- Consent language that hasn’t kept pace with regulatory change : Businesses sometimes carry forward consent language from years earlier without reviewing it against current Data Protection Act interpretation and ODPC guidance.
- Data subject request handling that isn’t genuinely centralized : When personal data is scattered across multiple systems with no central tracking, responding to access or deletion requests within required timeframes becomes genuinely difficult.
Why Businesses Choose ShineCert in Kenya?
ShineCert brings 10 years of ISO consulting and certification experience to Kenya’s market, coordinated through our Riyadh and India offices with services delivered remotely or on-site depending on what your engagement genuinely needs. We’ve guided more than 10,000 organizations through ISO certification worldwide, and we build every Kenya privacy engagement around your actual data processing activities and ODPC obligations, this is why Kenyan businesses increasingly choose ShineCert as the best ISO 27701 consultant in Kenya.
Choosing a Certification Body in Kenya?
What to Check | Why It Matters |
Accreditation under a recognized international accreditation framework, alongside ISO 27001 | Confirms genuine, internationally recognized certification for both security and privacy |
Genuine familiarity with the Data Protection Act and ODPC enforcement practice | Ensures your PIMS documentation aligns with actual Kenyan regulatory expectations |
Experience with your specific data processing profile | Fintech, healthtech, and BPO involve genuinely different privacy considerations |
Willingness to assess your ISO 27001 foundation honestly | A weak security foundation undermines privacy certification regardless of how well the privacy layer is documented |
Start Your Certification Journey
Whether you’re extending an existing ISO 27001 certification or building both together, we’ll walk through your specific data processing activities and cost factors before proposing a fixed-scope plan, delivered remotely, on-site, or however genuinely fits your project. Book a free consultation or contact us directly to get started.
Frequently Asked Questions
Look for genuine familiarity with the Data Protection Act and ODPC enforcement practice, experience with your specific data profile, and honest assessment of your ISO 27001 foundation. ShineCert scopes every Kenya engagement individually.
Yes, ISO 27701 cannot be certified standalone; it requires an existing or simultaneously implemented ISO 27001 certification as its foundation.
No, ODPC registration remains a separate, mandatory requirement for qualifying data controllers and processors, but a certified privacy management system gives you the documentation that makes compliance considerably stronger.
It genuinely depends on whether ISO 27001 is already in place, your data volume and sensitivity, and whether you transfer data across borders, we scope every project individually.
Typically two and a half to nine months depending on whether ISO 27001 is already in place and organizational complexity, see our detailed timeline breakdown above.
Certification doesn’t exempt you from investigation, but a certified, well-documented system considerably strengthens your position and typically results in a smoother outcome.
Documentation work runs effectively over remote sessions, but process verification and staff interviews genuinely benefit from in-person engagement.
ShineCert doesn’t maintain a standalone Kenya office; we coordinate Kenya engagements from our Riyadh and India offices, with services delivered remotely or on-site as your project requires.