
ISO 37001 Certification in South Africa
Quick Answer
ISO 37001 is the world’s leading anti-bribery management standard. It proves a business has documented, working controls to prevent, detect, and respond to bribery, verified by an independent auditor. In South Africa, this directly overlaps with a 2024 amendment to PRECCA (the Prevention and Combating of Corrupt Activities Act) that introduced a “failure to prevent corruption” offence: a business can now be held criminally liable if an associated person pays a bribe on its behalf, unless the business can show it had “adequate procedures” in place to prevent it. ISO 37001 is the clearest way to demonstrate exactly that. Certification usually takes three to six months. Cost depends on your exposure to public-sector dealings and how much anti-bribery documentation already exists.
What Is ISO 37001?
ISO 37001 is an international standard for anti-bribery management systems. It sets out what a business needs in place to prevent bribery, by employees, agents, contractors, or business partners acting on its behalf, and to detect and respond to it quickly if it happens anyway.
Think of it as a structured way of answering a question regulators now ask directly: what “adequate procedures” does your business actually have to prevent someone from paying a bribe in your name. A business becomes “ISO 37001 certified” once an independent, accredited auditor confirms these anti-bribery controls genuinely operate, not just exist as a code of conduct.
In South Africa, PRECCA is the primary anti-corruption statute, and a 2024 amendment, a direct recommendation of the State Capture Commission, introduced a new offence: a business can be held criminally liable if a person associated with it offers a bribe intending to secure business or an advantage, unless the business had “adequate procedures” designed to prevent it. ISO 37001 gives you a recognised, structured way to build and demonstrate exactly those procedures.
Why ISO 37001 Matters in South Africa?
- The legal bar has changed since 2024 : PRECCA’s failure-to-prevent offence means a business no longer needs to have directly authorised a bribe to face liability, only to have failed to prevent an associated person from offering one. Having no anti-bribery programme at all is now a direct legal exposure, not just a reputational risk.
- Penalties are severe : Convictions under PRECCA can carry life imprisonment in the High Court, or up to 18 years in regional courts, alongside substantial fines, for individuals and, under the new provision, corporate liability for the business itself.
- Government and multinational clients increasingly require it : Given South Africa’s ongoing scrutiny around state capture, both public entities and multinational partners are increasingly asking suppliers to demonstrate structured anti-bribery controls, not just a written policy.
- It’s the clearest defence available : Where PRECCA’s failure-to-prevent offence explicitly allows a business to defend itself by showing “adequate procedures” were in place, ISO 37001 certification is the most recognised way to demonstrate exactly that in practice.
What are the steps to get ISO 37001 Certification in South Africa?
our services
- ISO Certification South Africa
- ISO 9001 Certification South Africa
- ISO 14001 Certification South Africa
- ISO 27001 Certification South Africa
- ISO 22000 Certification South Africa
- ISO 27701 Certification South Africa
- ISO 45001 Certification South Africa
- ISO 20000-1 Certification South Africa
- ISO 13485 Certification South Africa
- ISO 17025 Certification South Africa
- ISO 31000 Certification South Africa
- ISO 42001 Certification South Africa
- ISO 37001 Certification South Africa
- ISO 22301 Certification South Africa
- ISO 50001 Certification South Africa
- CE Mark Certification South Africa
- GDPR Certification South Africa
- GMP Certification South Africa
- Halal Certification South Africa
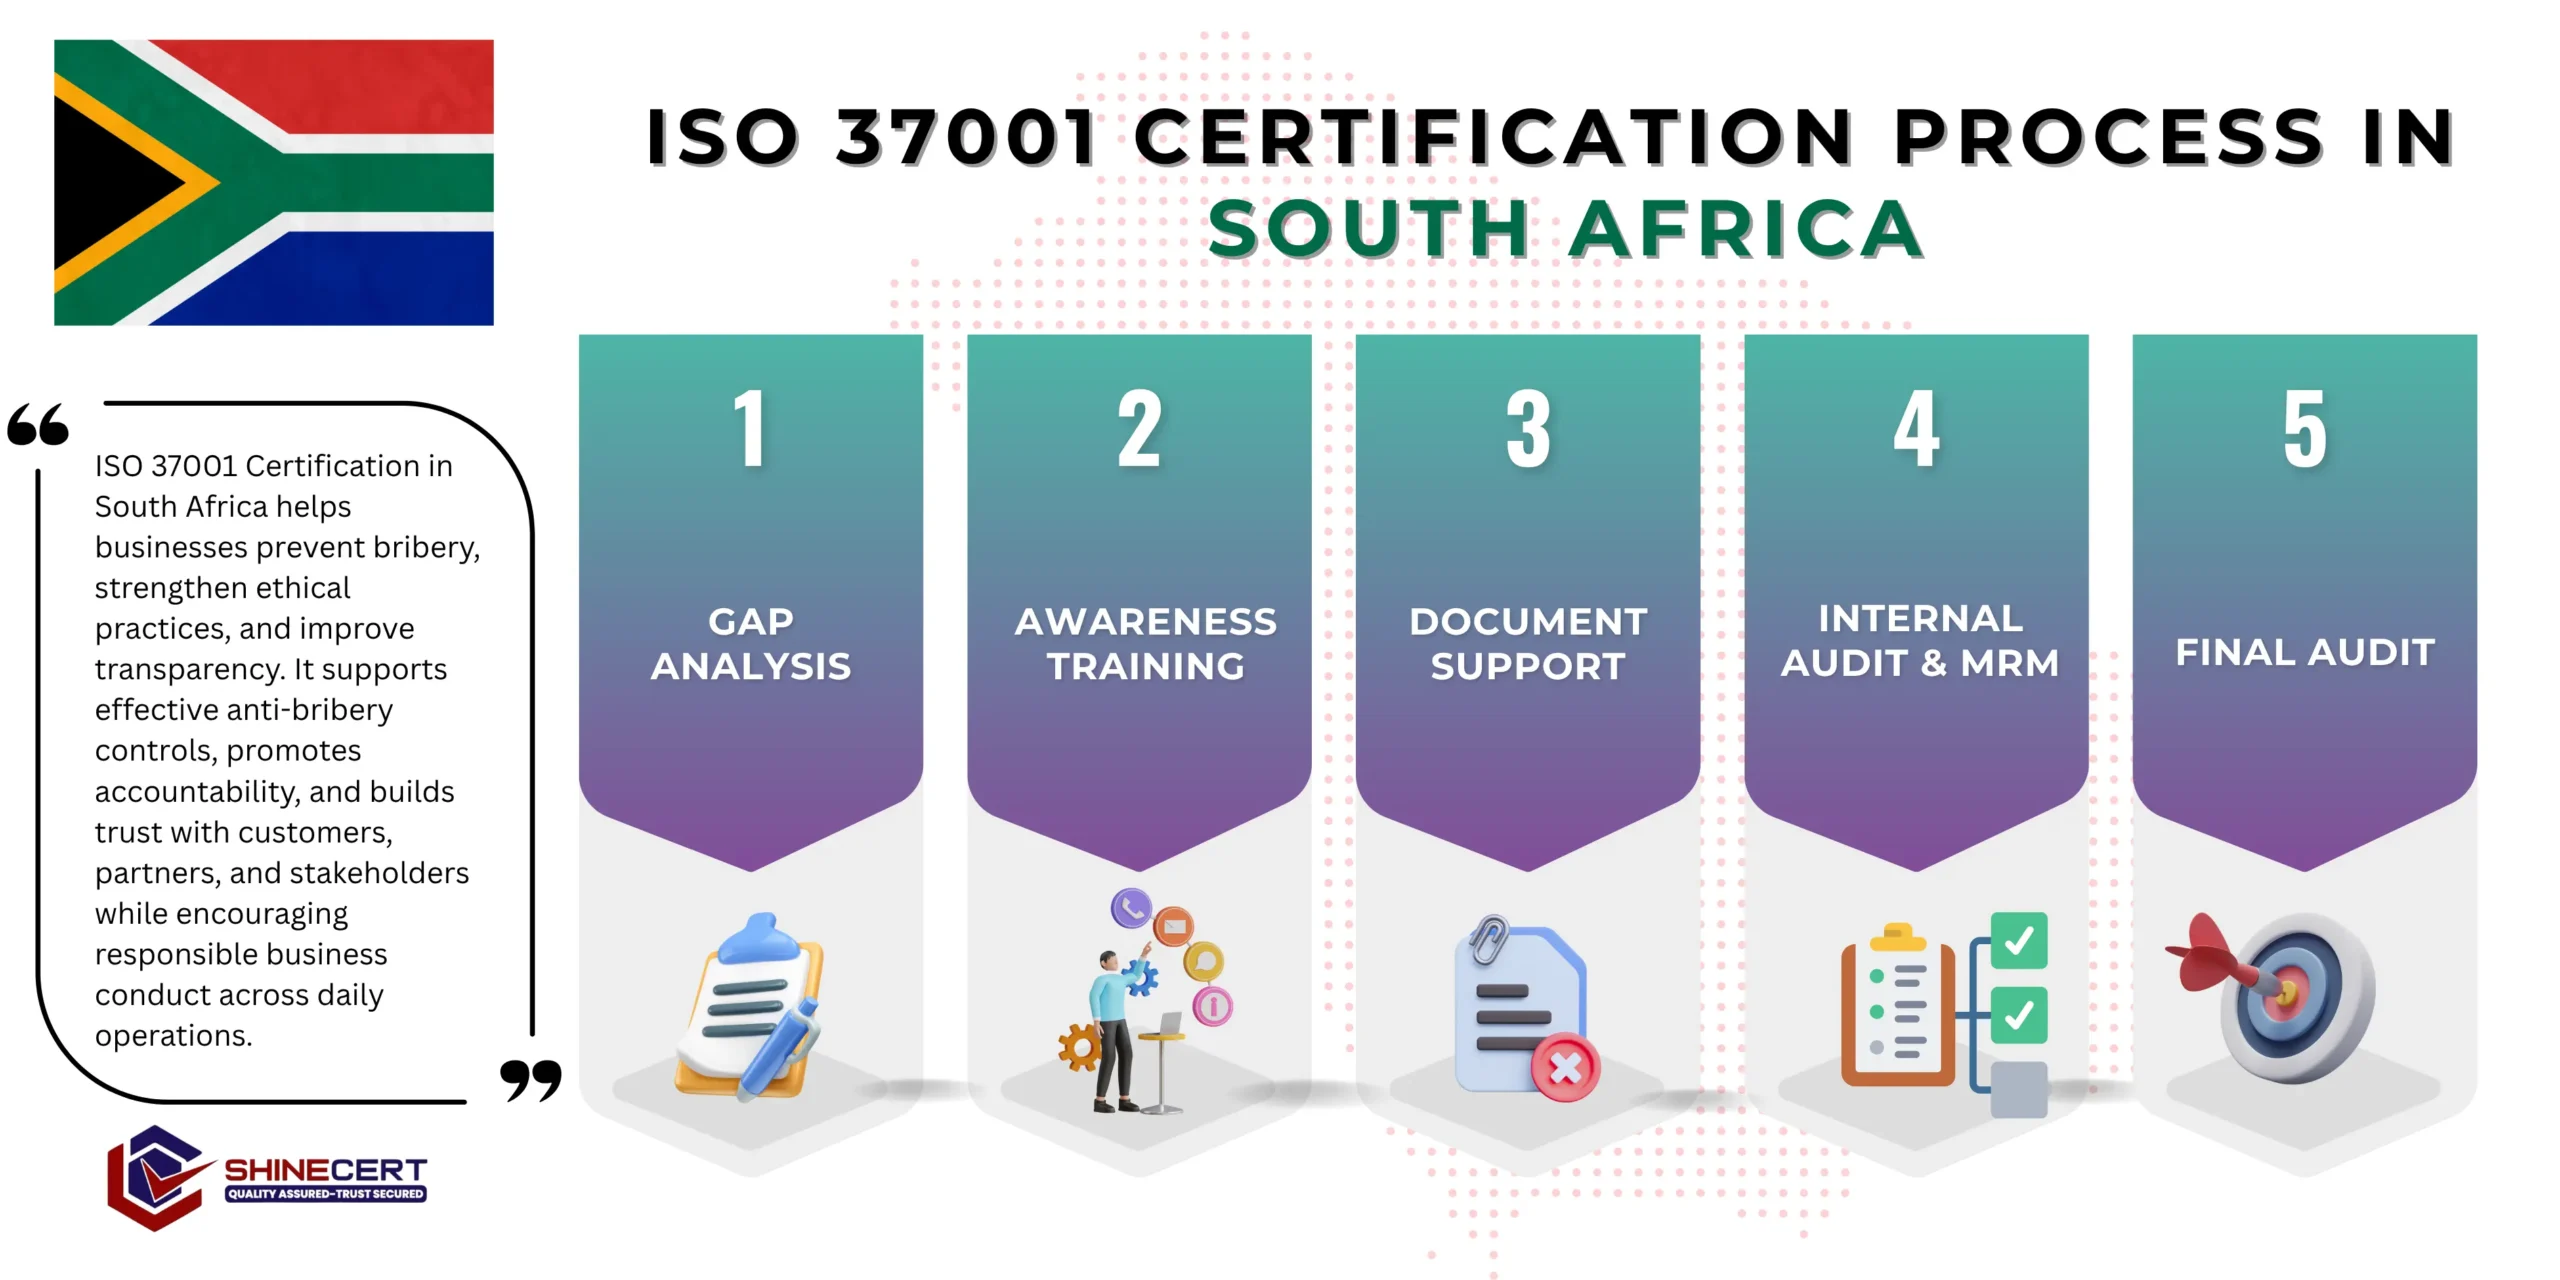
The ISO 37001 Certification Process in South Africa
Getting certified follows five steps. Here’s exactly what happens at each one.
Bribery Risk Assessment
We identify where your business genuinely faces bribery risk, government tenders, agents, high-value gifts, foreign partners, rather than treating every part of the business equally.
A precise picture of your real exposure, not a generic compliance checklist.
A bribery risk assessment specific to your business relationships.
Documentation
We help build your anti-bribery policy, third-party due diligence procedure, and gifts-and-hospitality controls around how your business actually operates.
Controls your sales and procurement teams can genuinely follow, not a policy nobody reads.
A complete ISO 37001 documentation set.
Implementation and Training
Controls go live, with staff trained on recognising bribery red flags and following due diligence procedures for agents and partners.
This phase takes real time, since staff need to genuinely internalise when to escalate a concern, not just sign an acknowledgement form.
Training records and evidence controls are genuinely operating.
Internal Audit and Management Review
We test whether controls genuinely work, with findings feeding into a management review before the external audit.
Gaps surface here, while there’s still time to close them quietly.
An internal audit report and management review minutes.
Certification Audit
An accredited, independent auditor reviews your documentation and tests whether controls function as described in practice.
Both your policy and your genuine business practice get checked before certification.
Your ISO 37001 certificate and a surveillance audit schedule.
Benefits of ISO 37001 Certification
- Direct legal defence under PRECCA’s failure-to-prevent offence : A working, certified anti-bribery system is concrete evidence of the “adequate procedures” the law specifically references.
- Fewer bribery incidents reaching the business : Structured due diligence on agents, partners, and gifts catches red flags before they become a genuine incident.
- Stronger standing with government and multinational clients : Certification demonstrates real anti-corruption commitment at a time when this scrutiny is at its highest in South Africa’s history.
- Reduced reputational risk : Businesses linked to bribery, even through an associated party, suffer real reputational damage; a working system reduces that exposure meaningfully.
- Clearer accountability for gifts, hospitality, and third parties : Staff know exactly what’s permitted and what requires approval, rather than relying on individual judgment calls.
- A foundation for broader governance : Much of the risk assessment and due diligence structure overlaps with ISO 31000 and general corporate governance requirements.
What Does ISO 37001 Certification Cost in South Africa?
- Exposure to government and public-sector dealings : Businesses regularly bidding for government tenders carry higher bribery risk exposure than those operating purely in private commercial markets.
- Use of agents and intermediaries ; More third parties acting on your behalf mean more due diligence work to build and maintain.
- Current anti-bribery practices : Businesses already running a code of conduct or basic due diligence aren’t starting from nothing, which shortens the work.
- International dealings : Businesses operating across borders typically face broader anti-corruption exposure requiring more thorough risk assessment.
Case Study: A Pretoria Government Contractor
- An engineering firm regularly bidding for government infrastructure tenders in Pretoria came to us after PRECCA’s 2024 amendment made leadership genuinely concerned about liability for agents they’d engaged to help navigate tender processes in other provinces.
- We ran a bribery risk assessment and found the firm’s core team operated with real integrity, but had never formally vetted the agents it worked with, and had no gifts and hospitality register despite routinely receiving invitations to industry events from potential suppliers.
- Over four months, we built a due diligence procedure for vetting agents and partners, established a gifts and hospitality register, and trained staff on recognising and escalating bribery red flags. The firm was certified within the expected timeline.
- The firm has since used its certification as part of its own tender submissions, presenting it as direct evidence of the “adequate procedures” PRECCA’s failure-to-prevent offence specifically references, strengthening its standing with government procurement evaluators.
ISO 37001 Certification Across South Africa
ISO 37001 in Pretoria
ISO 37001 in Johannesburg
ISO 37001 in Cape Town
ISO 37001 in Durban
ISO 37001 in Sandton
What Documents Do You Need for ISO 37001 in South Africa?
- Context and Scope : Document: Scope of the ABMS Statement. Defines which business units, relationships, and geographies the anti-bribery management system covers.
- Leadership : Document: Anti-Bribery Policy. A signed top-management commitment to preventing bribery across the business and its associated persons.
- Planning : Document: Bribery Risk Assessment. Identifies which relationships, transactions, and markets carry genuine bribery risk. Document: Legal Requirements Register. A record of PRECCA and any other anti-corruption obligations relevant to your business.
- Support : Document: Anti-Bribery Training Records. Evidence staff, agents, and relevant third parties understand what’s expected of them. Document: Due Diligence Procedure. How agents, distributors, and business partners are vetted before engagement.
- Operation : Document: Gifts and Hospitality Register. A record of gifts and hospitality given or received above a defined threshold. Document: Financial Controls Procedure. How payments, especially to agents and intermediaries, are reviewed and approved.
- Performance Evaluation : Document: Concerns and Incident Log. A working record of bribery concerns raised, including through a whistleblowing channel, and how each was handled. Document: Internal Audit Records. Proof an internal audit was carried out against every clause.
- Improvement : Document: Corrective Action Log. A functioning record tracking every anti-bribery weakness from discovery through to a verified fix.
Why Businesses Choose ShineCert in South Africa?
We’ve spent 10 years helping more than 10,000 businesses worldwide get certified, coordinated through our Riyadh and India offices with work delivered remotely or on-site as needed. As the best ISO 37001 consultant in South Africa, ShineCert quotes based on your real risk exposure, explains PRECCA’s implications in plain language, and builds controls your team can genuinely maintain.
How Long Does ISO 37001 Certification Take in South Africa?
| Business Size | Typical Timeline | Why |
|---|---|---|
| Small, limited public-sector dealings | 3–4 months | Lower risk exposure to document |
| Medium, regular tenders or third parties | 4–5 months | More due diligence and controls needed |
| Larger, significant public-sector or international exposure | 5–6 months | Broader risk assessment across relationships |
Ready to Get Started?
Whether you’re responding to PRECCA’s 2024 amendment or a client’s anti-corruption due diligence, we’ll walk through your business relationships and give you a clear, honest quote. Book a free consultation or contact us to get started.
Frequently Asked Questions
No, but PRECCA’s 2024 failure-to-prevent offence allows an “adequate procedures” defence, and ISO 37001 is the clearest recognised way to demonstrate exactly that.
It depends on your public-sector exposure, use of agents, and current controls. We quote every business individually.
Usually three to six months, depending on risk exposure.
PRECCA covers private-sector bribery too, so any business dealing with agents, large contracts, or international partners can benefit.
Most documentation and training work can happen remotely.
No certification guarantees legal protection, but a genuinely operating system is the strongest evidence available for an “adequate procedures” defence.