
ISO 27701 Certification in Tanzania
Quick Answer
ISO 27701 takes ISO 27001’s information security foundation and adds a specific layer of controls for handling personal data as a defined privacy information management system. With the Personal Data Protection Act now fully enforceable in Tanzania since April 2026 and more than 14,000 institutions already registered with the Personal Data Protection Commission (PDPC), the gap ISO 27701 fills has become concrete rather than theoretical: registration confirms you’re a recognized data handler, but it says nothing about whether your consent processes, data subject request handling, or cross-border transfer safeguards would actually survive a compliance review. Because ISO 27701 can’t stand alone, it requires an existing or simultaneously built ISO 27001 certification underneath it. Certification typically takes four to seven months, with cost shaped by real factors including whether that ISO 27001 foundation already exists.
Understanding ISO 27701: What It Actually Is, and Why It Matters in Tanzania
ISO 27701 is published by the International Organization for Standardization as an extension to ISO 27001, adding a defined set of requirements for managing personal data specifically, rather than information security in the broader sense. It doesn’t replace ISO 27001’s technical and organizational security controls, it builds directly on top of them, adding privacy-specific expectations: how consent gets captured and withdrawn, how the organization responds when someone asks what data is held about them, and how transfers of personal data outside Tanzania get assessed and safeguarded. Certification means an accredited auditor has confirmed both layers genuinely work together, not just that a privacy policy exists somewhere on file.
The reason this distinction carries real weight in Tanzania right now comes down to enforcement timing. PDPC registration was, until April 2026, something businesses could treat as an administrative formality completed once and set aside. With full enforceability now in effect, the Commission has the standing to actually examine whether registered organizations are managing personal data the way the law requires, not simply whether they filled out the registration form. ISO 27701 gives businesses a structured, independently verified answer to that question before a regulator ever has to ask it.
What are the steps to get ISO 27701 Certification in Tanzania?
our services
- ISO Certification Tanzania
- ISO 9001 Certification Tanzania
- ISO 14001 Certification Tanzania
- ISO 27001 Certification Tanzania
- ISO 22000 Certification Tanzania
- ISO 27701 Certification Tanzania
- ISO 45001 Certification Tanzania
- ISO 20000-1 Certification Tanzania
- ISO 13485 Certification Tanzania
- ISO 17025 Certification Tanzania
- ISO 31000 Certification Tanzania
- ISO 42001 Certification Tanzania
- ISO 37001 Certification Tanzania
- ISO 22301 Certification Tanzania
- ISO 50001 Certification Tanzania
- CE Mark Certification Tanzania
- GDPR Certification Tanzania
- GMP Certification Tanzania
- Halal Certification Tanzania
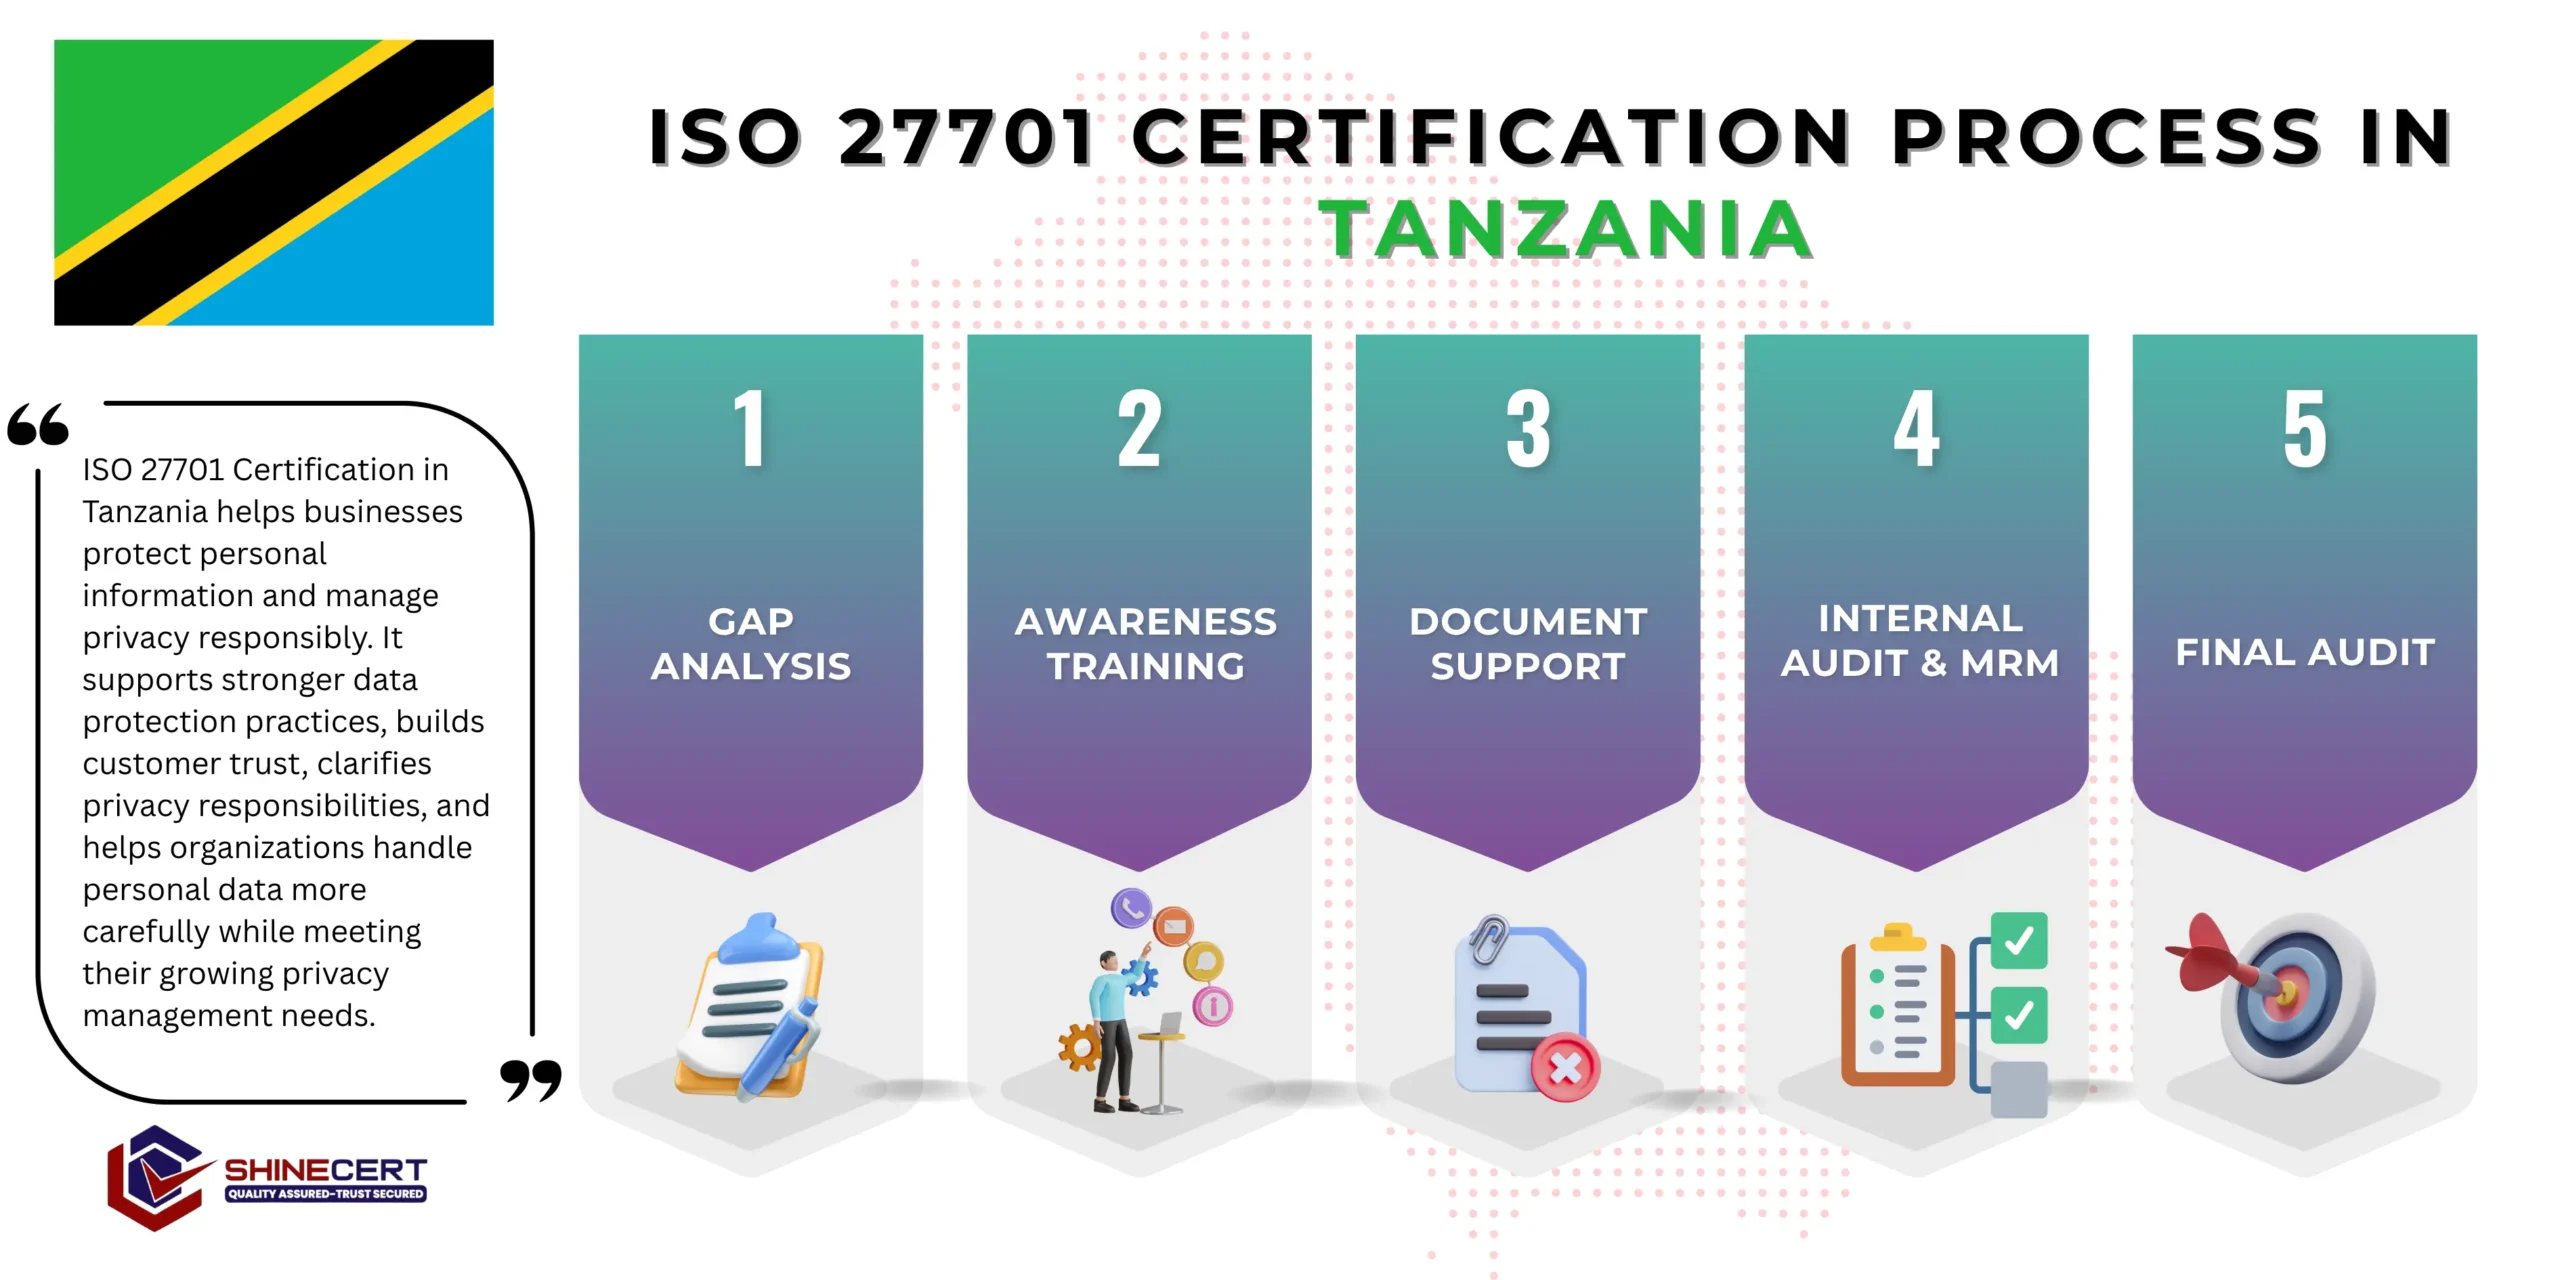
ISO 27701 Certification Process in Tanzania
Gap Assessment
We start with your existing ISO 27001 status, if any, and your current PDPC registration and data-handling practices, and map both against ISO 27701's actual requirements.
A gap report placing your real privacy practices side by side with ISO 27701 and your PDPA compliance position.
Documentation
We build your privacy policy, records of processing, and data subject rights procedures around the way your organization actually handles personal data day to day.
A complete PIMS documentation set tied to your genuine processing activities and legal bases.
Implementation
Consent capture, breach notification, and data subject request handling move from written procedure into everyday operational practice.
A working privacy management system with controls being actively used and recorded.
Internal Audit and Management Review
We test the system against every ISO 27701 clause and your PDPA obligations together, surfacing gaps before an external auditor does.
An internal audit report with corrective actions already closed before certification.
Certification Audit
Stage 1 confirms your documentation, alongside your ISO 27001 foundation, is genuinely ready; Stage 2 has the auditor review your actual operational records and speak with your team.
Your ISO 27701 certificate, valid for three years alongside your ISO 27001 certificate, plus a surveillance schedule.
Staying Certified: Surveillance and Renewal
An ISO 27701 certificate runs for three years, on the same clock as your ISO 27001 certificate. Annual surveillance audits in years one and two sample your consent records, data subject request logs, and breach notification readiness. A full recertification audit at the three-year mark confirms the system held up throughout the cycle. Given how recently the PDPA became fully enforceable, we recommend reviewing your privacy documentation whenever the PDPC issues new guidance, particularly in the early years of active enforcement.
ISO 27701 Certification Cost in Tanzania
There’s no flat price for ISO 27701 certification in Tanzania, cost genuinely comes down to six factors:
01
Whether ISO 27001 is already in place
Organizations with existing certification add the privacy layer far more efficiently than those building both systems from scratch at the same time.
02
Volume and sensitivity of personal data processed
Businesses handling large volumes or particularly sensitive categories of data, such as health or financial records, face broader documentation requirements.
03
Whether personal data crosses borders
Cross-border transfer documentation adds real scope for businesses working with international partners, cloud providers, or a parent company abroad.
04
Existing PDPC compliance maturity
Businesses already registered and actively managing data subject requests aren’t starting the documentation process from zero.
05
Certification body fees, invoiced entirely separately from our consulting work
Whichever accredited body conducts your certification audit bills that fee directly.
06
Number of systems and business units in scope
A privacy management system spanning multiple departments or IT systems takes more coordination to document and roll out.
Why It’s Becoming Essential for Tanzanian Businesses Right Now?
- Full PDPA enforceability closed the gap between registering and actually complying : Now that the voluntary period has ended, the more than 14,000 institutions already on the PDPC’s register face a materially different question: not whether they registered, but whether their day-to-day handling of personal data would hold up under a genuine compliance review.
- The PDPC’s flagged sectors, healthcare, finance, and education, carry a heavier practical burden to demonstrate real privacy practice, not just registration : Organizations in these categories handle some of the most sensitive personal data in the economy, and the Commission’s specific attention to these sectors means a documented, certifiable privacy system is a genuinely sound way to get ahead of scrutiny rather than wait for it.
- International partners and cloud providers increasingly ask for privacy certification specifically, not just a security certificate : As Tanzanian businesses deepen ties with international technology and financial partners, those partners are starting to distinguish between general information security certification and privacy-specific assurance, and ISO 27701 answers the second question directly.
- Data subjects in Tanzania are becoming more aware of their rights under the PDPA, which means requests to access, correct, or delete personal data are no longer rare : As public awareness of the law grows, businesses without a working, timed process for handling these requests risk missing statutory deadlines simply because no one owns the process internally.
Benefits of ISO 27701 Certification for Tanzanian Organizations
Tanzanian organizations that complete certification gain considerably more than a document confirming privacy policies exist. Here’s what actually changes:
A certified privacy information management system gives you structured, audit-ready evidence that considerably strengthens your position if the PDPC examines your practices.
Systematic consent management and a working data subject rights process catch problems internally before they turn into complaints filed with the regulator.
ISO 27701 is recognized well beyond Tanzania, which matters directly for businesses handling data tied to international partnerships or cloud infrastructure.
A documented, owned process for access, correction, and deletion requests means these are handled on time, not scrambled together case by case.
ISO 27701’s transfer safeguard requirements give you a structured, defensible way to document why and how personal data moves outside Tanzania.
Larger institutional clients and international partners increasingly treat demonstrable privacy management as a real condition of working together.
Because ISO 27701 is built directly on ISO 27001’s structure, organizations with that foundation already in place add privacy management with considerably less duplicated effort.
As Tanzanian consumers become more aware of their data rights under the PDPA, independently verified privacy practice becomes a genuine point of differentiation.
The Real Challenges Organizations Face While Implementing ISO 27701
- Underestimating how much ISO 27701 leans on ISO 27001 already being solid : Organizations sometimes start ISO 27701 work before their underlying security management system is genuinely mature, which slows the privacy-specific layer considerably.
- Records of processing that describe the system as it was designed, not as it actually runs : A common gap is documentation that reflects an original system design rather than how integrations and data flows have actually evolved since.
- Consent language that hasn’t been revisited since the PDPA became enforceable : Businesses sometimes carry forward consent wording drafted years ago without checking it against current PDPC guidance.
- Data subject requests handled informally rather than through an owned process : When access or deletion requests come in through general customer service channels rather than a defined procedure, meeting statutory response timeframes becomes genuinely difficult.
Where Certification Matters Most Across Tanzania’s Economy?
Mobile money and fintech
ISO 27701 is close to essential given direct handling of sensitive financial and identity data; pair with ISO 27001 as the required security foundation.
Read moreHealthcare and telemedicine
ISO 27701 addresses genuine health data sensitivity, one of the sectors the PDPC has specifically flagged for closer attention.
Read moreEducation technology platforms
ISO 27701 directly addresses student and family data handling, another sector named specifically by the PDPC.
Read moreBusiness process outsourcing
ISO 27701 supports the data handling assurances international clients increasingly require as a contractual condition of outsourcing work.
Read moreE-commerce and digital services
ISO 27701 addresses customer data and consent management expectations central to online retail and digital service delivery.
Read moreA Tanzanian Business We’ve Worked With
- A Dar es Salaam-based mobile money and micro-lending platform, handling identity verification and transaction data for a large and growing customer base, came to us after a partner bank’s due diligence process specifically asked whether the company held privacy certification distinct from its existing information security certificate.
- Our gap assessment found the company’s ISO 27001 controls were genuinely solid, but records of processing had never been formally documented, and the process for handling a customer’s request to access or delete their data ran informally through customer service tickets rather than a defined procedure with tracked timelines.
- We built the records of processing inventory, formalized the data subject rights procedure with clear ownership, and reviewed consent language in the onboarding flow against current PDPA requirements. Certification took just over four months, building on the existing ISO 27001 foundation, and the partner bank’s due diligence requirement was satisfied on the first review.
- This reflects a recurring pattern among Tanzanian fintechs: we work with strong technical security controls that simply hadn’t been extended into a formally documented privacy practice, rather than one specific client account.
The Documentation PDPC and Auditors Expect
- PIMS Scope Statement : A documented statement defining which personal data processing activities, systems, and business units the privacy information management system actually covers, aligned with your PDPC registration.
- Privacy Policy : A policy approved by top management, expressing real commitment to privacy practice consistent with the PDPA and PDPC guidance.
- Records of Processing Activities. An actively maintained inventory describing what personal data you process, the purpose behind each activity, and the legal basis relied on.
- Consent Management Records : Documentation showing exactly how consent is captured, recorded, and can be withdrawn, matched against PDPA requirements.
- Data Subject Rights Procedure : A working, actually-used process for handling access, correction, deletion, and objection requests within statutory timeframes.
- Cross-Border Transfer Documentation : Records showing any transfer of personal data outside Tanzania has genuinely been assessed and safeguarded under PDPA requirements.
- Privacy Impact Assessment Records : Documentation showing higher-risk processing activities were assessed for privacy impact before being rolled out, not after something went wrong.
- Breach Notification Procedure : A documented process for detecting a personal data breach and notifying the PDPC and affected individuals within required timeframes.
- Internal Audit and Management Review Records : A planned internal audit schedule and management review decisions showing privacy priorities are actually being tracked.
Realistic Timelines for Tanzanian Businesses
| Business Profile | Typical Total Timeline | What Drives This |
|---|---|---|
| Already ISO 27001 certified | 2.5–4 months | Privacy layer added on top of an existing security foundation |
| Building ISO 27001 and ISO 27701 together | 5–7.5 months | Full security and privacy management system built from the ground up |
| Larger organization with complex data flows | 6–9 months | Extensive records of processing and cross-border transfer documentation |
Beyond company size, the single biggest timeline driver is whether ISO 27001 is already in place, adding the privacy layer to an existing security foundation moves considerably faster than building both at once.
ISO 27701 Certification Across Tanzania’s Business Hubs
Dar es Salaam
As the hub for financial services, technology, and business process outsourcing, businesses here handle the widest concentration of sensitive personal data in the country.
Arusha
With a growing base of tourism-linked digital services and regional trade platforms, personal data handling here increasingly draws on cross-border customer relationships.
Mwanza
As a regional commercial center serving the Lake Zone, growing digital services and mobile money activity are bringing privacy considerations into sharper focus locally.
Dodoma
As the seat of government with expanding digital public services, personal data handling here increasingly intersects with public-sector data protection expectations.
Why Businesses Choose ShineCert in Tanzania?
ShineCert brings 10 years of ISO consulting experience to Tanzania’s market, coordinated through our Riyadh and India offices with services delivered remotely or on-site depending on what your engagement genuinely needs. We’ve guided more than 10,000 organizations through ISO certification worldwide, and we build every Tanzania privacy engagement around your real data processing activities and PDPC obligations, this is why Tanzanian businesses increasingly choose ShineCert as the best ISO 27701 consultant in Tanzania.
Choosing a Certification Body in Tanzania?
What to Check | Why It Matters |
Accreditation under a recognized international framework, alongside ISO 27001 | Confirms genuine, internationally recognized certification covering both security and privacy |
Real familiarity with the PDPA and PDPC’s current enforcement posture | Ensures your PIMS documentation reflects actual Tanzanian regulatory expectations, not a generic template |
Experience with your specific data processing profile | Fintech, healthcare, and education involve meaningfully different privacy considerations |
Willingness to assess your ISO 27001 foundation honestly | A weak underlying security system undermines privacy certification no matter how well the privacy layer is documented |
Ready to Get Started?
Whether you’re extending an existing ISO 27001 certification or building both together, we’ll walk through your specific data processing activities and cost factors before proposing a fixed-scope plan, delivered remotely, on-site, or however genuinely fits your project. Book a free consultation or contact us directly to get started.
Frequently Asked Questions
Look for real familiarity with the PDPA and PDPC’s current enforcement posture, experience with your specific data profile, and an honest assessment of your ISO 27001 foundation. ShineCert scopes every Tanzania engagement individually.
Yes, ISO 27701 cannot be certified on its own; it requires an existing or simultaneously implemented ISO 27001 certification underneath it.
No, PDPC registration remains a separate, mandatory requirement, but a certified privacy system gives you the documentation that makes actual compliance considerably stronger.
It depends on whether ISO 27001 is already in place, your data volume and sensitivity, and whether you transfer data across borders, we scope every project individually.
Typically two and a half to nine months depending on whether ISO 27001 is already in place and how complex your organization is, see the timeline breakdown above.
Certification doesn’t exempt you from review, but a certified, well-documented system considerably strengthens your position and tends to lead to a smoother outcome.
Documentation work runs well over remote sessions, but process verification and staff interviews genuinely benefit from in-person engagement.
Not a standalone one, we coordinate Tanzania engagements from our Riyadh and India offices, with services delivered remotely or on-site as your project requires.