
ISO 37001 Certification in Bahrain
Quick Answer
ISO 37001 is the international standard for anti-bribery management systems, and in Bahrain it addresses a genuine and evolving legal landscape. Bahrain has no standalone bribery law, bribery offenses are instead addressed through Articles 186-193 and 417-427 of the Penal Code (Decree Law No. 15 of 1976), with Law No. 1 of 2013 specifically extending coverage to private-sector bribery to align with the UN Convention Against Corruption. The General Directorate of Anti-Corruption and Economic and Electronic Security, under the Ministry of Interior, leads enforcement, and Bahrain’s Economic Vision 2030 and National Anti-Corruption Strategy both frame integrity as core to the country’s competitiveness agenda. Get certified through a body accredited under the Global Accreditation Cooperation (GAC) framework. Plan for two to four months from kickoff to certificate. Cost depends on genuine factors, third-party relationship volume, public sector exposure, geographic reach, not a flat number.
What Is ISO 37001, Technically Speaking?
ISO 37001 follows the Harmonized Structure shared with ISO 9001, ISO 14001, and ISO 27001, but its technical content addresses a genuinely distinct risk category: bribery specifically, rather than the broader corruption, fraud, cartel, or money-laundering risks that sit adjacent to it but fall outside the standard’s defined scope. This scope boundary is worth understanding precisely, ISO 37001 doesn’t claim to prevent all forms of corruption; it’s specifically designed to help organizations implement, maintain, and improve an anti-bribery management system addressing bribery by the organization, its personnel, and its business associates acting on its behalf.
The standard’s technical core is bribery risk assessment (Clause 4.5), which requires organizations to identify bribery risks specific to their actual operations, considering factors like the countries and sectors they operate in, the nature and complexity of their transactions, and their genuine exposure to public officials and other third parties who could be bribery counterparties. This risk assessment then directly informs the depth of due diligence required under Clause 8.2 for business associates, a genuinely tiered, risk-based approach rather than uniform scrutiny applied identically to every relationship.
Two technical mechanisms distinguish ISO 37001 from a generic compliance policy. First, the standard requires a genuinely independent anti-bribery compliance function (Clause 5.3), someone with the authority and resources to oversee the system, reporting to a level of management or governing body with sufficient independence from operational pressure to act without being overridden by business considerations. Second, Clause 8.9 requires financial, commercial, and contractual controls specifically designed to prevent bribery, things like tiered approval limits for gifts and hospitality, controls over facilitation payments, and financial controls that would make a bribe genuinely difficult to disguise as a legitimate transaction, such as unusually structured payments or commissions disproportionate to the service genuinely rendered.
The standard also formally requires a whistleblowing/raising concerns procedure (Clause 8.9) that genuinely protects those reporting suspected bribery from retaliation, a mechanism that only works if employees and business associates genuinely trust it, which the standard expects organizations to actively build confidence in, not just document as a policy nobody uses. For organizations bidding on Bahrain government contracts specifically, ISO 37001’s due diligence and gift/hospitality control requirements map closely onto the kind of integrity expectations increasingly embedded in Tender Board evaluation and post-award compliance monitoring.
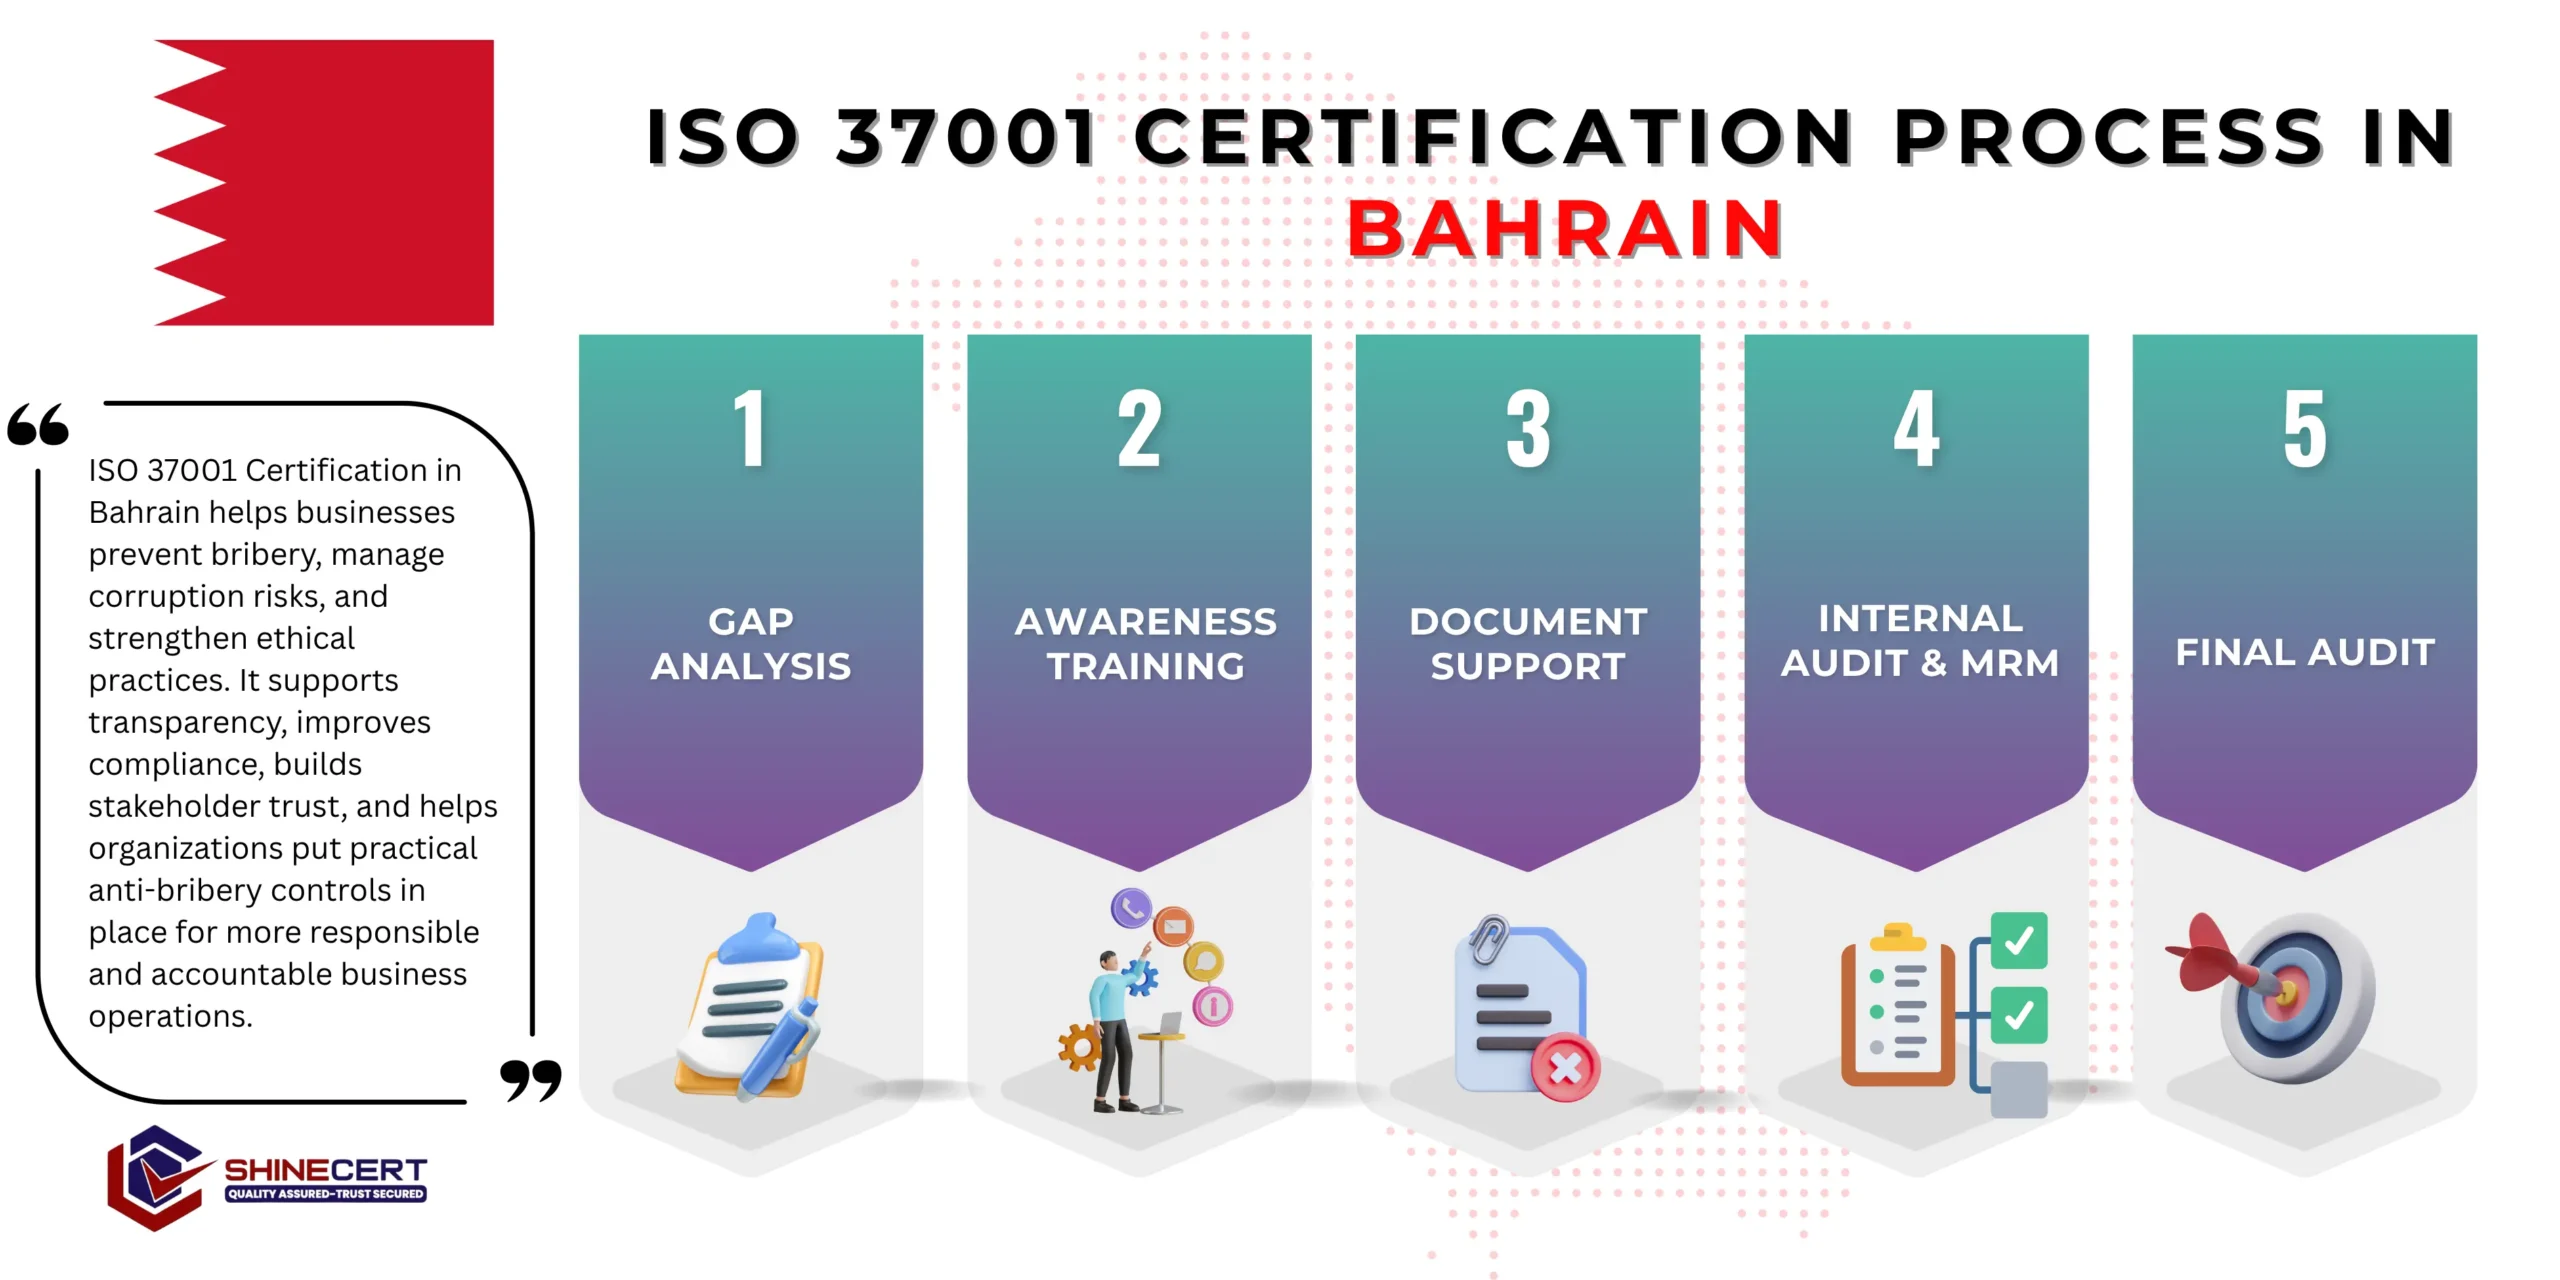
What are the steps to get ISO 37001 Certification in Bahrain?
our services
- ISO Certification Bahrain
- ISO 9001 Certification Bahrain
- ISO 14001 Certification Bahrain
- ISO 27001 Certification Bahrain
- ISO 22000 Certification Bahrain
- ISO 27701 Certification Bahrain
- ISO 45001 Certification Bahrain
- ISO 20000-1 Certification Bahrain
- ISO 13485 Certification Bahrain
- ISO 17025 Certification Bahrain
- ISO 31000 Certification Bahrain
- ISO 42001 Certification Bahrain
- ISO 37001 Certification Bahrain
- ISO 22301 Certification Bahrain
- ISO 50001 Certification Bahrain
- CE Mark Certification Bahrain
- GDPR Certification Bahrain
- GMP Certification Bahrain
- Halal Certification Bahrain
Our Five-Step Certification Process: What to Actually Expect
Bribery Risk Assessment
We evaluate your genuine bribery exposure, which markets, relationships, and transaction types carry real risk. What this means for you: a risk-based system that focuses genuine scrutiny where it matters, rather than uniform bureaucracy applied everywhere equally.
A bribery risk assessment report specific to your operations.
Documentation Development
Your anti-bribery policy, due diligence framework, and financial controls get built around your actual risk profile. What this means for you: controls your finance and procurement teams can genuinely apply, not an abstract policy disconnected from real transaction processes.
A complete ISO 37001 documentation set.
Implementation and Training
Controls roll out across procurement, sales, and third-party relationship management, with staff and key business associates trained on genuine red-flag recognition. What this means for you: your team knows what a suspicious payment structure or unusual commission actually looks like, not just abstract policy language.
Training records and evidence of controls functioning in daily operations.
Internal Audit and Management Review
We test the system internally, surfacing weaknesses before the real audit. What this means for you: control gaps get caught and fixed in a low-stakes setting.
Internal audit report and management review minutes.
Certification Audit
Stage 1 and Stage 2 audits with a GAC-accredited certification body. What this means for you: Stage 1 checks documentation readiness; Stage 2 verifies controls genuinely function, including due diligence records and whistleblowing channel evidence.
Your ISO 37001 certificate and a surveillance audit schedule.
Why This Matters So Much in Bahrain Specifically?
- Bahrain’s legal framework for bribery, built through Penal Code amendments rather than a dedicated standalone statute, creates a genuine need for organizations to translate general Penal Code provisions into concrete, operational controls specific to their own risk exposure, since the law itself doesn’t prescribe a specific compliance program structure the way some jurisdictions’ anti-bribery statutes do. ISO 37001 fills exactly this gap, giving organizations an internationally recognized, structured way to demonstrate genuine anti-bribery diligence that maps onto Bahrain’s Penal Code bribery provisions.
- For companies bidding on Tender Board contracts, integrity and anti-corruption controls increasingly feature in both pre-qualification and ongoing contract compliance monitoring, consistent with Economic Vision 2030’s genuine emphasis on governance quality as part of national competitiveness. Companies operating across multiple GCC or international markets also find ISO 37001 gives them a single, consistent anti-bribery framework that can flex to different local legal contexts while maintaining one coherent internal control structure.
Bahrain at a Glance: What Shapes ISO 37001 Demand Here
01
No standalone bribery law
bribery offenses are addressed through the Penal Code (Decree Law No. 15 of 1976), Articles 186-193 and 417-427, covering bribery of public officials.
02
Private-sector extension
Law No. 1 of 2013 amended the Penal Code to explicitly cover private-sector bribery and corruption, aligning Bahrain with UN Convention Against Corruption obligations.
03
Enforcement authority
the General Directorate of Anti-Corruption and Economic and Electronic Security, under the Ministry of Interior, leads investigation and enforcement, working through community partnerships.
04
National strategy
Economic Vision 2030 and Bahrain’s National Anti-Corruption Strategy both explicitly frame integrity and anti-corruption as core to the country’s competitiveness and governance agenda
What Actually Drives Your Cost?
We don’t quote a flat number, because a flat number would misrepresent how different two Bahrain companies’ actual bribery exposure can be. Here’s what genuinely drives cost :
A company with a handful of low-risk domestic vendor relationships needs meaningfully less due diligence infrastructure than one with dozens of agents and distributors across higher-risk markets.
Companies regularly bidding on Tender Board or other government contracts need deeper controls around gifts, hospitality, and public official interactions than purely private-sector businesses.
Operations spanning multiple countries with varying corruption risk levels need a more sophisticated, tiered risk assessment than single-market domestic operations.
Businesses with complex commission structures, intermediary payments, or joint venture arrangements need deeper financial control documentation.
Companies with some existing due diligence or approval processes aren’t starting from zero. Companies relying purely on informal trust need more foundational work.
Pursuing ISO 9001 or ISO 27001 alongside ISO 37001 shares meaningful management review and internal audit infrastructure.
An internal compliance or legal lead who can own documentation reduces consultant hours needed.
Where your project qualifies for co-funding, your genuine out-of-pocket cost can be meaningfully lower.
A compressed timeline driven by a partnership or tender deadline sometimes needs more concentrated consultant hours in a shorter window.
Common Pitfalls We See in Bahrain ISO 37001 Projects
- Applying uniform due diligence regardless of actual risk : Treating every business associate with identical, maximum scrutiny wastes resources on low-risk relationships while potentially under-resourcing genuinely high-risk ones, the standard expects a genuinely tiered, risk-based approach.
- Building a whistleblowing channel nobody trusts : A reporting mechanism that exists on paper but that employees don’t genuinely believe protects them from retaliation produces silence, not early warning.
- Treating gift and hospitality controls as a formality : Vague or unenforced thresholds tend to erode in practice, genuine controls need clear limits and consistent, visible enforcement.
- Assuming general Penal Code awareness substitutes for a structured system : Bahrain’s Penal Code bribery provisions establish legal liability, but they don’t prescribe a specific operational compliance program, companies need to build that structure themselves, and ISO 37001 provides the framework for doing so.
Benefits at a Glance
01
Structured framework mapping to Bahrain’s Penal Code bribery provisions
02
Stronger positioning in Tender Board pre-qualification and compliance monitoring
03
Reduced legal and reputational exposure from third-party relationships
04
Access to potential Tamkeen funding support
05
A consistent framework for multi-market GCC and international operations
Benefits: What Certification Actually Changes
- Defensible, documented anti-bribery diligence : In the event of an allegation or investigation, a genuinely functioning ISO 37001 system gives an organization concrete evidence of proactive controls, rather than relying on an informal claim of good faith.
- Stronger Tender Board positioning : Certification increasingly differentiates bidders on integrity grounds, alongside quality and safety credentials, in competitive government procurement evaluation.
- Reduced third-party relationship risk : Risk-based due diligence genuinely reduces the likelihood of an agent, distributor, or subcontractor engaging in bribery on the organization’s behalf without its knowledge.
- A trusted whistleblowing channel : A genuinely functioning, trusted reporting mechanism surfaces problems while they’re still manageable, rather than after they’ve escalated into a genuine scandal.
- Access to Tamkeen-supported funding : Depending on eligibility, certification-related training and consulting costs may be partially offset through Tamkeen’s programs.
What Happens When a Bahrain Company Operates Without Structured Anti-Bribery Controls?
- This is worth understanding concretely. Without structured due diligence and financial controls, a company remains genuinely exposed to bribery committed by an agent, distributor, or subcontractor acting on its behalf, exposure that can trigger real Penal Code liability even where company leadership had no direct knowledge of the specific act. Companies bidding on Tender Board contracts without demonstrable integrity controls also increasingly find themselves at a competitive disadvantage as procurement evaluation criteria give more explicit weight to governance and anti-corruption credentials.
- Companies that discover control gaps only after an allegation or investigation face significantly more costly and reputationally damaging remediation than those who build genuine controls proactively. We generally recommend Bahrain companies with meaningful third-party relationships or public-sector exposure treat ISO 37001 as standing infrastructure, not something to build only once a specific partner or tender requires it.
Anti-Bribery Requirements, Clause by Clause
- Context of the Organization (Clause 4) : Includes the specific bribery risk assessment, genuinely mapping which of your operations, markets, and relationships carry meaningful bribery exposure.
- Leadership (Clause 5) : Requires a genuinely independent anti-bribery compliance function with real authority and reporting access, plus top management commitment that goes beyond a signed policy.
- Planning (Clause 6) : Objectives and plans specifically addressing identified bribery risks, tied to measurable action.
- Support (Clause 7) : Competence and training requirements ensuring staff and relevant business associates genuinely understand bribery red flags relevant to their specific role.
- Operation (Clause 8) : The largest clause, due diligence on business associates, financial and commercial controls, gift and hospitality controls, facilitation payment controls, and the whistleblowing procedure.
- Performance Evaluation (Clause 9) : Monitoring, measurement, and internal audit test whether controls are genuinely catching red flags, not just existing on paper.
- Improvement (Clause 10) : Structured handling of bribery concerns and nonconformities, with genuine investigation and corrective action.
Tamkeen Funding: Does Your ISO 37001 Project Qualify for Subsidy?
Tamkeen’s training and business development programs can apply to anti-bribery management system implementation, particularly training-related costs, depending on your company’s size, sector, and program eligibility. We generally recommend checking your Tamkeen eligibility before finalizing your certification budget.
Applicable Standards by Industry
Construction and Contracting
Companies bidding on Tender Board and large private developments use ISO 37001 to demonstrate integrity alongside quality and safety credentials.
Read moreTrading and Distribution
Companies working through agents and distributors across multiple markets use ISO 37001 to structure due diligence and commission controls.
Read moreOil, Gas, and Industrial Services
Contractors and suppliers in high-value industrial supply chains use ISO 37001 given the genuine bribery risk profile of large contract values.
Read moreFinancial Services
Institutions use ISO 37001 alongside CBB regulatory expectations to formalize anti-bribery controls within broader governance frameworks.
Read moreProfessional Services and Consultancies
Firms advising on public sector engagements use ISO 37001 to demonstrate their own integrity standards to clients and regulators.
Read moreCase Study: A Bahrain Trading Company’s Anti-Bribery Program Buildout
- The following is an illustrative, composite example based on the kind of project ShineCert typically runs, not a specific named client. A Bahrain-based trading company working with agents across several regional markets had a general anti-corruption statement in its employee handbook, but no formal due diligence process for onboarding new agents and no structured controls around commission payments. The trigger was a new international supplier partnership that specifically required evidence of a certified anti-bribery management system as a condition of the agreement.
- The gap assessment found the company’s genuine risk exposure was concentrated in a handful of agent relationships in markets with elevated bribery risk, while most of its operations carried comparatively low exposure. The bulk of implementation work went into building tiered due diligence, deeper scrutiny for the higher-risk agent relationships, lighter-touch review for lower-risk ones, and formalizing commission payment controls that flagged payments disproportionate to the services genuinely documented. The company also established a genuinely independent whistleblowing channel, addressing a prior gap where concerns had nowhere clear to go. Certification was achieved in time to secure the international partnership, and the pattern we typically see afterward held: the tiered due diligence process surfaced a previously unaddressed red flag in one agent relationship, allowing the company to address it proactively rather than discovering it during an actual incident.
Mandatory Documents Required for Certification
Genuine leadership commitment specific to your organization’s risk profile.
Documented, defining exactly which operations and business associates are covered.
Reflecting your actual markets, relationships, and transaction types.
Tiered by genuine risk level for business associates.
Covering gifts, hospitality, facilitation payments, and approval thresholds.
Evidence of a genuinely functioning, trusted reporting channel.
Why ShineCert?
We coordinate Bahrain engagements from ShineCert’s Riyadh and Lebanon offices, with direct familiarity with Bahrain’s Penal Code bribery provisions, Tender Board integrity expectations, and Tamkeen’s funding programs. Our team has guided more than 10,000 organizations through ISO certification globally, with the best ISO 37001 consultant in Bahrain, and we build every Bahrain anti-bribery engagement around your actual third-party relationships, market exposure, and funding eligibility, not a one-size-fits-all package.
Choosing a Certification Body in Bahrain?
What to Check | Why It Matters |
Accreditation under the GAC framework | Confirms genuine, internationally recognized certification |
Genuine understanding of Bahrain’s Penal Code bribery provisions | Ensures the auditor connects the system to actual local legal exposure |
Experience with Tender Board integrity expectations | Helps ensure certification genuinely strengthens government bid competitiveness |
Sector-specific due diligence experience | Trading, construction, and financial services each involve meaningfully different bribery risk profiles |
Ready to Get Certified?
ShineCert supports Bahrain organizations from initial bribery risk assessment through certification audit, including checking whether your project qualifies for Tamkeen funding support. Book a free consultation or contact us directly, and we’ll walk through your specific third-party relationships and cost factors before proposing a fixed-scope plan.
Frequently Asked Questions
It’s the international standard for anti-bribery management systems, setting requirements for preventing, detecting, and responding to bribery risk.
No, bribery is addressed through Penal Code provisions (Decree Law No. 15 of 1976), with Law No. 1 of 2013 extending coverage to private-sector bribery.
It genuinely depends on factors like third-party relationship volume, public sector exposure, and geographic complexity, we scope every project individually.
Typically two to four months.
Potentially, Tamkeen’s training and development programs can apply to certification-related costs depending on eligibility.
Not universally mandatory, but integrity and anti-corruption controls increasingly feature in Tender Board pre-qualification and compliance monitoring.
No, it’s specifically scoped to bribery risk, not the broader categories of fraud, cartel behavior, or money laundering, which fall outside its defined scope.
A genuinely risk-based, tiered approach, deeper scrutiny for higher-risk relationships, proportionate lighter-touch review for lower-risk ones.
Yes, each relationship needs its own risk-based due diligence assessment, so companies with extensive agent networks face meaningfully more implementation work.
We coordinate Bahrain engagements from our Riyadh and Lebanon offices, with consultants traveling on-site as needed.