
ISO 20000-1 Certification in Bahrain
Quick Answer
ISO/IEC 20000-1 is the international standard for IT service management systems, and in Bahrain it operates in a market shaped by the Telecommunications Regulatory Authority’s (TRA) genuine focus on infrastructure resilience and cybersecurity readiness, Bahrain has ranked highly on the International Telecommunications Union’s Cyber Security Readiness Maturity Index, reflecting sustained national investment in telecom sector reliability. For IT service providers and enterprise IT functions, ISO 20000-1 formalizes exactly the kind of structured, measurable service delivery this environment increasingly expects. Get certified through a body accredited under the Global Accreditation Cooperation (GAC) framework. Plan for three to five months from kickoff to certificate. Cost depends on genuine factors, service complexity, number of clients or business units served, existing process maturity, not a flat number.
What Is ISO 20000-1, Technically Speaking?
ISO/IEC 20000-1 is the certifiable standard within the ISO/IEC 20000 family, built on IT Service Management (ITSM) principles closely related to, but formally distinct from, the ITIL (IT Infrastructure Library) framework widely used in IT operations. It’s worth understanding this relationship precisely: ITIL is a detailed best-practice framework offering extensive practical guidance on how to run IT service management processes, while ISO 20000-1 is the leaner, certifiable standard defining what a genuine service management system must achieve, many organizations use ITIL’s detailed guidance to help satisfy ISO 20000-1’s more streamlined, auditable requirements, but the two are not identical, and certification is against ISO 20000-1 specifically, not ITIL.
The standard’s technical structure, like other current ISO management system standards, follows the Harmonized Structure, but its Clause 8 (Operation) carries genuinely IT-specific service management processes: service level management, service reporting, capacity and availability management, information security controls specific to service delivery, service continuity management, budgeting and accounting for services, incident and service request management, problem management, and control processes covering configuration, change, and release management. This is a substantially more detailed operational clause than in more generic management system standards, reflecting the genuine operational complexity of running IT services reliably.
Service Level Management deserves particular technical attention: the standard requires organizations to establish, agree, record, and manage service level agreements (SLAs), and critically, to genuinely monitor and report performance against those agreements, not just document that an SLA exists, but demonstrate ongoing, measured conformance to it. This connects directly to the standard’s approach to Configuration Management, which requires organizations to maintain accurate information about configuration items (the components making up IT services) sufficient to support effective service delivery and change management, without accurate configuration information, an organization genuinely cannot reliably assess the impact of a planned change or diagnose the root cause of an incident.
The standard also formally addresses the “service integration” scenario increasingly relevant to modern IT environments, where an organization’s overall service delivery depends on multiple internal teams and external suppliers working together. Clause 8.3’s Supplier Management requirements specifically address managing multiple suppliers as an integrated whole, recognizing that a service failure’s root cause frequently sits at the boundary between two parties’ responsibilities rather than cleanly within either one, a genuinely common, genuinely difficult operational reality for managed service providers and IT departments relying on cloud providers, network carriers, and specialized vendors simultaneously.
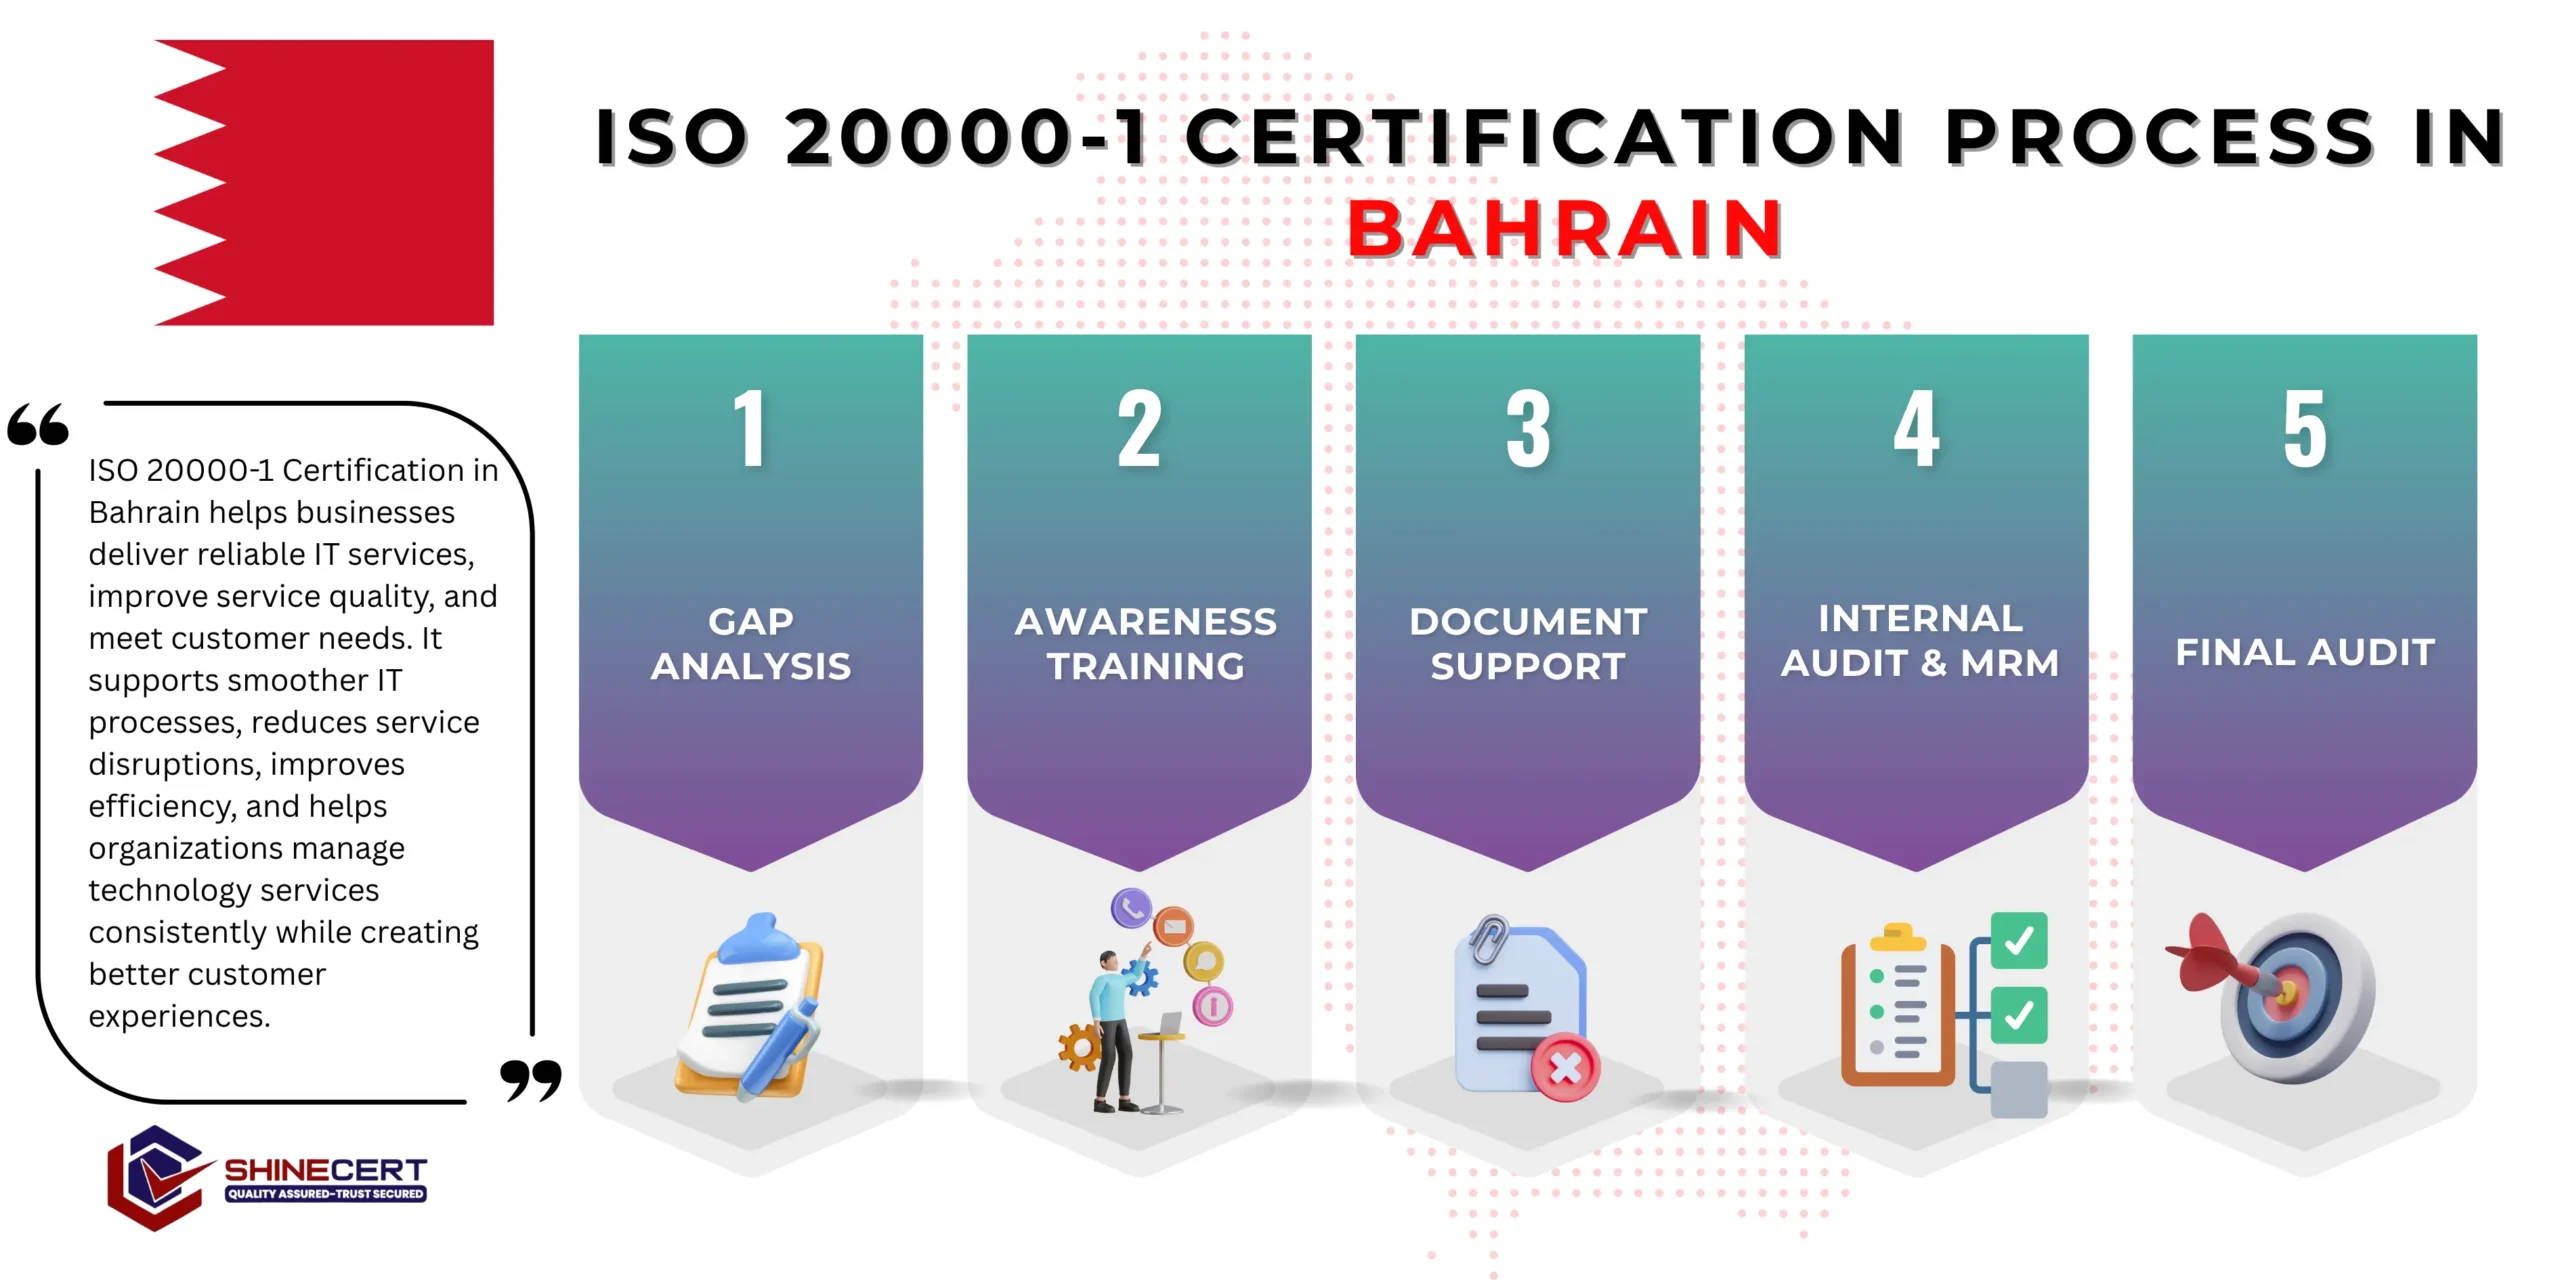
What are the steps to get ISO 20000-1 Certification in Bahrain?
our services
- ISO Certification Bahrain
- ISO 9001 Certification Bahrain
- ISO 14001 Certification Bahrain
- ISO 27001 Certification Bahrain
- ISO 22000 Certification Bahrain
- ISO 27701 Certification Bahrain
- ISO 45001 Certification Bahrain
- ISO 20000-1 Certification Bahrain
- ISO 13485 Certification Bahrain
- ISO 17025 Certification Bahrain
- ISO 31000 Certification Bahrain
- ISO 42001 Certification Bahrain
- ISO 37001 Certification Bahrain
- ISO 22301 Certification Bahrain
- ISO 50001 Certification Bahrain
- CE Mark Certification Bahrain
- GDPR Certification Bahrain
- GMP Certification Bahrain
- Halal Certification Bahrain
Our Five-Step Certification Process: What to Actually Expect
Gap Assessment
We evaluate your current service management practices against ISO 20000-1’s requirements, including existing SLA and incident management processes. What this means for you: an honest picture of the real gap between your current operations and what genuine certification requires.
A gap assessment report specific to your services and client relationships.
Documentation Development
Your service management policy, SLAs, service catalog, and process documentation get built around your actual service portfolio. What this means for you: documentation your operations team can genuinely use to run daily service delivery, not a generic template.
A complete ISO 20000-1 documentation set.
Implementation and Training
Processes roll out across incident, problem, change, and configuration management, with staff trained on their specific roles. What this means for you: this phase typically takes longest for organizations building configuration management discipline from scratch, since accurate configuration data takes real time to establish.
Training records and evidence of processes functioning across service delivery.
Internal Audit and Management Review
We test the system internally, surfacing weaknesses before the real audit. What this means for you: SLA gaps and process weaknesses get caught and fixed in a low-stakes setting.
Internal audit report and management review minutes.
Certification Audit
Stage 1 and Stage 2 audits with a GAC-accredited certification body. What this means for you: Stage 1 checks documentation readiness; Stage 2 verifies processes genuinely function and SLAs are genuinely being monitored.
Your ISO 20000-1 certificate and a surveillance audit schedule.
Why This Matters So Much in Bahrain Specifically?
- Bahrain’s genuine digital advancement, reflected in its strong ITU cybersecurity readiness standing and its broader digital government leadership ambitions, creates real expectations for the IT service providers and enterprise IT functions supporting that ecosystem. Organizations delivering IT services to government bodies, financial institutions, or enterprise clients increasingly need to demonstrate structured, measurable service delivery discipline, not just technical competence, particularly as TRA’s regulatory focus on infrastructure resilience filters down into genuine expectations from the organizations operating within that infrastructure.
- For managed service providers specifically, ISO 20000-1 certification is increasingly a genuine differentiator in competitive procurement, giving potential clients independently verified evidence of service management maturity rather than relying entirely on sales claims and reference checks.
Bahrain at a Glance: What Shapes ISO 20000-1 Demand Here
01
Telecom regulator
the Telecommunications Regulatory Authority (TRA), established in 2002 under Bahrain’s Telecommunications Law, oversees licensing, technical operations, and cybersecurity readiness across the telecom sector.
02
Strong cybersecurity readiness standing
Bahrain has ranked highly on the ITU’s Cyber Security Readiness Maturity Index, reflecting genuine national investment in telecom infrastructure resilience.
03
Digital government leadership
Bahrain’s broader digital transformation agenda creates real expectations for reliable, measurable IT service delivery across both government and private-sector technology providers.
04
SME funding available
Tamkeen offers training and business development grants that can offset certification-related costs for eligible companies.
What Actually Drives Your Cost?
We don’t quote a flat number, because a flat number would misrepresent how different two Bahrain IT providers’ actual service complexity can be. Here’s what genuinely drives cost :
A provider offering a narrow, standardized service set needs meaningfully less documentation depth than one offering diverse, highly customized services to different clients.
Each distinct client relationship generally needs its own SLA definition and monitoring, adding genuine scope for providers with larger client portfolios.
Organizations with some existing asset or configuration tracking aren’t starting from zero. Organizations relying purely on individual engineer knowledge need substantial foundational work.
Providers relying on multiple external suppliers (cloud providers, network carriers, specialized vendors) need deeper supplier management documentation.
Providers with functioning ticketing and escalation processes aren’t starting from zero, though formalizing genuine root-cause problem management often still requires real work.
Pursuing ISO 27001 alongside ISO 20000-1 shares meaningful risk assessment and information security control infrastructure, particularly relevant for IT service providers.
An internal service delivery or operations lead who can own documentation reduces consultant hours needed.
Where your project qualifies for co-funding, your genuine out-of-pocket cost can be meaningfully lower.
A compressed timeline driven by a competitive retender deadline sometimes needs more concentrated consultant hours in a shorter window.
Common Pitfalls We See in Bahrain ISO 20000-1 Projects
- Treating SLAs as contractual language rather than genuinely monitored metrics : An SLA that exists only in a contract, without systematic performance measurement and reporting, doesn’t satisfy the standard’s genuine intent and leaves real performance invisible.
- Relying on individual knowledge instead of shared configuration records : Configuration information that lives only in specific engineers’ heads creates genuine operational risk when those individuals are unavailable or leave, and doesn’t satisfy the standard’s documented information requirements.
- Confusing ITIL adoption with ISO 20000-1 certification : Following ITIL best practices is genuinely valuable, but it doesn’t automatically satisfy ISO 20000-1’s specific, auditable requirements, the two need to be explicitly connected during implementation.
- Underestimating supplier management for multi-vendor environments : Providers relying on multiple external suppliers sometimes document only their own internal processes, missing the standard’s explicit requirement to manage the multi-supplier ecosystem as an integrated whole.
Benefits at a Glance
01
Independently verified service delivery credential for enterprise and government clients
02
Structured alignment with Bahrain’s digital resilience and cybersecurity expectations
03
Reduced incident frequency and faster, more consistent resolution
04
Access to potential Tamkeen funding support
05
A foundation that shares infrastructure with ISO 27001
Benefits: What Certification Actually Changes
- Independently verified service delivery credibility : Certification gives potential clients concrete, third-party-verified evidence of your service management maturity, differentiating you from competitors relying solely on marketing claims.
- More consistent, measurable service quality : Structured SLA monitoring and reporting genuinely reduces the gap between promised and delivered service levels, and surfaces performance issues before clients need to escalate them.
- Faster incident resolution through genuine configuration and problem management : Accurate configuration information and structured root-cause analysis reduce both the time to resolve incidents and the recurrence of the same underlying problems.
- Better-managed supplier and partner relationships : Formal supplier management processes reduce the risk of service failures falling into unmanaged gaps between your organization and external providers.
- Access to Tamkeen-supported funding : Depending on eligibility, certification-related training and consulting costs may be partially offset through Tamkeen’s programs.
What Happens When a Bahrain IT Provider Operates Without Certification?
- This is worth understanding concretely. Operating without a certified service management system doesn’t necessarily mean poor service, many uncertified providers deliver genuinely good technical support, but it does mean an inability to demonstrate that quality with independent, verifiable evidence, and an ongoing risk that genuine strengths (or weaknesses) remain invisible without systematic measurement. In competitive procurement processes where clients explicitly favor or require ISO 20000-1 certification, uncertified providers face a genuine disadvantage regardless of their actual technical capability.
- Providers that discover this only after losing a competitive pretender to a certified competitor often start certification under real time pressure. We generally recommend Bahrain IT service providers serving enterprise or government clients treat ISO 20000-1 as standing infrastructure to have in place before a competitive procurement process demands it.
IT Service Management Requirements, Clause by Clause
- Context of the Organization (Clause 4) : Mapping your genuine service delivery context, which services you provide, to whom, and which interested parties (clients, suppliers, TRA where relevant) have a stake in service quality.
- Leadership (Clause 5) : Top management accountability for service management, including genuine resourcing for the service management system, not delegation entirely to a technical operations team disconnected from leadership decisions.
- Planning (Clause 6) : Risk-based planning specific to service delivery risk, plus planning for changes to the service management system itself.
- Support (Clause 7) : Competence, awareness, and documented information requirements ensuring staff genuinely understand their role in service delivery and change control.
- Operation (Clause 8) : The largest and most technical clause, covering service level management, capacity, availability, continuity, information security, budgeting, incident, problem, configuration, change, release, and supplier management.
- Performance Evaluation (Clause 9) : Monitoring, measurement, and internal audit test whether service levels are genuinely being met, not just documented as targets.
- Improvement (Clause 10) : Structured handling of service nonconformities, with genuine root-cause problem management feeding back into service improvement.
Tamkeen Funding: Does Your ISO 20000-1 Project Qualify for Subsidy?
Tamkeen’s training and business development programs can apply to IT service management system implementation, depending on your company’s size, sector, and program eligibility. We generally recommend checking your Tamkeen eligibility before finalizing your certification budget.
Applicable Standards by Industry
Managed IT Service Providers
MSPs use ISO 20000-1 as a genuine competitive differentiator in enterprise and government procurement.
Read moreFinancial Services IT
In-house IT functions and technology vendors serving CBB-regulated institutions use ISO 20000-1 alongside ISO 27001 to demonstrate structured, secure service delivery.
Read moreGovernment Technology Contractors
Providers delivering IT services to government bodies find certification increasingly favored or required in procurement evaluation.
Read moreTelecommunications
Companies operating within TRA’s regulatory scope use ISO 20000-1 to formalize service delivery discipline alongside cybersecurity readiness expectations.
Read moreEnterprise Internal IT Departments
Large organizations’ internal IT functions use ISO 20000-1 to professionalize service delivery to internal business units.
Read moreCase Study: A Bahrain Managed Service Provider’s Certification Journey
- The following is an illustrative, composite example based on the kind of project ShineCert typically runs, not a specific named client. A Bahrain-based managed service provider supporting several enterprise clients had capable technical staff and generally responsive support, but SLAs existed mostly as contractual language rather than genuinely monitored, reported metrics, and configuration information for client environments lived informally across individual engineers’ knowledge rather than a shared, accurate record. The trigger was a competitive retender from a major client that explicitly favored ISO 20000-1 certified providers in its evaluation criteria.
- The gap assessment found the company’s actual incident response was genuinely fast in practice, but it couldn’t demonstrate this with data, SLA performance simply wasn’t being systematically measured and reported, meaning the company’s real strength was invisible in client conversations. The bulk of implementation work went into building genuine SLA monitoring and reporting, establishing a shared configuration management record replacing scattered individual engineer knowledge, and formalizing problem management to track recurring incidents back to root causes rather than repeatedly fixing the same symptom. Certification was achieved in time for the retender, and the pattern we typically see afterward held: the newly visible SLA performance data, genuinely strong once actually measured, became a significant differentiator in the client conversation, turning an invisible strength into a demonstrable one.
Mandatory Documents Required for Certification
Genuine leadership commitment specific to your service portfolio.
Documented, defining exactly which services and clients are covered.
Reflecting your actual service commitments, with defined, monitored performance targets.
Accurate, current information about service components.
Documented, with clear escalation and root-cause analysis requirements.
Evidence of genuine, ongoing oversight.
Why ShineCert?
We coordinate Bahrain engagements from ShineCert’s Riyadh and Lebanon offices, with direct familiarity with TRA’s regulatory environment and Tamkeen’s funding programs. Our team has guided more than 10,000 organizations through ISO certification globally, with the best ISO 20000-1 consultant in Bahrain, and we build every Bahrain IT service management engagement around your actual service portfolio, client base, and funding eligibility, not a one-size-fits-all package.
Choosing a Certification Body in Bahrain?
What to Check | Why It Matters |
Accreditation under the GAC framework | Confirms genuine, internationally recognized certification |
Genuine ITSM technical expertise | Ensures the auditor can meaningfully assess SLA monitoring, configuration management, and problem management maturity |
Experience with multi-supplier service environments | Particularly relevant for providers integrating multiple external suppliers |
Sector-specific IT service audit experience | Managed services, financial IT, and government technology each involve meaningfully different service expectations |
Ready to Get Certified?
ShineCert supports Bahrain IT service providers from initial gap assessment through certification audit, including checking whether your project qualifies for Tamkeen funding support. Book a free consultation or contact us directly, and we’ll walk through your specific service portfolio and cost factors before proposing a fixed-scope plan.
Frequently Asked Questions
It’s the international standard for IT service management systems, setting requirements for delivering, monitoring, and continually improving IT services.
It genuinely depends on factors like service complexity, number of clients served, and existing process maturity, we scope every project individually.
ITIL is a detailed best-practice framework for running IT service management processes; ISO 20000-1 is the leaner, certifiable standard defining what a service management system must achieve, often implemented using ITIL’s practical guidance.
Typically three to five months.
Potentially, Tamkeen’s training and development programs can apply to certification-related costs depending on eligibility.
Not as a blanket mandate, but it supports the broader cybersecurity and infrastructure resilience expectations TRA’s regulatory environment reflects.
Not strictly required, though many organizations find ITIL’s detailed guidance genuinely useful for building the specific processes ISO 20000-1 requires.
It includes information security controls specific to service delivery, but organizations handling sensitive data typically pursue ISO 27001 alongside it for comprehensive security management.
Yes, each distinct client relationship generally needs its own SLA definition and monitoring, adding genuine scope.
We coordinate Bahrain engagements from our Riyadh and Lebanon offices, with consultants traveling on-site as needed.