
ISO 27701 Certification in Bahrain
Quick Answer
ISO 27701 is the international extension standard that adds Privacy Information Management System (PIMS) requirements on top of an existing ISO 27001 Information Security Management System. In Bahrain, it addresses exactly the gap left by ISO 27001 alone: while ISO 27001 provides a strong information security foundation, Bahrain’s Personal Data Protection Law (Law No. 30 of 2018, in force since August 2019) imposes specific obligations around data subject rights, consent management, and cross-border data transfers that ISO 27701 formally structures. The Personal Data Protection Authority, operating under the Ministry of Justice, Islamic Affairs, and Waqf, holds genuine investigation, audit, and penalty powers under the PDPL. Get certified through a body accredited under the Global Accreditation Cooperation (GAC) framework, and note that ISO 27701 requires an existing or simultaneous ISO 27001 certification as its foundation. Plan for two to three months for the extension, assuming ISO 27001 is already in place. Cost depends on genuine factors, data volume, processing complexity, cross-border transfer activity, not a flat number.
What Is ISO 27701, Technically Speaking?
ISO 27701 is not a standalone standard, it is formally structured as an extension to ISO 27001 and ISO 27002, adding privacy-specific requirements and controls on top of an organization’s existing information security management system rather than replacing or duplicating it. This is a genuinely important technical point: an organization cannot pursue ISO 27701 certification without an ISO 27001 foundation already in place or being implemented simultaneously, because ISO 27701’s structure literally extends ISO 27001’s clauses with privacy-specific additions rather than standing on its own.
The standard’s core technical contribution is formalizing the distinction between two roles under privacy law: the PII Controller (an organization that determines the purposes and means of processing personal data, broadly, the entity making decisions about why and how data is used) and the PII Processor (an organization that processes personal data on behalf of a controller, typically under contract, without independently determining the purposes of processing). This distinction matters enormously in practice because the two roles carry genuinely different obligations, a controller has direct data subject rights obligations, while a processor’s obligations largely flow through contractual terms with the controller. ISO 27701 provides separate control sets for each role (Annex A for controllers, Annex B for processors), reflecting this real legal and operational distinction rather than treating all “privacy work” identically.
Technically, ISO 27701 requires organizations to build genuine, operational mechanisms for the rights PDPL grants Bahrain data subjects, access requests, correction requests, and deletion requests need documented, auditable procedures with defined response timeframes, not an ad hoc email-based process improvised each time a request arrives. The standard also formalizes consent management as a genuine technical and procedural discipline: documenting what consent was obtained, for what specific purpose, when, and how it can be withdrawn, directly addressing PDPL’s consent requirements in a structured, auditable way.
Cross-border data transfer is another area where ISO 27701 provides genuine technical structure relevant to Bahrain: the standard requires organizations to document and assess the safeguards applied when personal data moves outside the jurisdiction, which for Bahrain-based organizations transferring data internationally, common for cloud-hosted services or international group companies, means building a defensible, documented basis for those transfers rather than assuming international data flows are automatically fine.
Because ISO 27701 builds directly on ISO 27001’s risk assessment and Statement of Applicability process, privacy risks get assessed using the same rigorous methodology as security risks, extended to cover genuinely privacy-specific concerns like re-identification risk (the possibility that supposedly anonymized data could be traced back to a specific individual) and purpose limitation (ensuring data collected for one purpose isn’t quietly repurposed for another without a proper legal basis).
What are the steps to get ISO 27701 Certification in Bahrain?
our services
- ISO Certification Bahrain
- ISO 9001 Certification Bahrain
- ISO 14001 Certification Bahrain
- ISO 27001 Certification Bahrain
- ISO 22000 Certification Bahrain
- ISO 27701 Certification Bahrain
- ISO 45001 Certification Bahrain
- ISO 20000-1 Certification Bahrain
- ISO 13485 Certification Bahrain
- ISO 17025 Certification Bahrain
- ISO 31000 Certification Bahrain
- ISO 42001 Certification Bahrain
- ISO 37001 Certification Bahrain
- ISO 22301 Certification Bahrain
- ISO 50001 Certification Bahrain
- CE Mark Certification Bahrain
- GDPR Certification Bahrain
- GMP Certification Bahrain
- Halal Certification Bahrain
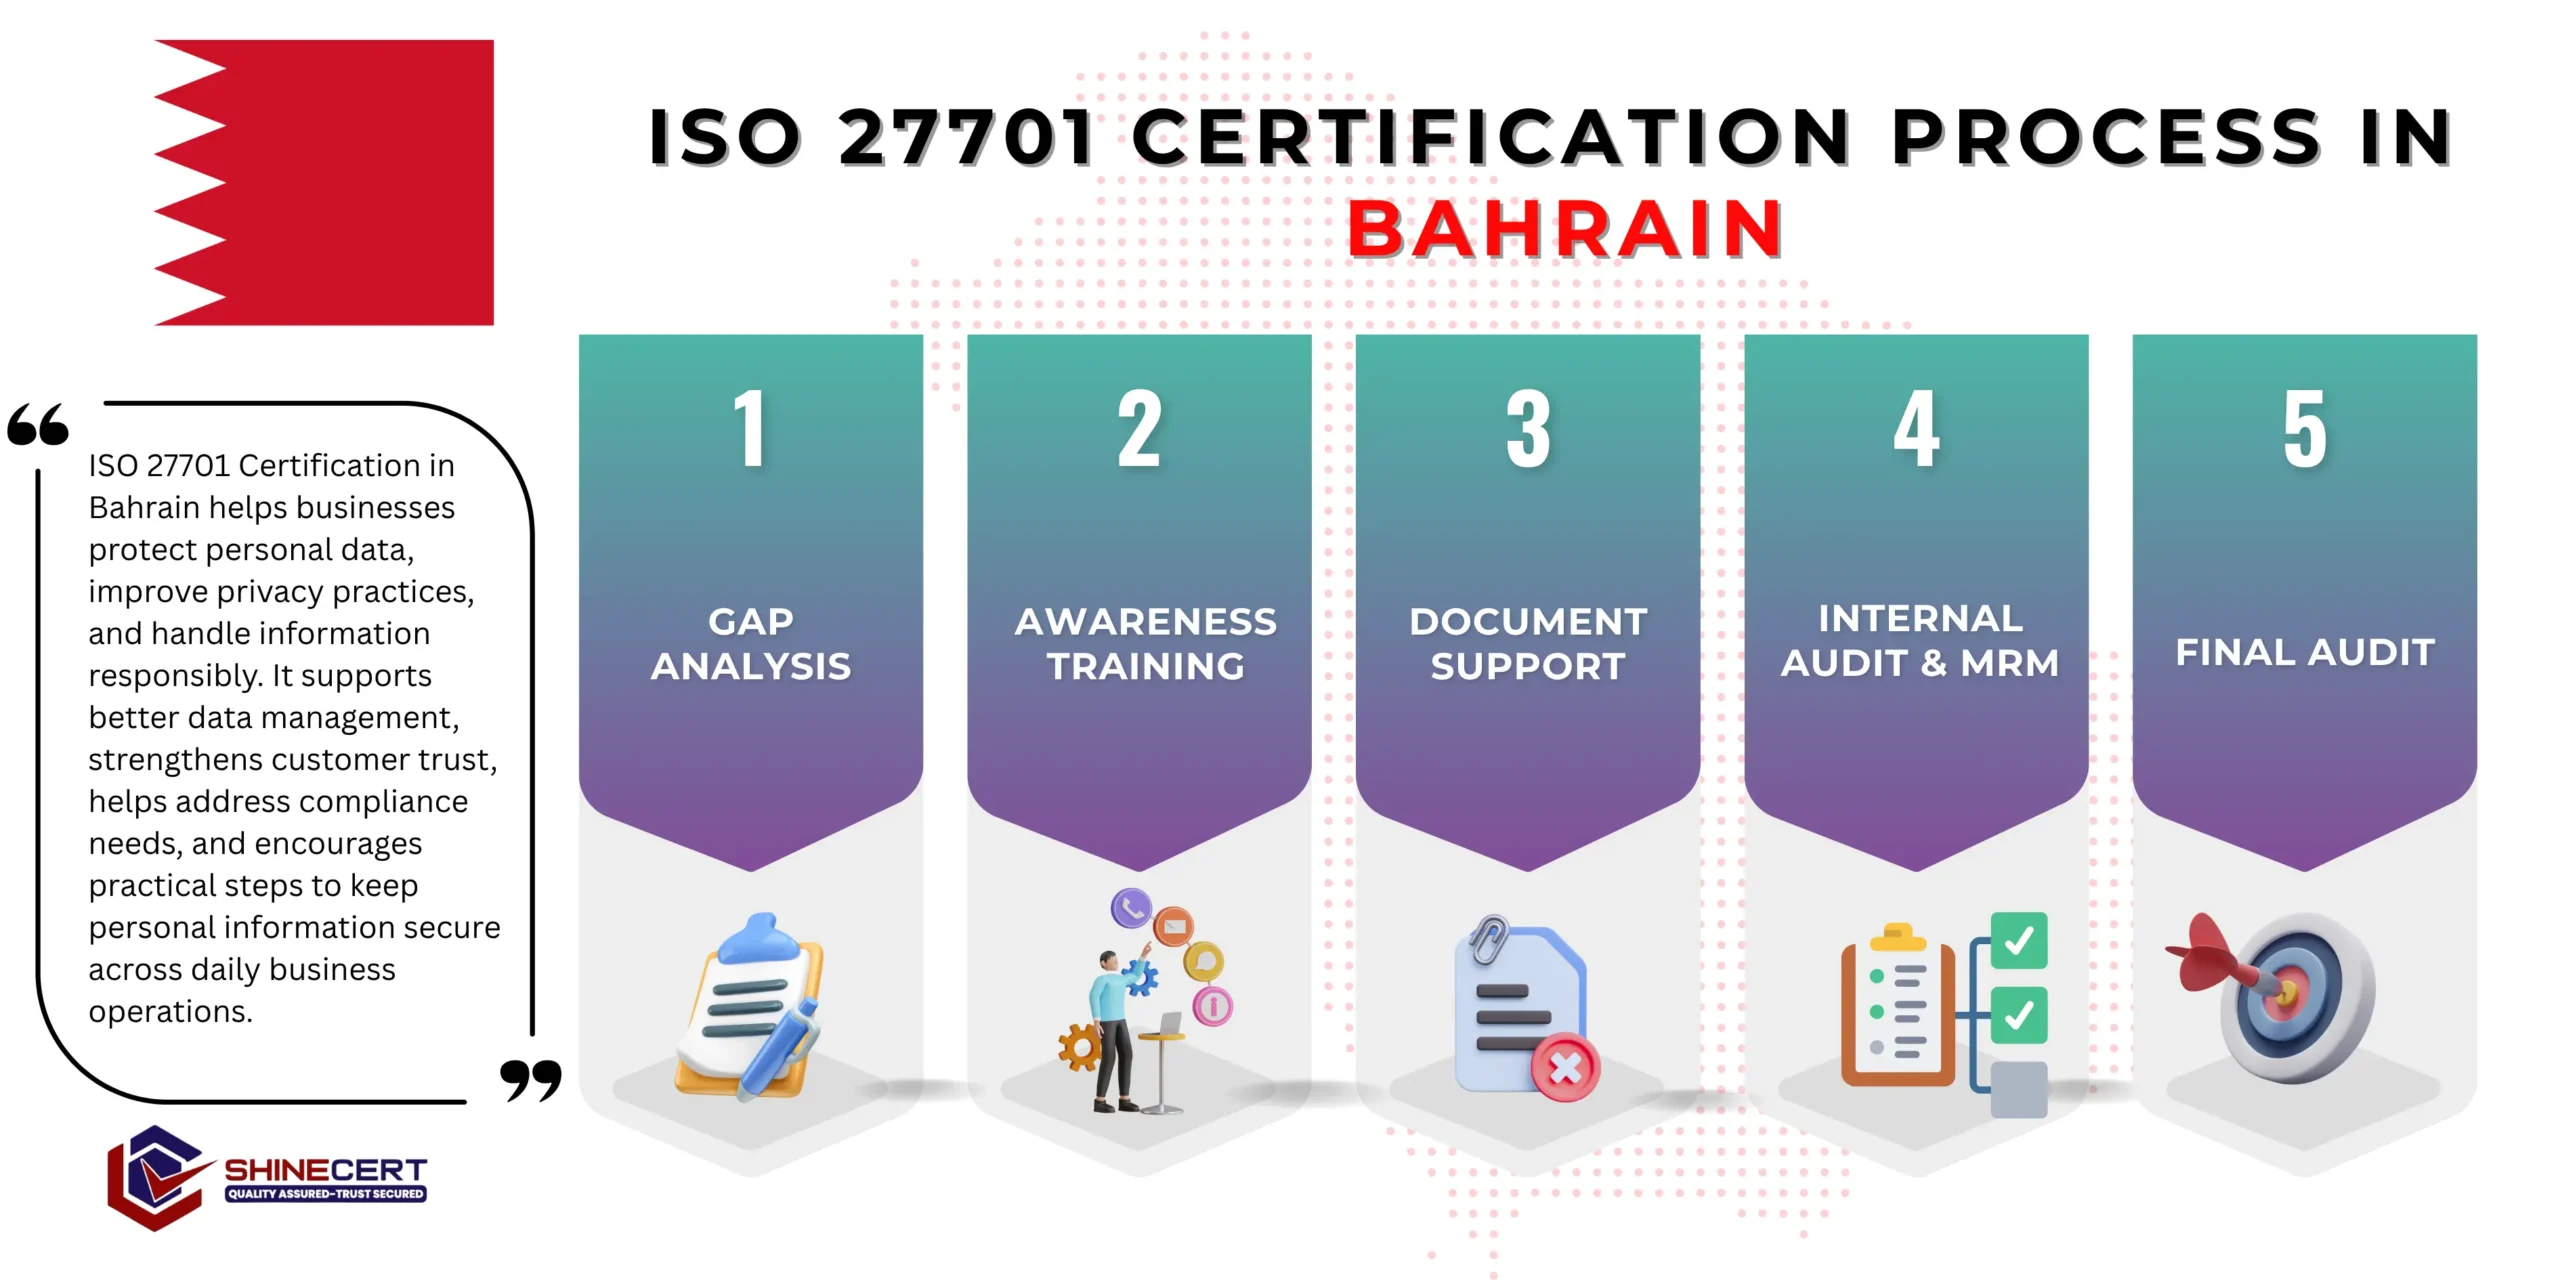
Our Five-Step Certification Process: What to Actually Expect
Gap Assessment
We evaluate your current privacy practices and existing ISO 27001 system against ISO 27701’s specific additions. What this means for you: a clear picture of exactly what needs to be added, not a redundant rebuild of work already done for ISO 27001.
A gap assessment report specific to your data processing activities.
Documentation Development
Your controller/processor role mapping, purpose and legal basis register, and consent management framework get built around your actual data flows. What this means for you: documentation that genuinely reflects how your organization actually collects, uses, and shares personal data.
A complete ISO 27701 documentation extension set.
Implementation and Training
Data subject rights request processes, consent management tools, and privacy-by-design practices roll out, with staff trained on their specific privacy responsibilities. What this means for you: your team can genuinely handle a real access or deletion request within PDPL’s expected timeframes, not scramble to figure out a process on the spot.
Training records and evidence of data subject rights processes functioning.
Internal Audit and Management Review
We test the extension internally, surfacing weaknesses before the real audit. What this means for you: privacy gaps get caught and fixed in a low-stakes setting.
Internal audit report and management review minutes.
Certification Audit
The PIMS extension audit with a GAC-accredited certification body, either alongside your ISO 27001 audit or as a follow-on. What this means for you: a single coordinated audit process where possible, minimizing disruption.
Your ISO 27701 certification extension and a surveillance audit schedule.
Why This Matters So Much in Bahrain Specifically?
- PDPL creates genuine, enforceable obligations for essentially any organization processing personal data of Bahrain residents, and the Personal Data Protection Authority’s real investigation and penalty powers mean these obligations aren’t abstract legal theory, they carry genuine enforcement risk.
- Organizations that rely solely on ISO 27001 certification, while genuinely valuable for information security, often discovered during a PDPA inquiry or audit that they lack the specific documented processes PDPL actually requires: how data subject access requests get handled, what legal basis justifies each category of data processing, and how consent is genuinely tracked and honored.
- ISO 27701’s role in Bahrain is filling exactly this gap in a structured, internationally recognized way, giving organizations a credible answer when the PDPA, or a customer’s own due-diligence questionnaire, asks specifically how personal data rights are operationalized, not just how systems are secured.
Bahrain at a Glance: What Shapes ISO 27701 Demand Here
01
Governing law
Law No. 30 of 2018 (PDPL), in force since August 1, 2019, applies to all entities collecting, processing, or storing personal data of individuals residing in Bahrain.
02
Enforcement authority
the Personal Data Protection Authority (PDPA), under the Ministry of Justice, Islamic Affairs, and Waqf, issued 10 ministerial resolutions supplementing the PDPL in March 2022 and holds genuine investigation, audit, and penalty powers.
03
The compliance gap ISO 27701 fills
ISO 27001 alone establishes a strong information security foundation, but PDPL-specific obligations, data subject rights management, consent management, cross-border transfer requirements, extend beyond ISO 27001’s scope into genuine legal and privacy-specific territory that ISO 27701 formally addresses.
04
SME funding available
Tamkeen offers training and business development grants that can offset certification-related costs for eligible companies.
What Actually Drives Your Cost?
We don’t quote a flat number, because a flat number would misrepresent how different two Bahrain organizations’ actual privacy scope can be. Here’s what genuinely drives cost :
Organizations already certified face a meaningfully smaller, faster project than those needing to build both the security foundation and privacy extension simultaneously.
Organizations handling large volumes of sensitive personal data need deeper data subject rights processes than those processing limited, low-sensitivity data.
Organizations acting as both controller and processor across different relationships need documentation covering both Annex A and Annex B controls.
More distinct categories, employees, customers, website visitors, each with different processing purposes, means more documentation depth.
Organizations with significant international data flows need deeper transfer safeguard documentation than those processing data purely domestically.
Organizations with some existing consent management or request-handling process aren’t starting from zero.
An internal privacy or legal lead who can own documentation reduces consultant hours needed.
Where your project qualifies for co-funding, your genuine out-of-pocket cost can be meaningfully lower.
A compressed timeline driven by a customer due-diligence deadline sometimes needs more concentrated consultant hours in a shorter window.
Common Pitfalls We See in Bahrain ISO 27701 Projects
- Attempting ISO 27701 without a genuine ISO 27001 foundation : Because the standard extends ISO 27001’s structure, organizations without a properly implemented security management system underneath find the privacy extension has nothing solid to attach to.
- Confusing controller and processor obligations : Companies sometimes apply controller-level data subject rights obligations to a pure processor relationship, or vice versa, missing the genuinely different legal and contractual dynamics of each role.
- Treating consent management as a one-time checkbox : Genuine consent management requires ongoing tracking of what was consented to, when, and whether it’s been withdrawn, not a single “I agree” click logged once and never revisited.
- Assuming international cloud hosting is automatically compliant : Organizations using international cloud providers sometimes assume the provider’s own certifications cover their cross-border transfer obligations, missing the need for their own documented transfer safeguard assessment.
Benefits at a Glance
01
Structured, auditable framework directly supporting PDPL compliance
02
Genuine operational processes for data subject rights requests
03
Reduced PDPA enforcement exposure
04
Access to potential Tamkeen funding support
05
Efficient extension for organizations already ISO 27001 certified
Benefits: What Certification Actually Changes
- Genuine, defensible PDPL compliance posture : Where ISO 27001 alone leaves privacy-specific obligations informally handled, ISO 27701 gives you documented, auditable processes directly addressing PDPL’s data subject rights and consent requirements.
- Reduced PDPA enforcement risk : A structured privacy management system demonstrates genuine “appropriate technical and organizational measures”, exactly the standard PDPA investigations assess against.
- Efficient path for ISO 27001-certified organizations : Because ISO 27701 extends rather than duplicates ISO 27001, organizations already certified add privacy management with meaningfully less incremental effort than building a privacy program from scratch.
- Stronger customer and partner trust : Certification gives a credible, verifiable answer to increasingly common privacy due-diligence questions from customers, partners, and international group companies.
- Access to Tamkeen-supported funding : Depending on eligibility, certification-related training and consulting costs may be partially offset through Tamkeen’s programs.
What Happens When a Bahrain Organization Relies on ISO 27001 Alone for Privacy?
- This is worth understanding concretely. ISO 27001 certification demonstrates genuine information security maturity, but it doesn’t specifically address PDPL’s data subject rights, consent management, or cross-border transfer requirements, an organization relying on ISO 27001 alone can face a PDPA inquiry or a customer due-diligence request that specifically asks about these privacy-specific obligations and find it has no structured, documented answer, despite having genuinely strong security controls.
- Organizations that discover this gap only during an actual PDPA investigation or a lost contract due to an unanswered privacy questionnaire face more pressure-filled remediation than those who proactively extend their security foundation into a genuine privacy management system.
Privacy Information Management Requirements, Clause by Clause
- PIMS-Specific Requirements Related to ISO 27001 Clauses 4-10 : ISO 27701 doesn’t introduce entirely new clause numbers, it extends each existing ISO 27001 clause with privacy-specific additions, so Clause 4 (Context) now explicitly requires identifying your role as PII controller, processor, or both; Clause 6 (Planning) extends risk assessment to cover privacy risks alongside security risks.
- Determining PII Processing Purpose and Legal Basis (extension of Clause 6) : A genuinely important addition, organizations must document the specific purpose and legal basis for each category of personal data processing, directly supporting PDPL’s requirements around lawful processing.
- Privacy by Design and by Default (extension of Clause 8) : New systems and processes need privacy considerations built in from the start, not retrofitted after deployment, a genuinely proactive rather than reactive requirement.
- Annex A: Controls for PII Controllers : Covers conditions for collection and processing, obligations to PII principals (data subjects), privacy by design, and PII sharing, transfer, and disclosure, directly mapping to PDPL’s data subject rights provisions.
- Annex B: Controls for PII Processors : Covers conditions for collection and processing on behalf of a controller, and obligations to PII principals via the controller relationship, relevant for Bahrain organizations processing data on behalf of clients.
Tamkeen Funding: Does Your ISO 27701 Project Qualify for Subsidy?
Tamkeen’s training and business development programs can apply to privacy management system implementation, depending on your company’s size, sector, and program eligibility. Given that ISO 27701 is typically a faster, more targeted project than a full management system implementation, checking Tamkeen eligibility early still helps offset training-related costs.
Applicable Standards by Industry
HR Technology and Staffing
Companies processing employee data on behalf of clients need clear controller/processor role documentation and genuine data subject rights processes.
Read moreFinancial Services and Fintech
Companies handling sensitive financial and personal data use ISO 27701 to formalize privacy obligations alongside CBB Module TC security expectations.
Read moreHealthcare Technology
Providers processing patient data need especially rigorous consent management and data subject rights processes given the sensitivity involved.
Read moreMarketing and Customer Data Platforms
Companies processing customer data for marketing purposes need clear purpose and legal basis documentation, particularly around consent.
Read moreCloud and Technology Service Providers
Companies acting as processors for multiple clients need especially clear controller/processor role mapping across their client base.
Read moreCase Study: A Bahrain HR Technology Company’s Privacy Extension
- The following is an illustrative, composite example based on the kind of project ShineCert typically runs, not a specific named client. A Bahrain-based HR technology company, already ISO 27001 certified, processed employee data on behalf of multiple corporate clients across the region. The trigger was a client due-diligence questionnaire asking specifically how the company handled data subject access requests and cross-border data transfers, questions the company’s existing ISO 27001 certification didn’t directly answer.
- The gap assessment found the company’s underlying security controls were genuinely strong, but its role as a PII processor for multiple clients had never been formally documented, and data subject rights requests, rare but real, had been handled informally on a case-by-case basis without a consistent, timed process. The bulk of implementation work went into formally mapping the company’s processor relationships with each client, building a genuine, timed process for handling data subject requests received through client relationships, and documenting the safeguards applied to the company’s use of an international cloud hosting provider. Certification was achieved within the extension’s typical shorter timeline given the existing ISO 27001 foundation, and the pattern we typically see afterward held: the newly documented processor relationships clarified several previously ambiguous contractual responsibilities with clients, reducing friction in subsequent contract renewals.
Mandatory Documents Required for Certification
Extending your ISO 27001 information security policy with genuine privacy commitments.
Documented for each category of personal data processing.
Covering why and under what legal basis each data category is processed.
Documented, with defined response timeframes aligned to PDPL.
Evidence of what consent was obtained, for what purpose, and how it can be withdrawn.
Where applicable, evidencing safeguards for international data flows.
Why ShineCert?
We coordinate Bahrain engagements from ShineCert’s Riyadh and Lebanon offices, with direct familiarity with PDPL, PDPA enforcement practice, and Tamkeen’s funding programs. Our team has guided more than 10,000 organizations through ISO certification globally, bringing the expertise of the best ISO 27701 consultant in Bahrain to every engagement, and we build every Bahrain privacy management engagement around your actual data flows, controller/processor role, and funding eligibility, not a one-size-fits-all package.
Choosing a Certification Body in Bahrain?
What to Check | Why It Matters |
Accreditation under the GAC framework | Confirms genuine, internationally recognized certification |
Experience auditing ISO 27701 as an ISO 27001 extension | Ensures the auditor genuinely understands how the two standards interconnect |
Familiarity with PDPL and PDPA enforcement practice | Helps ensure your PIMS genuinely supports broader data protection compliance |
Experience with controller/processor relationship structures | Particularly relevant for companies processing data on behalf of multiple clients |
Ready to Get Certified?
ShineCert supports Bahrain organizations from initial gap assessment through certification audit, including checking whether your project qualifies for Tamkeen funding support. Book a free consultation or contact us directly, and we’ll walk through your specific data flows and cost factors before proposing a fixed-scope plan.
Frequently Asked Questions
It’s an extension standard adding Privacy Information Management System requirements on top of an existing ISO 27001 Information Security Management System.
Yes, ISO 27701 extends ISO 27001’s structure and cannot be certified independently of an existing or simultaneous ISO 27001 implementation.
It genuinely depends on factors like whether ISO 27001 is already in place, data volume and sensitivity, and controller/processor complexity, we scope every project individually.
It provides a strong, structured foundation directly addressing PDPL’s core requirements, though organizations should still confirm specific legal advice for their particular circumstances.
Typically two to three months if ISO 27001 is already in place; longer if both need to be built simultaneously.
Potentially, Tamkeen’s training and development programs can apply to certification-related costs depending on eligibility.
A controller determines the purposes and means of processing personal data; a processor processes data on behalf of a controller under contract, without independently determining processing purposes.
Yes, it requires organizations to document and assess safeguards applied when personal data moves outside the jurisdiction.
Yes, organizations handling large volumes of sensitive personal data need deeper data subject rights processes and documentation.
We coordinate Bahrain engagements from our Riyadh and Lebanon offices, with consultants traveling on-site as needed.