
ISO 22301 Certification in Bahrain
Quick Answer
ISO 22301 is the international standard for business continuity management systems, and in Bahrain it has genuine regulatory traction, the Central Bank of Bahrain itself achieved ISO 22301:2019 certification for its own statutory and internal support functions, and its Module TC (Technology Controls) sets requirements around business continuity that map directly onto ISO 22301 implementation for licensed financial institutions. Bahrain Islamic Bank became the first bank in Bahrain to obtain business continuity certification, signaling the standard’s genuine local adoption beyond the regulator itself. Get certified through a body accredited under the Global Accreditation Cooperation (GAC) framework. Plan for three to five months from kickoff to certificate. Cost depends on genuine factors, critical process complexity, number of sites, recovery time requirements, not a flat number.
What Is ISO 22301, Technically Speaking?
ISO 22301 is the certifiable standard for business continuity management systems, following the same Harmonized Structure as ISO 9001, ISO 27001, and ISO 14001, which means organizations already running other management systems can integrate business continuity into shared governance infrastructure rather than building an isolated program. What makes ISO 22301 technically distinct is its central analytical tool: the Business Impact Analysis (BIA), required under Clause 8.2.2, which systematically identifies an organization’s critical activities and the maximum tolerable period of disruption each can withstand before causing unacceptable harm to the organization or its stakeholders.
The BIA produces two genuinely important technical metrics for each critical activity: Recovery Time Objective (RTO), how quickly the activity must be restored after disruption, and Recovery Point Objective (RPO), how much data loss, measured in time, is tolerable for activities involving data processing. These aren’t abstract numbers; they directly determine the cost and complexity of your recovery infrastructure. A payment processing function with a four-hour RTO needs meaningfully different (and more expensive) recovery infrastructure than a marketing function that can tolerate a week of disruption, and the BIA is what makes that distinction explicit and defensible rather than a guess.
Building on the BIA, Clause 8.3 requires organizations to develop business continuity strategies and solutions specifically calibrated to meet the RTOs and RPOs identified, this is where genuine technical decisions get made about backup site strategy, data replication approach, alternate staffing arrangements, and supplier continuity requirements. A critical technical distinction the standard makes clear is between business continuity plans (how the organization keeps operating or resumes critical activities) and disaster recovery plans (how specific IT systems and infrastructure get restored), the two are related but not identical, and ISO 22301 explicitly requires both dimensions to be addressed and connected.
Perhaps the standard’s most operationally significant requirement is Clause 8.5’s mandate for exercising and testing, a business continuity plan that exists only on paper and has never been tested against a realistic scenario is, in practice, an unverified assumption, not a genuine capability. The standard expects organizations to conduct exercises ranging from tabletop discussions through full-scale simulations, and to formally capture and act on lessons learned from each exercise, feeding back into plan improvement. This is precisely the gap that distinguishes organizations with a genuine continuity capability from those with an impressive-looking but untested document.
For Bahrain financial institutions specifically, CBB’s Module TC references business continuity requirements that map directly onto ISO 22301’s structure, meaning a properly built ISO 22301 system does double duty, satisfying the international standard’s certification requirements while directly supporting the specific regulatory expectations CBB already holds licensed institutions to.
What are the steps to get ISO 22301 Certification in Bahrain?
our services
- ISO Certification Bahrain
- ISO 9001 Certification Bahrain
- ISO 14001 Certification Bahrain
- ISO 27001 Certification Bahrain
- ISO 22000 Certification Bahrain
- ISO 27701 Certification Bahrain
- ISO 45001 Certification Bahrain
- ISO 20000-1 Certification Bahrain
- ISO 13485 Certification Bahrain
- ISO 17025 Certification Bahrain
- ISO 31000 Certification Bahrain
- ISO 42001 Certification Bahrain
- ISO 37001 Certification Bahrain
- ISO 22301 Certification Bahrain
- ISO 50001 Certification Bahrain
- CE Mark Certification Bahrain
- GDPR Certification Bahrain
- GMP Certification Bahrain
- Halal Certification Bahrain
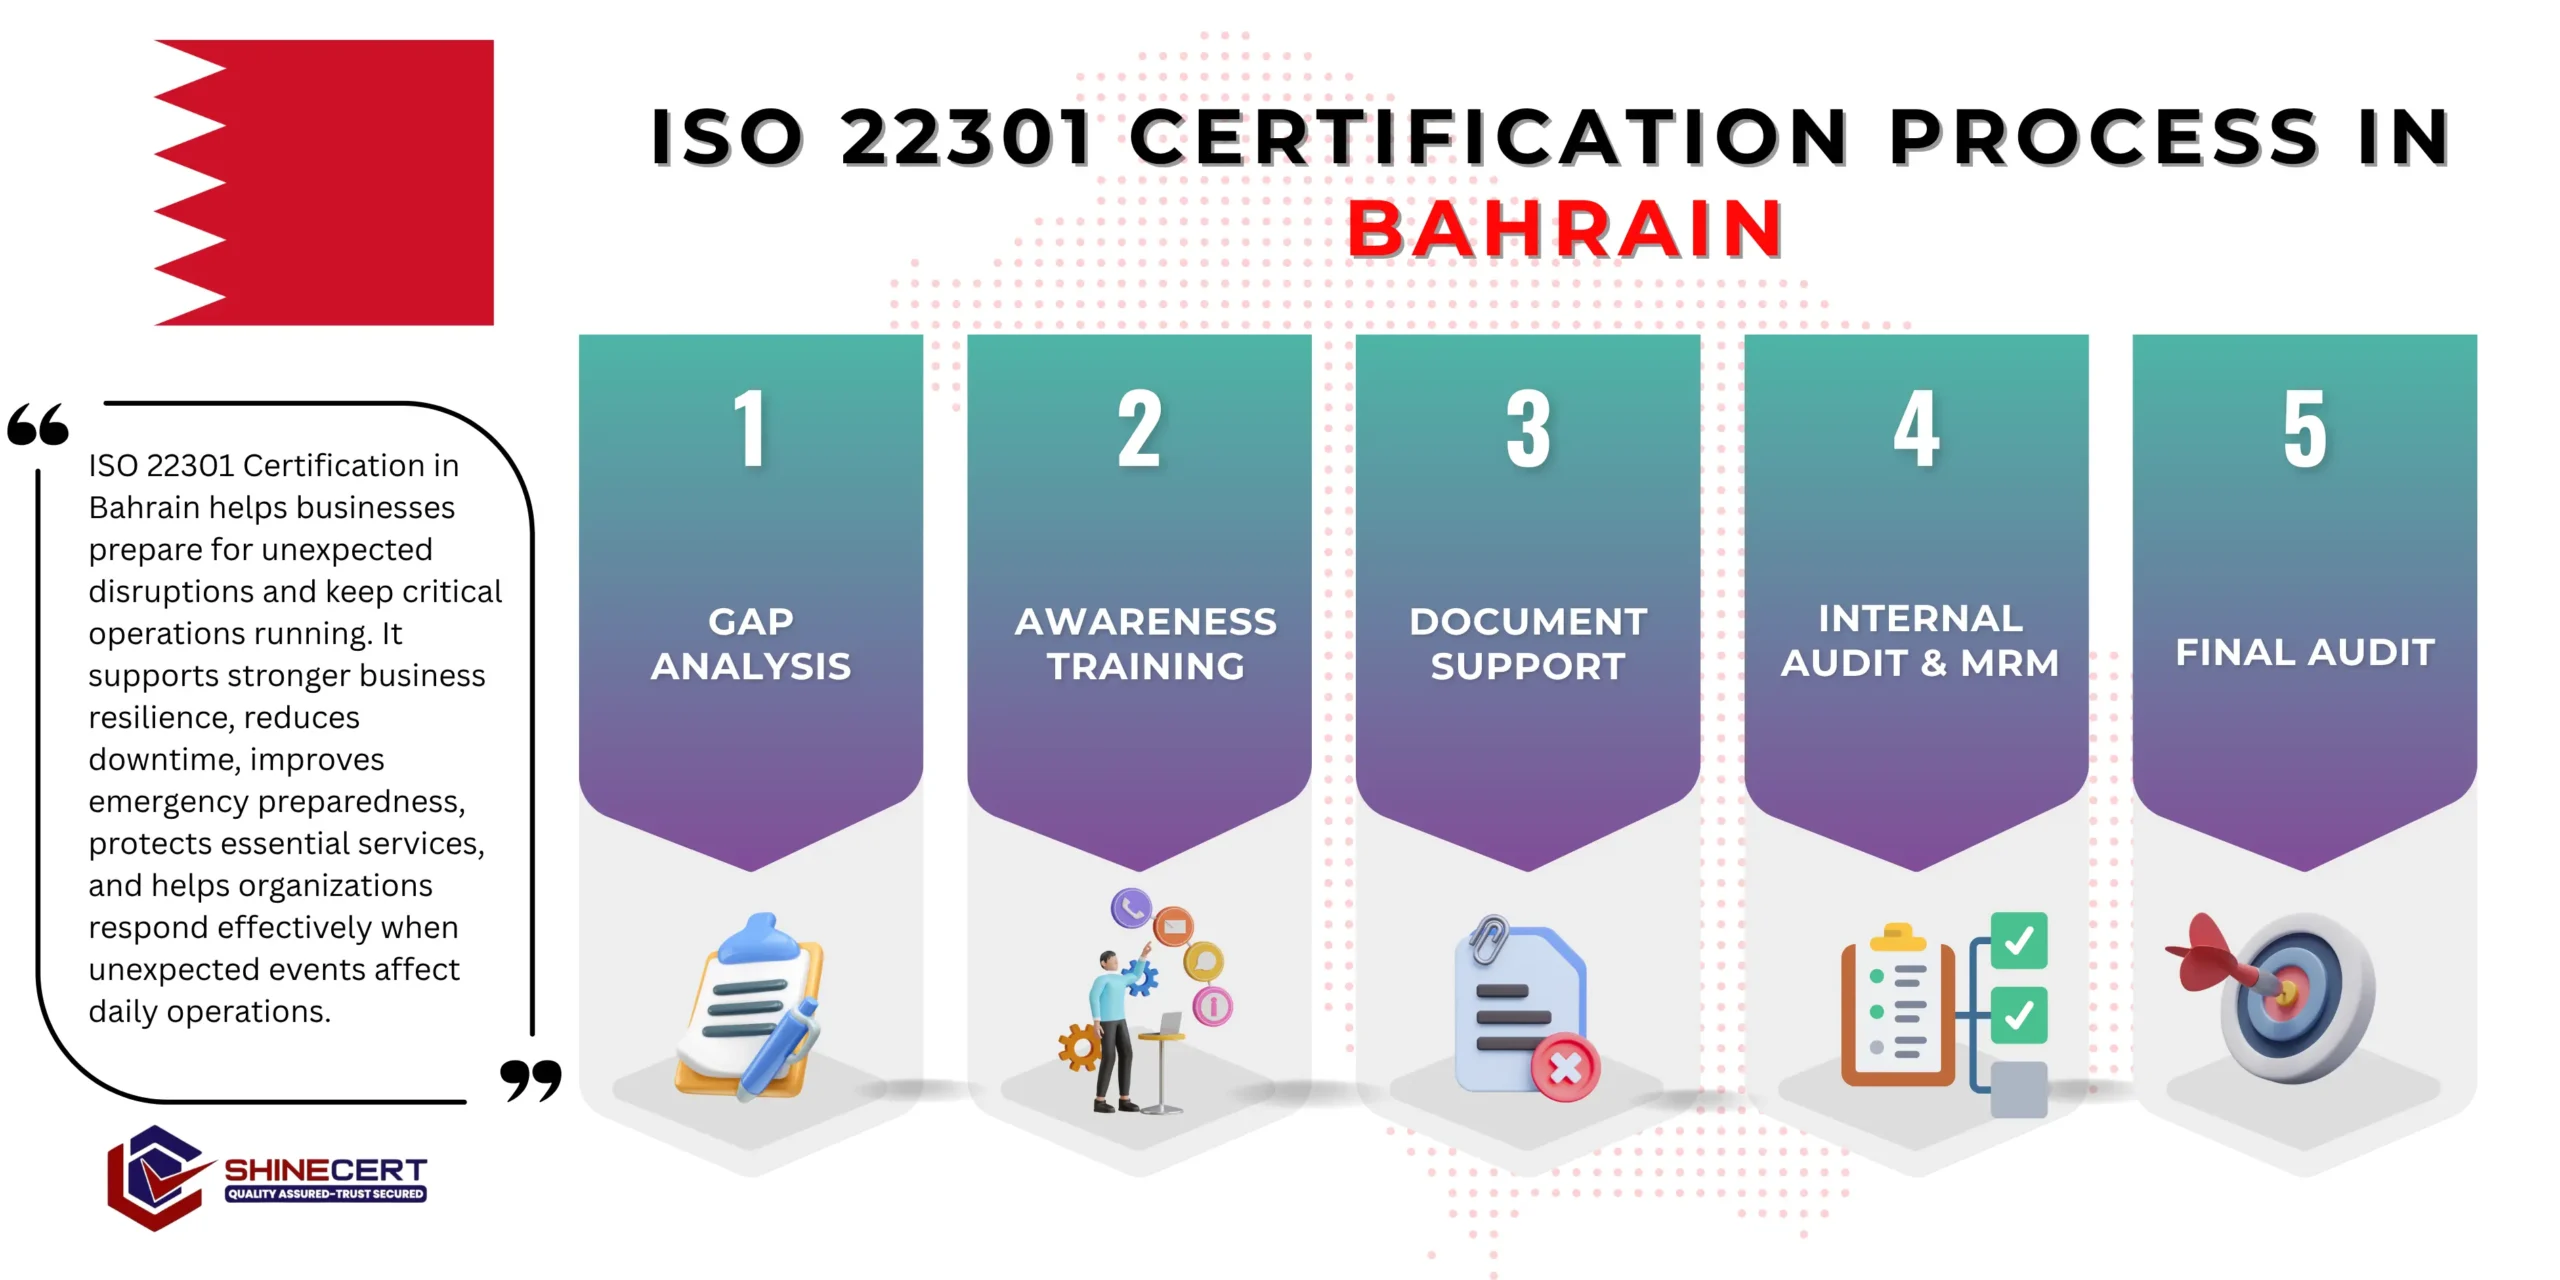
Our Five-Step Certification Process: What to Actually Expect
Gap Assessment
We evaluate your current continuity practices, including any existing CBB Module TC compliance work, against ISO 22301’s requirements. What this means for you: a clear picture of the real gap, avoiding duplicate effort against work already done for other regulatory obligations.
A gap assessment report specific to your operations and critical activities.
Business Impact Analysis and Documentation
We identify your genuinely critical activities and establish defensible RTOs and RPOs for each, then build continuity strategies calibrated to meet them. What this means for you: recovery infrastructure investment that’s proportionate to genuine business need, not over- or under-built.
A complete Business Impact Analysis and continuity strategy documentation set.
Implementation and Training
Continuity plans and recovery arrangements roll out, with staff trained on their specific roles during a disruption. What this means for you: your team knows genuinely what to do during a real incident, not just where to find a document.
Training records and documented continuity plans for each critical activity.
Exercising, Internal Audit, and Management Review
We run genuine exercises, tabletop through simulation, testing whether the plan actually works, then internally audit before the real certification audit. What this means for you: gaps between the plan on paper and genuine capability get caught and closed before they matter.
Exercise reports, internal audit report, and management review minutes.
Certification Audit
Stage 1 and Stage 2 audits with a GAC-accredited certification body. What this means for you: Stage 1 checks documentation readiness; Stage 2 verifies the system, including exercise evidence, genuinely functions.
Your ISO 22301 certificate and a surveillance audit schedule.
Why This Matters So Much in Bahrain Specifically?
- Bahrain’s position as a regional financial hub means genuine operational disruption at a licensed institution has consequences that extend well beyond the individual company, payment systems, currency stability functions, and cross-border financial flows all depend on the resilience of the institutions running them.
- The Central Bank of Bahrain’s decision to pursue its own ISO 22301 certification for exactly these functions, monetary policy, reserves and debt management, currency issuance, payment and settlement oversight, is a genuinely meaningful regulatory signal: the regulator isn’t just expecting business continuity discipline from licensed institutions, it has demonstrated the discipline in its own operations.
- Bahrain Islamic Bank’s early adoption reinforces that this isn’t a theoretical expectation confined to the regulator, it’s a genuine, achievable standard being adopted across Bahrain’s banking sector, and institutions that haven’t yet pursued it increasingly stand out by its absence rather than benefit from an unusual competitive advantage by having it.
Bahrain at a Glance: What Shapes ISO 22301 Demand Here
01
Regulatory leadership by example
the Central Bank of Bahrain holds its own ISO 22301:2019 certification, covering monetary policy functions, government reserves and debt management, currency issuance, and payment system oversight.
02
Module TC (Technology Controls)
CBB’s regulatory module sets specific requirements around information security governance, incident response, and business continuity that directly map to ISO 22301 implementation for licensed institutions.
03
Early banking sector adoption
Bahrain Islamic Bank was the first bank in the Kingdom to obtain ISO certification for business continuity management, demonstrating genuine sector-wide momentum beyond the regulator.
04
SME funding available
Tamkeen offers training and business development grants that can offset certification-related costs for eligible companies.
What Actually Drives Your Cost?
We don’t quote a flat number, because a flat number would misrepresent how different two Bahrain organizations’ actual continuity requirements can be. Here’s what genuinely drives cost :
An organization with a handful of straightforward critical functions needs meaningfully less BIA and strategy work than one with dozens of interdependent critical processes.
Activities requiring near-immediate recovery (measured in hours) need more sophisticated, expensive recovery infrastructure than those tolerating longer disruption windows, directly affecting both implementation and ongoing cost.
Each additional location generally needs its own continuity strategy and testing.
CBB-regulated institutions need deeper documentation and alignment with Module TC requirements than unregulated commercial businesses.
Organizations with some existing plans and infrastructure, even outdated ones, aren’t starting from zero. Organizations with no documented plan need more foundational work.
Full-scale simulation exercises are more resource-intensive to plan and run than tabletop discussions, though both have genuine value at different program maturity stages.
Pursuing ISO 27001 alongside ISO 22301 shares meaningful risk assessment and incident response infrastructure.
An internal business continuity coordinator who can own documentation and exercise planning reduces consultant hours needed.
Where your project qualifies for co-funding, your genuine out-of-pocket cost can be meaningfully lower.
A compressed timeline driven by a regulatory review deadline sometimes needs more concentrated consultant hours in a shorter window.
Common Pitfalls We See in Bahrain ISO 22301 Projects
- Writing a plan and never testing it : This is the single most common and most dangerous gap, a plan’s real value only becomes clear when it’s genuinely exercised, and organizations that skip this step carry an untested assumption, not a real capability.
- Setting RTOs and RPOs that don’t reflect genuine business need : Overly conservative RTOs waste money on unnecessary infrastructure; overly relaxed RTOs leave the organization genuinely exposed, both stem from a BIA that wasn’t rigorously conducted.
- Confusing business continuity plans with disaster recovery plans : Treating IT system recovery as the entirety of business continuity misses the broader organizational, staffing, and supplier dimensions the standard explicitly requires.
- Letting plans go stale after organizational change : Plans referencing outdated contact details, departed staff, or discontinued systems fail exactly when needed most, genuine currency requires regular review tied to organizational change, not just an annual calendar date.
Benefits at a Glance
01
Direct alignment with CBB Module TC business continuity expectations
02
Genuinely tested recovery capability, not an unverified document
03
Access to potential Tamkeen funding support
04
Reduced risk of biased, unexplainable, or drift-affected AI outcomes
05
A foundation that shares infrastructure with ISO 27001 and ISO 27701
Benefits: What Certification Actually Changes
- Genuinely tested, not just documented, resilience : The mandatory exercising and testing program means certified organizations have actually rehearsed disruption scenarios, not just written a plan that’s never been stress-tested.
- Direct regulatory alignment for CBB-licensed institutions : ISO 22301’s structure maps closely onto Module TC’s business continuity expectations, reducing the gap between certification and regulatory compliance work.
- Reduced financial and reputational impact from real disruptions : Organizations with genuinely tested RTOs and RPOs recover measurably faster and more predictably from actual incidents than those relying on improvised responses.
- Stronger counterparty and customer confidence : Certification is increasingly a genuine differentiator in due diligence from correspondent banks, large corporate clients, and regulators reviewing institutional resilience.
- Access to Tamkeen-supported funding : Depending on eligibility, certification-related training and consulting costs may be partially offset through Tamkeen’s programs.
What Happens When a Bahrain Institution Operates Without a Genuinely Tested Plan?
- This is worth understanding concretely. An untested business continuity plan creates a dangerous illusion of preparedness, the document exists, so leadership assumes the organization is covered, right up until an actual disruption reveals the gap between documented assumption and genuine capability. For CBB-regulated institutions, this gap is exactly what Module TC compliance reviews are designed to surface, and remediation under regulatory pressure, following an actual finding, tends to be more costly and reputationally damaging than proactive, planned testing.
- We generally recommend Bahrain financial institutions and critical service providers treat genuine exercising and testing as the actual point of ISO 22301, not a formality en route to a certificate, the certificate matters less than knowing, with real evidence, that your organization can genuinely recover when it needs to.
Business Continuity Requirements, Clause by Clause
- Context of the Organization (Clause 4) : Mapping your genuine operating environment, critical activities, and the interested parties, customers, regulators, counterparties, with a stake in your continuity capability.
- Leadership (Clause 5) : Top management accountability for business continuity, including genuine resourcing and priority, not delegation to a single business continuity coordinator disconnected from real operational decisions.
- Planning (Clause 6) : Risk-based planning specific to your genuine continuity risks, informed directly by the Business Impact Analysis.
- Support (Clause 7) : Competence and awareness requirements ensuring staff genuinely understand their role during a disruption, tested through their actual knowledge of continuity procedures, not just training attendance records.
- Operation (Clause 8) : The largest and most technical clause, Business Impact Analysis, risk assessment, business continuity strategies and solutions, and the exercising and testing program that proves the plan genuinely works.
- Performance Evaluation (Clause 9) : Monitoring, measurement, and internal audit test whether continuity capability is genuinely maintained and improving, not degrading as the organization changes.
- Improvement (Clause 10) : Structured handling of continuity nonconformities, including genuine lessons-learned integration after every exercise and real incident.
Tamkeen Funding: Does Your ISO 22301 Project Qualify for Subsidy?
Tamkeen’s training and business development programs can apply to business continuity management system implementation, depending on your company’s size, sector, and program eligibility. We generally recommend checking your Tamkeen eligibility before finalizing your certification budget.
Applicable Standards by Industry
Banking and Financial Services
CBB-licensed institutions use ISO 22301 to directly support Module TC compliance and demonstrate genuine operational resilience.
Read moreInsurance
Insurers use business continuity management to protect policy administration and claims processing functions critical to policyholders.
Read moreTelecommunications
Companies operating critical communications infrastructure use ISO 22301 to demonstrate resilience expected by both regulators and enterprise customers.
Read moreGovernment-Adjacent and Utility Services
Organizations delivering essential services use structured continuity management given the broad public impact of disruption.
Read moreLogistics and Supply Chain
Companies managing critical import and distribution functions use ISO 22301 to protect against genuine supply chain disruption risk.
Read moreCase Study: A Bahrain Financial Institution’s Continuity Program Buildout
- The following is an illustrative, composite example based on the kind of project ShineCert typically runs, not a specific named client. A Bahrain-based licensed financial institution had a written business continuity plan produced several years earlier that had never been genuinely exercised, and key contact details and recovery procedures within it were significantly out of date. The trigger was a CBB Module TC compliance review that specifically flagged the absence of recent testing evidence.
- The gap assessment found the plan’s underlying strategy, a backup data center and alternate staffing arrangement, was reasonably sound in concept, but nobody could confirm it would genuinely work because it had never been tested, and several key personnel referenced in the plan had since left the organization. The bulk of implementation work went into rebuilding the Business Impact Analysis with current, defensible RTOs and RPOs, updating the continuity strategies to reflect the organization’s current structure, and running a genuine tabletop exercise followed by a partial simulation of the backup data center failover. The simulation revealed a previously unknown gap: the backup data center’s failover process took nearly three times longer than the documented RTO assumed. Certification was achieved after remediating this gap, and the pattern we typically see afterward held: the discovered failover gap, caught during a controlled exercise, would have caused a genuine, costly service disruption had it first been discovered during an actual crisis.
Mandatory Documents Required for Certification
Genuine leadership commitment specific to your organization.
Documented, defining exactly which activities and sites are covered.
Identifying critical activities, RTOs, and RPOs specific to your operations.
Covering threats to your critical activities.
Calibrated to genuinely meet identified RTOs and RPOs.
Evidence that plans have been genuinely tested, not just written.
Why ShineCert?
We coordinate Bahrain engagements from ShineCert, the best ISO 22301 consultant in Bahrain, Riyadh and Lebanon offices, with direct familiarity with CBB Module TC requirements and Tamkeen’s funding programs. Our team has guided more than 10,000 organizations through ISO certification globally, and we build every Bahrain business continuity engagement around your actual critical activities, recovery requirements, and funding eligibility, not a one-size-fits-all package, with genuine emphasis on testing that proves your capability rather than paperwork that merely claims it.
Choosing a Certification Body in Bahrain?
What to Check | Why It Matters |
Accreditation under the GAC framework | Confirms genuine, internationally recognized certification |
Experience with CBB-regulated financial institutions | Ensures the auditor understands Module TC’s specific business continuity expectations |
Genuine expertise in exercise design and evaluation | Ensures your testing program produces real, defensible evidence, not a superficial checkbox exercise |
Sector-specific continuity audit experience | Banking, telecommunications, and logistics each involve meaningfully different continuity risk profiles |
Ready to Get Certified?
ShineCert supports Bahrain organizations from initial gap assessment through certification audit, including checking whether your project qualifies for Tamkeen funding support. Book a free consultation or contact us directly, and we’ll walk through your specific critical activities and cost factors before proposing a fixed-scope plan.
Frequently Asked Questions
It’s the international standard for business continuity management systems, setting requirements for identifying critical activities and building genuinely tested capability to maintain or recover them during disruption.
It genuinely depends on factors like the number and complexity of critical activities, recovery time requirements, and existing continuity maturity, we scope every project individually.
Not as a blanket mandate by name, but Module TC’s business continuity requirements map directly onto ISO 22301 implementation for licensed institutions.
Typically three to five months.
Potentially, Tamkeen’s training and development programs can apply to certification-related costs depending on eligibility.
Business continuity covers how the whole organization keeps operating or resumes critical activities; disaster recovery specifically covers restoring IT systems and infrastructure; ISO 22301 requires both to be addressed and connected.
Testing is mandatory under Clause 8.5, an untested plan is an unverified assumption, not a genuine capability, and auditors specifically look for exercise evidence.
Yes, the Central Bank of Bahrain itself holds ISO 22301:2019 certification, and Bahrain Islamic Bank was the first bank in the Kingdom to achieve it.
Yes, each critical activity generally needs its own Business Impact Analysis, RTO/RPO determination, and continuity strategy.
We coordinate Bahrain engagements from our Riyadh and Lebanon offices, with consultants traveling on-site as needed.