
ISO 27001 Certification in Bahrain
Quick Answer
ISO 27001 is the international standard for information security management systems, and in Bahrain it sits at the intersection of two genuine regulatory pressures: the Personal Data Protection Law (Law No. 30 of 2018, in force since August 2019), overseen by the Personal Data Protection Authority under the Ministry of Justice, Islamic Affairs, and Waqf; and, for licensed financial institutions, the Central Bank of Bahrain’s Module TC (Technology Controls), which sets specific requirements around information security governance, incident response, and business continuity. ISO 27001 doesn’t automatically satisfy either framework on its own, but it provides a strong foundation for both. Get certified through a body accredited under the Global Accreditation Cooperation (GAC) framework. Plan for three to five months from kickoff to certificate. Cost depends on genuine factors, data sensitivity, number of systems, regulatory exposure, not a flat number.
What Is ISO 27001, Technically Speaking?
ISO 27001 is the certifiable standard within the ISO 27000 family of information security standards, which also includes ISO 27002 (a detailed reference for implementing the Annex A controls), ISO 27701 (a privacy-specific extension), and several sector-specific extensions. ISO 27001 itself, like ISO 9001 and ISO 14001, follows the Harmonized Structure, and its most recent major revision, ISO 27001:2022, restructured its Annex A controls from the previous 114 controls across 14 domains down to 93 controls organized into four themes: organizational, people, physical, and technological.
The technical core of ISO 27001 is the risk assessment and Statement of Applicability (SoA) process. Clause 6.1.2 requires organizations to establish and apply an information security risk assessment process, identifying risks to the confidentiality, integrity, and availability of information assets. Critically, Annex A’s 93 controls aren’t all mandatory for every organization, Clause 6.1.3 requires producing a Statement of Applicability that documents which controls are actually applied, and which are formally excluded with justification, based on the organization’s genuine risk assessment. This is a frequently misunderstood point: an auditor doesn’t expect every organization to implement all 93 controls identically; they expect the SoA to reflect a genuine, defensible risk-based decision about which controls matter for this specific organization’s specific risk profile.
Among the 2022 revision’s newer control themes, several carry particular relevance for Bahrain’s financial and technology sectors: threat intelligence (a new control requiring organizations to actively gather and use information about emerging threats, not just react to past incidents), cloud services security (addressing the shared-responsibility reality of cloud infrastructure, relevant given the growth of Bahrain’s fintech and cloud-hosting sector), and data masking (formalizing techniques to protect sensitive data during testing, development, or analytics use). These additions reflect how much the information security threat landscape shifted between the 2013 and 2022 revisions.
ISO 27001 also formally requires an Information Security Continuity plan (Control 5.30/A.17 in the older numbering), meaning the standard genuinely overlaps with business continuity management, which is exactly why organizations pursuing both ISO 27001 and ISO 22301 find significant shared infrastructure between the two, particularly relevant for CBB-regulated Bahrain financial institutions where Module TC references both concepts together.
Importantly for Bahrain organizations: ISO 27001 certification demonstrates a functioning information security management system, but it is not automatically equivalent to PDPL compliance. PDPL governs how personal data specifically is collected, processed, and protected, including data subject rights, consent management, and cross-border transfer requirements, areas that extend beyond ISO 27001’s information security scope into genuine legal and privacy-specific territory. Organizations serious about full PDPL compliance typically pursue ISO 27001 as a strong technical foundation, then layer PDPL-specific legal and consent-management controls on top, an approach ISO 27701 (covered on its own Bahrain page) formalizes directly.
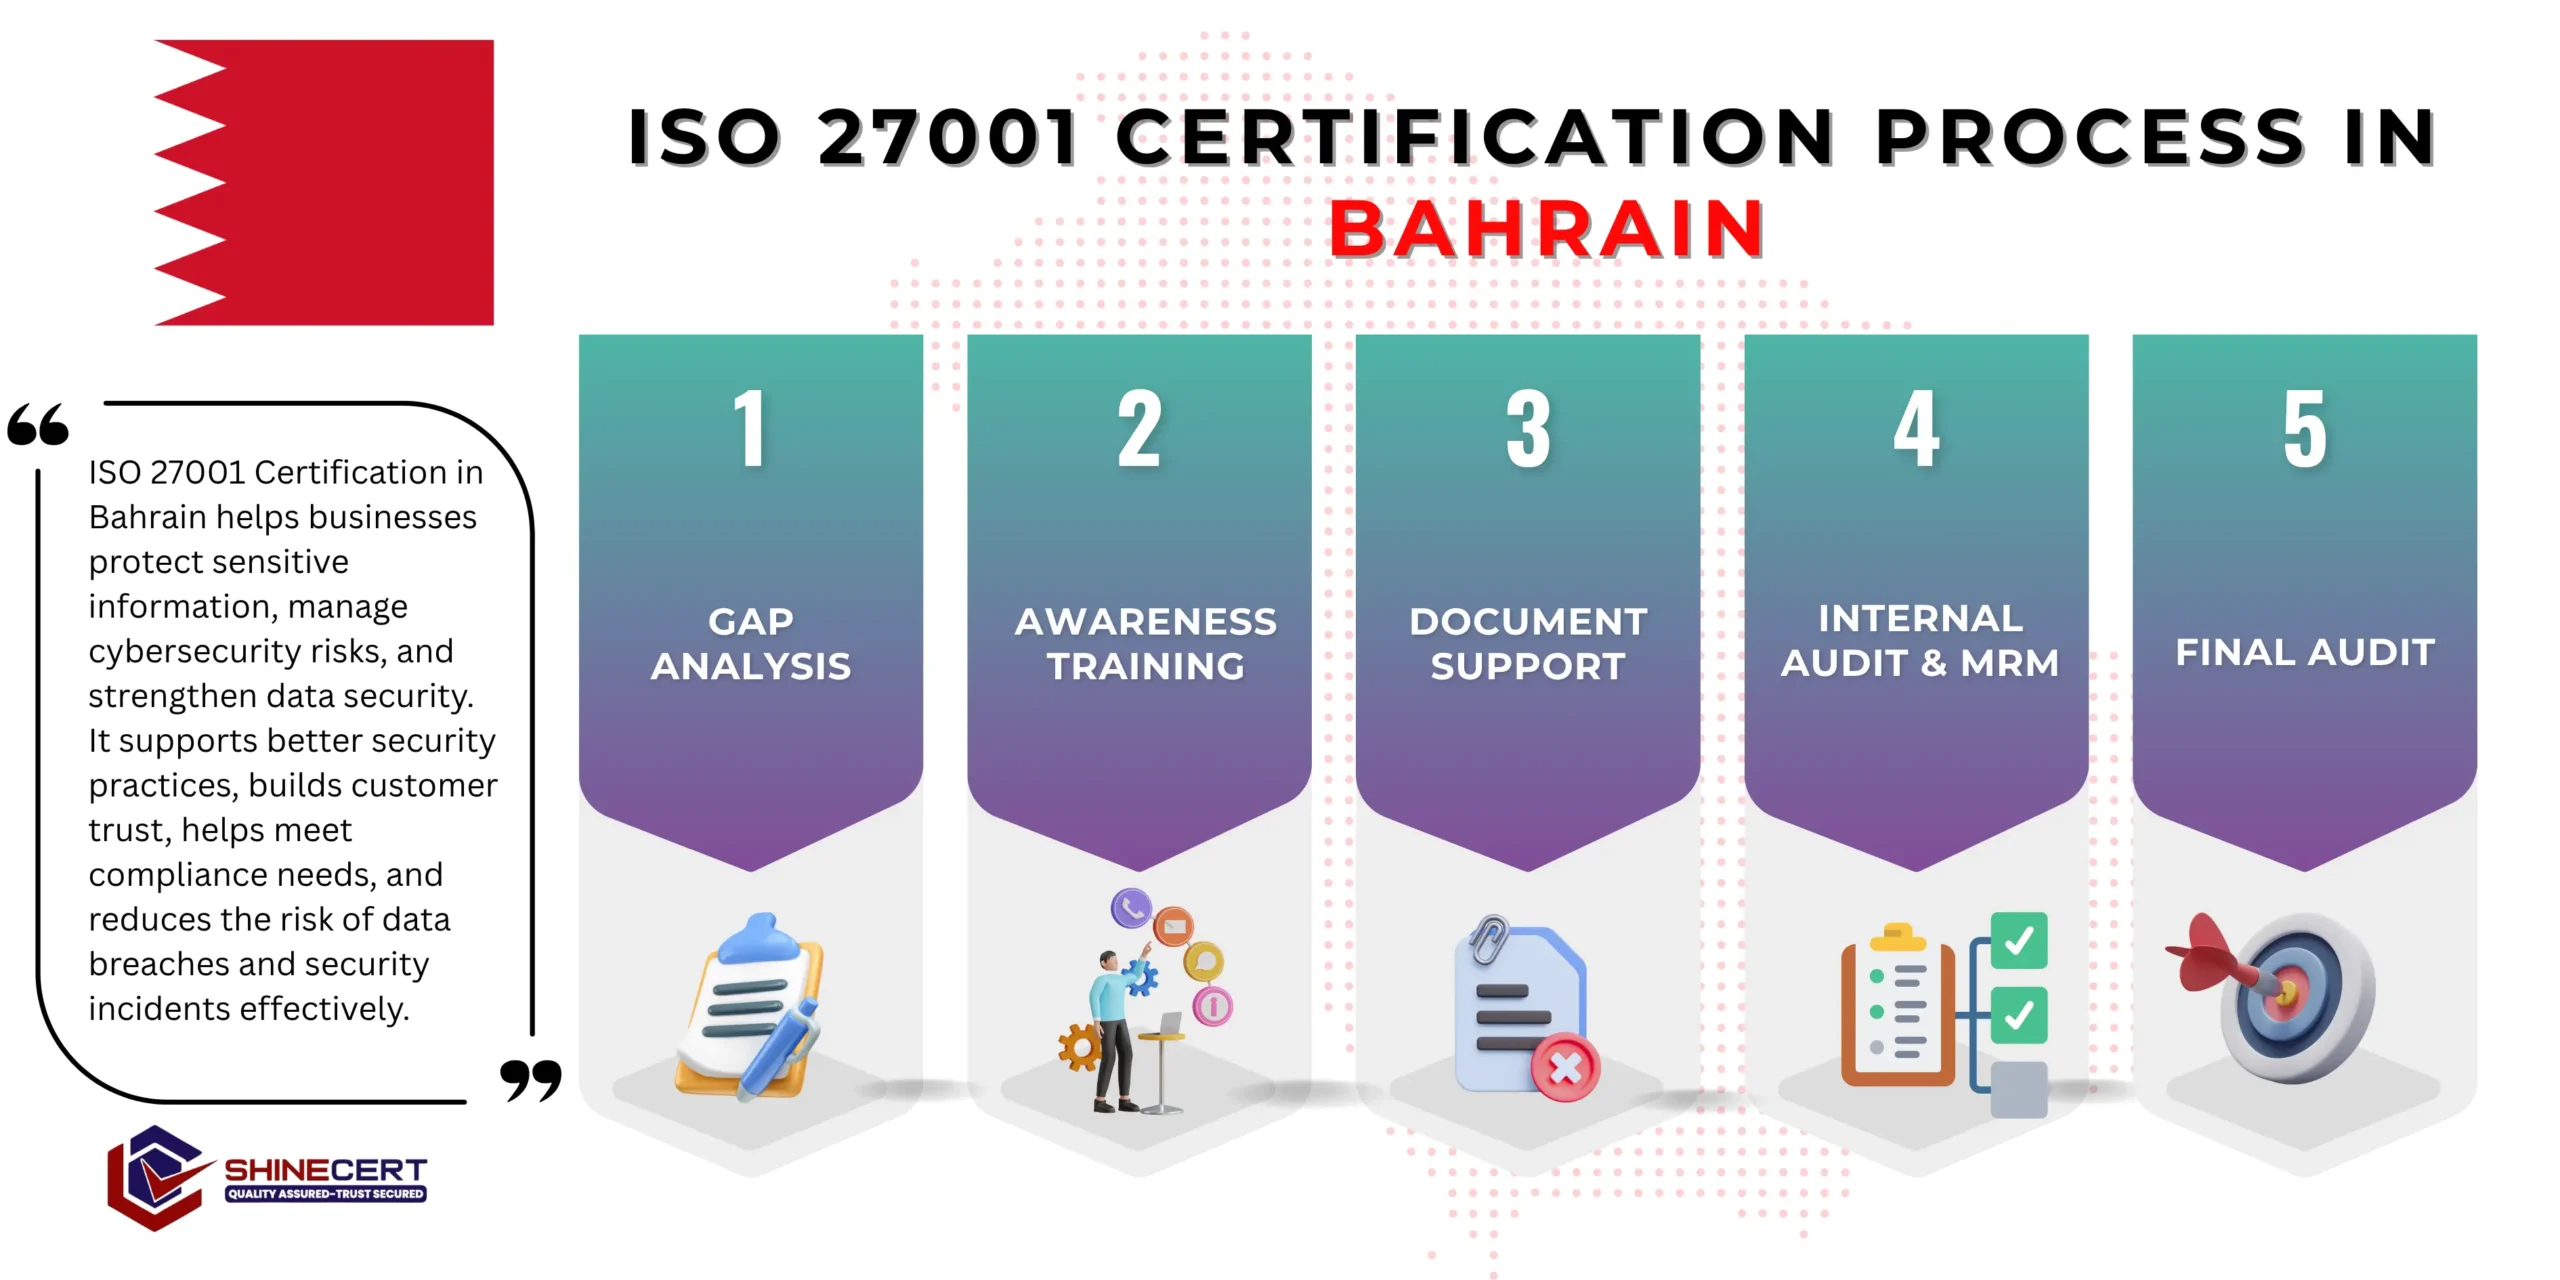
What are the steps to get ISO 27001 Certification in Bahrain?
our services
- ISO Certification Bahrain
- ISO 9001 Certification Bahrain
- ISO 14001 Certification Bahrain
- ISO 27001 Certification Bahrain
- ISO 22000 Certification Bahrain
- ISO 27701 Certification Bahrain
- ISO 45001 Certification Bahrain
- ISO 20000-1 Certification Bahrain
- ISO 13485 Certification Bahrain
- ISO 17025 Certification Bahrain
- ISO 31000 Certification Bahrain
- ISO 42001 Certification Bahrain
- ISO 37001 Certification Bahrain
- ISO 22301 Certification Bahrain
- ISO 50001 Certification Bahrain
- CE Mark Certification Bahrain
- GDPR Certification Bahrain
- GMP Certification Bahrain
- Halal Certification Bahrain
Our Five-Step Certification Process: What to Actually Expect
Gap Assessment
We evaluate your current security posture, including any existing PDPL or CBB Module TC compliance work, against ISO 27001’s requirements. What this means for you: a clear picture of what genuinely needs to change, avoiding duplicate effort against work you’ve already done for other compliance obligations.
A gap assessment report specific to your systems and data environment.
Documentation Development
Your risk assessment methodology, risk register, Statement of Applicability, and supporting policies get built around your actual technology environment. What this means for you: a Statement of Applicability that genuinely reflects your risk profile, not a copy-pasted list of all 93 controls marked “applicable” by default.
A complete ISO 27001 documentation set.
Implementation and Training
Selected controls roll out across your systems, with staff trained on security awareness and their specific responsibilities. What this means for you: this phase often takes longest for technical controls requiring genuine system or process changes, not just policy writing.
Training records and evidence of controls functioning in daily operations.
Internal Audit and Management Review
We test the system internally, surfacing weaknesses before the real audit. What this means for you: control gaps get caught and fixed in a low-stakes setting.
Internal audit report and management review minutes.
Certification Audit
Stage 1 and Stage 2 audits with a GAC-accredited certification body. What this means for you: Stage 1 checks documentation and SoA readiness; Stage 2 verifies controls genuinely function.
Your ISO 27001 certificate and a surveillance audit schedule.
Why This Matters So Much in Bahrain Specifically?
- Bahrain has positioned itself as a regional financial and fintech hub, and that positioning creates genuine, concrete information security expectations. Licensed financial institutions operate under the Central Bank of Bahrain’s regulatory framework, where Module TC’s technology-controls requirements around information security governance, incident response, and business continuity map directly onto ISO 27001 implementation, meaning certification isn’t an abstract international credential for these companies, it’s a practical accelerator toward regulatory compliance they already need to demonstrate.
- Beyond financial services, the PDPL creates a genuine, enforceable obligation for essentially any Bahrain-based or Bahrain-serving business handling personal data, with the Personal Data Protection Authority holding real investigation, audit, and penalty powers. Companies that treat data protection as a legal afterthought rather than a structured technical and organizational discipline face genuine enforcement exposure, and ISO 27001 gives them a recognized, auditable framework for demonstrating the “appropriate technical and organizational measures” that data protection laws worldwide, PDPL included, typically require.
Bahrain at a Glance: What Shapes ISO 27001 Demand Here
01
Data protection law
Law No. 30 of 2018 (PDPL), in force since August 1, 2019, applies to all entities collecting, processing, or storing personal data of individuals residing in Bahrain, overseen by the Personal Data Protection Authority (PDPA).
02
Financial sector overlay
the Central Bank of Bahrain’s Module TC sets specific technology-control requirements for licensed financial institutions, directly mapping to ISO 27001 and ISO 22301 implementation.
03
Telecom sector regulator
the Telecommunications Regulatory Authority (TRA), established in 2002, regulates cybersecurity readiness across Bahrain’s telecom infrastructure.
04
SME funding available
Tamkeen offers training and business development grants that can offset certification-related costs for eligible companies.
What Actually Drives Your Cost?
We don’t quote a flat number, because a flat number would misrepresent how different two Bahrain companies’ actual information security scope can be. Here’s what genuinely drives cost :
A company processing sensitive financial or health data needs meaningfully deeper controls than one handling low-sensitivity operational data.
Every system holding or processing information within your defined scope needs its own risk assessment and applicable controls.
Physical security controls need to be assessed separately for each site or hosting location.
Companies also subject to CBB Module TC or other sector-specific requirements need additional mapping work beyond ISO 27001 alone.
Companies with existing encryption, access control, and monitoring aren’t starting from zero. Companies with informal, undocumented security practices need more foundational work.
Each vendor relationship touching your data needs its own risk consideration under Annex A’s supplier relationship controls.
Pursuing ISO 27701 or ISO 22301 alongside ISO 27001 shares meaningful implementation and audit infrastructure.
An internal security or IT lead who can own technical implementation reduces consultant hours needed.
Where your project qualifies for co-funding, your genuine out-of-pocket cost can be meaningfully lower.
A compressed timeline driven by a partnership or contract deadline sometimes needs more concentrated consultant hours in a shorter window.
Common Pitfalls We See in Bahrain ISO 27001 Projects
- Marking every Annex A control “applicable” without genuine justification : A Statement of Applicability that doesn’t reflect a real, defensible risk assessment doesn’t hold up under audit scrutiny and doesn’t actually help manage risk.
- Assuming ISO 27001 certification automatically means PDPL compliance : The two frameworks overlap substantially but aren’t identical, PDPL-specific requirements like consent management and data subject rights need dedicated attention beyond ISO 27001’s scope.
- Building technical controls without documenting the risk assessment behind them : Strong technical security that isn’t formally risk-assessed and documented doesn’t satisfy the audit trail auditors, or PDPA investigators, actually need to see.
- Treating incident response plans as untested documents : A plan that’s never been walked through in a tabletop exercise often fails in exactly the ways a real incident would expose.
Benefits at a Glance
01
Strong technical foundation supporting PDPL compliance
02
Direct alignment with CBB Module TC for regulated financial institutions
03
Reduced likelihood and impact of data breaches
04
Access to potential Tamkeen funding support
05
A foundation that transfers cleanly into ISO 27701 or ISO 22301 later
Benefits: What Certification Actually Changes
- Stronger PDPL compliance posture : While not automatically equivalent, ISO 27001’s technical and organizational measures directly support the “appropriate security measures” language common to data protection law, reducing genuine enforcement exposure.
- Faster path to CBB Module TC alignment : For licensed financial institutions, ISO 27001’s structured approach to information security governance, incident response, and business continuity maps directly onto Module TC expectations.
- Reduced breach likelihood and impact : A functioning risk assessment and control implementation process genuinely reduces both the probability of a security incident and how badly it plays out when one occurs.
- Stronger customer and partner trust : Certification is increasingly a genuine differentiator in vendor selection, particularly for companies serving financial services, government, or international clients with their own security due-diligence requirements.
- Access to Tamkeen-supported funding : Depending on eligibility, certification-related training and consulting costs may be partially offset through Tamkeen’s programs.
What Happens When a Bahrain Company Operates Without Certification in a Security-Sensitive Sector?
- This is worth understanding concretely. When a financial institution, government body, or security-conscious enterprise customer requires ISO 27001 as part of vendor due diligence, an uncertified Bahrain company isn’t always disqualified outright, but it typically faces a slower, more manual security questionnaire and audit process that a certified competitor bypasses entirely, and in competitive vendor selection, that friction and delay can be the deciding factor.
- Beyond commercial impact, operating without a structured information security management system genuinely increases breach risk and, if a breach involving personal data occurs, increases PDPA enforcement exposure given the absence of demonstrable “appropriate technical and organizational measures.” Companies that discover this only after a breach or a lost partnership opportunity often end up building security infrastructure under real pressure, rather than having it in place proactively.
Information Security Requirements, Clause by Clause
- Context of the Organization (Clause 4) : Mapping your genuine information security context, what data you hold, which systems matter, and which interested parties (PDPA, CBB if regulated, customers, partners) have security expectations of you.
- Leadership (Clause 5) : Top management accountability for information security, auditors look for evidence that security gets genuine attention and resourcing at the leadership level, not just delegation to IT.
- Planning (Clause 6) : The risk assessment and Statement of Applicability process, the technical heart of the entire system, determines which of the 93 Annex A controls genuinely apply to your organization.
- Support (Clause 7) : Competence, awareness, and communication, security awareness training that’s genuinely effective, tested through staff understanding of phishing, data handling, and incident reporting.
- Operation (Clause 8) : Operational planning and control, including the actual implementation of your selected Annex A controls across access management, encryption, secure development, and vendor management.
- Performance Evaluation (Clause 9) : Monitoring, measurement, and internal audit test whether controls are genuinely operating effectively, not just documented.
- Improvement (Clause 10) : Structured handling of security incidents and nonconformities, feeding lessons learned back into the risk assessment.
Tamkeen Funding: Does Your ISO 27001 Project Qualify for Subsidy?
Tamkeen’s training and business development programs can apply to information security management system implementation, depending on your company’s size, sector, and program eligibility. We generally recommend checking your Tamkeen eligibility before finalizing your certification budget, since co-funded training support can meaningfully reduce your effective cost.
Applicable Standards by Industry
Financial Services and Fintech
Licensed institutions and fintech companies find ISO 27001 directly supports CBB Module TC alignment and partner due-diligence requirements.
Read moreTechnology and Software
Companies building or hosting software products use ISO 27001 to demonstrate security maturity to enterprise and government customers.
Read moreHealthcare
Providers and health-tech companies handling patient data use ISO 27001 alongside sector-specific requirements to protect sensitive health information.
Read moreTelecommunications
Companies operating within TRA’s regulatory scope use ISO 27001 to demonstrate structured cybersecurity readiness.
Read moreProfessional and Legal Services
Firms handling confidential client data increasingly need demonstrable information security management alongside professional confidentiality obligations.
Read moreCase Study: A Bahrain Fintech’s Certification Journey
- The following is an illustrative, composite example based on the kind of project ShineCert typically runs, not a specific named client. A Bahrain-based fintech company processing customer financial data had strong technical security instincts, encryption, access controls, and monitoring were all reasonably solid, but no formal risk assessment methodology, no Statement of Applicability, and no documented incident response plan tested against realistic scenarios. The trigger was a partnership requirement from a regional bank that explicitly required ISO 27001 certification before integrating the fintech’s API into its systems.
- The gap assessment found the company’s actual technical controls were genuinely strong, but almost none of it was formally risk-assessed or documented in an auditable way, the security team’s institutional knowledge wasn’t captured anywhere a new hire or auditor could verify it. The bulk of implementation work went into building a genuine risk assessment methodology, formalizing the Statement of Applicability around already-strong existing controls, and building and testing a documented incident response plan. The company also mapped its existing practices against PDPL obligations during the same project, closing several genuine compliance gaps around data subject request handling that had gone unaddressed. Certification was achieved in time for the partnership integration, and the pattern we typically see afterward held: the formal risk assessment process surfaced two genuine, previously unidentified risks in third-party vendor access that the informal security approach had missed entirely.
Mandatory Documents Required for Certification
Genuine leadership commitment specific to your organization.
Documented, defining exactly which systems, data, and locations are covered.
Reflecting your actual threat landscape, not a generic template.
Documenting which of the 93 Annex A controls apply, with justification for exclusions.
Mapped to PDPL and, where relevant, CBB Module TC obligations.
Evidence of genuine, ongoing oversight.
Why ShineCert?
We coordinate Bahrain engagements from ShineCert’s Riyadh and Lebanon offices, with direct familiarity with PDPL, PDPA enforcement practice, CBB Module TC, and Tamkeen’s funding programs. Our team has guided more than 10,000 organizations through ISO certification globally, with ShineCert as the best ISO 27001 consultant in Bahrain, building every Bahrain information security engagement around your actual data environment, regulatory exposure, and funding eligibility, not a one-size-fits-all package.
Choosing a Certification Body in Bahrain?
What to Check | Why It Matters |
Accreditation under the GAC framework | Confirms genuine, internationally recognized certification |
Experience with CBB-regulated financial institutions | Ensures the auditor understands Module TC’s specific technology-controls expectations |
Familiarity with PDPL and PDPA enforcement practice | Helps ensure your ISMS genuinely supports broader data protection compliance |
Sector-specific audit experience | Fintech, healthcare, and telecom each involve meaningfully different risk profiles |
Ready to Get Certified?
ShineCert supports Bahrain businesses from initial gap assessment through certification audit, including checking whether your project qualifies for Tamkeen funding support. Book a free consultation or contact us directly, and we’ll walk through your specific data environment and cost factors before proposing a fixed-scope plan.
Frequently Asked Questions
It’s the international standard for information security management systems, setting requirements for identifying, controlling, and continually improving how an organization protects information.
It genuinely depends on factors like data sensitivity, number of systems, regulatory overlay, and existing security maturity, we scope every project individually.
Not automatically, it provides a strong technical foundation for PDPL compliance, but PDPL-specific requirements like consent management need dedicated attention beyond ISO 27001’s information security scope.
Not as a blanket mandate, but it directly supports Module TC’s technology-controls requirements for licensed financial institutions.
Typically three to five months.
Potentially, Tamkeen’s training and development programs can apply to certification-related costs depending on eligibility.
Annex A was restructured from 114 controls across 14 domains to 93 controls across four themes, with new controls added for threat intelligence, cloud security, and data masking.
A required document listing which of the 93 Annex A controls your organization applies, with justification for any that are excluded, based on your genuine risk assessment.
Yes, each system or application in scope needs its own risk assessment and applicable controls.
We coordinate Bahrain engagements from our Riyadh and Lebanon offices, with consultants traveling on-site as needed.