
ISO 42001 Certification in Kenya
Quick Answer
ISO 42001 is the international standard for artificial intelligence management systems, and Kenya’s AI governance landscape is moving from strategy toward genuine legislation faster than most African markets: the Kenya Artificial Intelligence Strategy 2025-2030, launched in March 2025 under the Ministry of Information, Communications and the Digital Economy, is now being followed by the Artificial Intelligence Bill 2026, which proposes a standalone statutory framework built around a dedicated AI Commissioner. ISO 42001 gives Kenyan organizations building or deploying AI systems a structured, internationally recognized way to demonstrate responsible AI practice ahead of this legislation taking effect. Certification typically takes three to five months, and cost depends on real factors like the scale and risk profile of your AI systems, never a flat number quoted upfront.
Understanding ISO 42001
ISO 42001 is an international standard, published by the International Organization for Standardization, that sets out requirements for an artificial intelligence management system, a structured way an organization governs the development, deployment, and ongoing operation of AI systems responsibly. It’s the first international management system standard specifically for AI, covering AI risk assessment, data governance, transparency, and human oversight, whether your organization builds AI models directly or deploys and integrates third-party AI tools. Certification means an independent, accredited body has formally verified your AI governance practices meet the standard’s requirements, giving customers, regulators, and partners genuine confidence your organization manages AI risk systematically, not just as a marketing claim.
Why It’s Becoming Essential for Kenyan Businesses Right Now?
- Kenya’s AI governance framework is moving from strategy to genuine legislation, faster than most comparable markets : The Kenya Artificial Intelligence Strategy 2025-2030 set out six pillars, Digital Government, Digital Business, Infrastructure, Innovation and Entrepreneurship, Digital Skills and Values, and Digital Inclusion, and has since been followed by the Artificial Intelligence Bill 2026, which proposes a standalone statutory framework with a dedicated AI Commissioner responsible for risk assessments, policy development, and public AI literacy. Organizations building genuine AI governance capability now are aligning directly with where Kenyan law is explicitly heading.
- The proposed governance structure explicitly links AI oversight to existing regulators you may already deal with : The Strategy’s governance architecture gives the Office of the Data Protection Commissioner a formal role on data privacy alignment and the Communications Authority’s KE-CIRT a formal role on cybersecurity and incident response, meaning AI governance in Kenya won’t sit in a regulatory vacuum but will connect directly to bodies already actively enforcing data protection and cybersecurity obligations.
- Kenya’s fast-growing fintech, agritech, and healthtech sectors are deploying AI faster than most organizations’ internal governance maturity : As Kenyan businesses integrate AI into credit scoring, agricultural forecasting, and health diagnostics support, the genuine risk of biased outcomes or unexplainable automated decisions grows faster than most organizations’ informal governance can keep pace with, precisely the gap ISO 42001 is built to close.
- International investors and enterprise clients increasingly ask genuine AI governance questions, not just AI capability questions : Kenyan AI-driven businesses seeking international investment or enterprise partnerships increasingly encounter due-diligence questions about how AI risk and data use are actually managed, questions a certified management system answers with independently verified evidence rather than a policy statement alone.
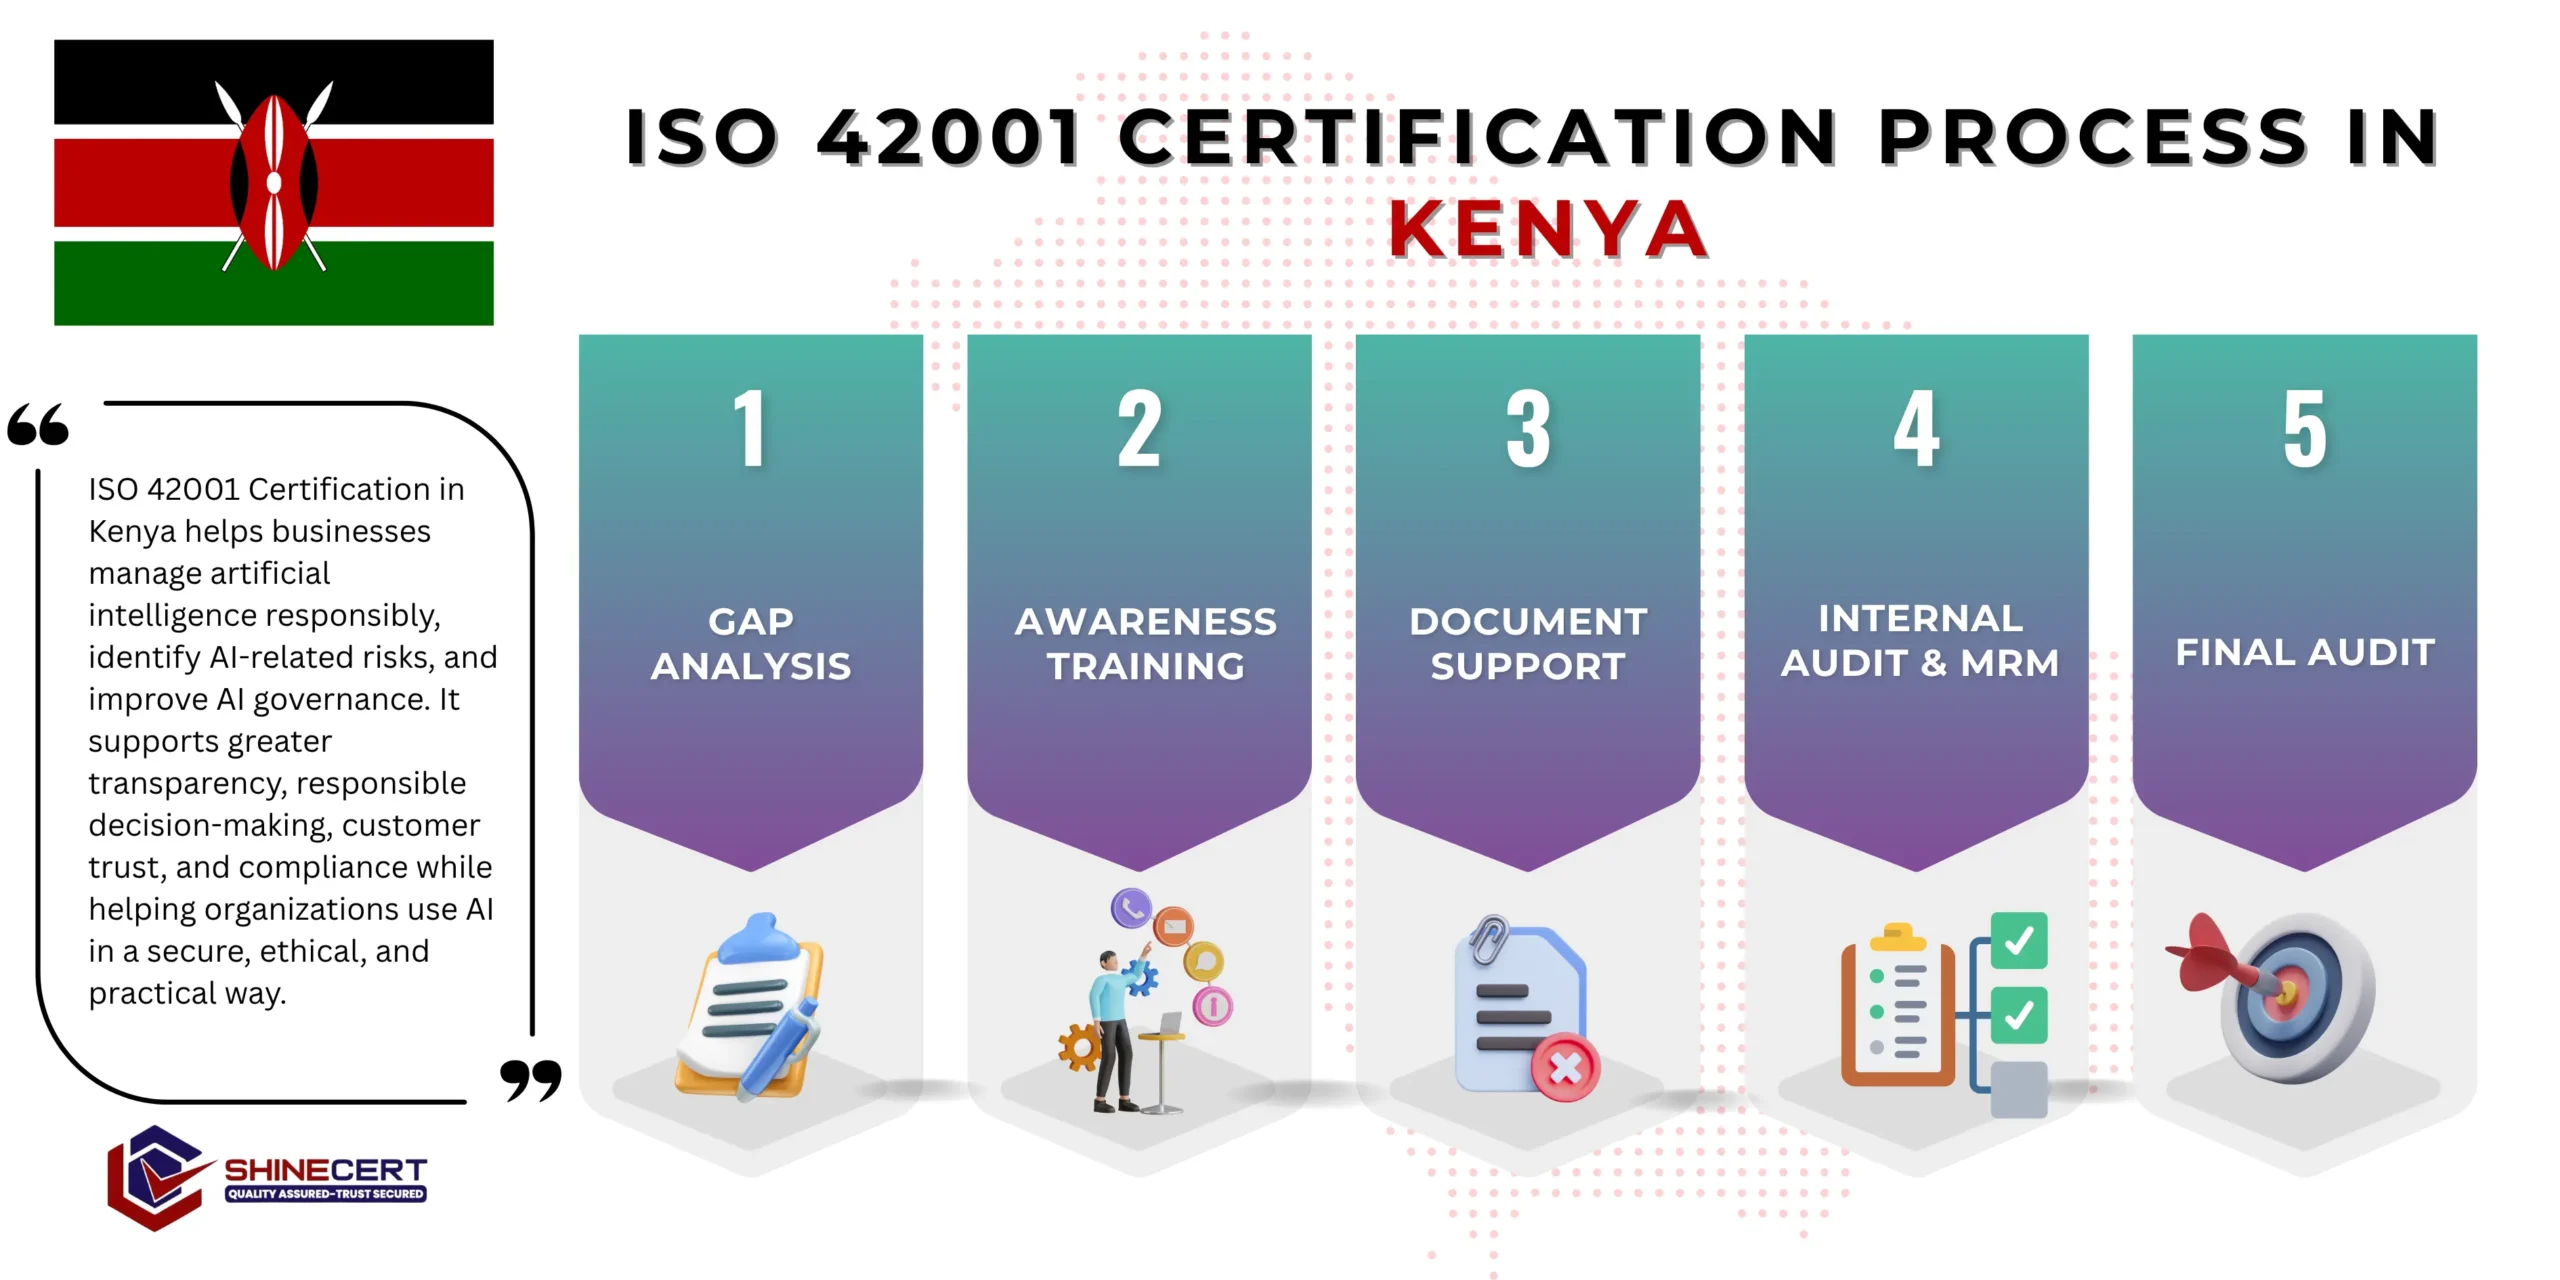
What are the steps to get ISO 42001 Certification in Kenya?
our services
- ISO Certification Kenya
- ISO 9001 Certification Kenya
- ISO 14001 Certification Kenya
- ISO 27001 Certification Kenya
- ISO 22000 Certification Kenya
- ISO 27701 Certification Kenya
- ISO 45001 Certification Kenya
- ISO 20000-1 Certification Kenya
- ISO 13485 Certification Kenya
- ISO 17025 Certification Kenya
- ISO 31000 Certification Kenya
- ISO 42001 Certification Kenya
- ISO 37001 Certification Kenya
- ISO 22301 Certification Kenya
- ISO 50001 Certification Kenya
- CE Mark Certification Kenya
- GDPR Certification Kenya
- GMP Certification Kenya
- Halal Certification Kenya
ISO 42001 Certification Process in Kenya
Gap Assessment
We review your actual AI systems, whether internally developed models or integrated third-party tools, and current governance practices, mapping what we find against ISO 42001’s requirements and Kenya’s AI Strategy direction together.
A gap report identifying your real AI risk profile and where formal governance documentation is missing.
Documentation
We build your AI policy, risk and impact assessment methodology, and system inventory around your organization’s genuine AI use cases, a fintech using AI for credit scoring has a meaningfully different risk profile than a business using AI for internal document processing.
A complete AI governance documentation set, with human oversight requirements genuinely built in for higher-stakes use cases.
Implementation
Governance controls, data quality checks, human review checkpoints, incident response, move into real practice around how your AI systems are actually built and monitored.
A functioning AI management system with genuine oversight actively operating.
Internal Audit and Management Review
We audit against every ISO 42001 clause, surfacing gaps while stakes are low. Findings go to formal management review with documented decisions.
An internal audit report and corrective actions closed out before the certification audit.
Certification Audit
Stage 1 confirms your AI governance documentation is genuinely audit-ready; Stage 2 verifies governance controls are actually operating around your real AI systems. We stay engaged through both stages.
Your ISO 42001 certificate, valid for three years, plus a surveillance audit schedule.
Staying Certified: Surveillance and Renewal
An ISO 42001 certificate is valid for three years. During years one and two, your certification body conducts an annual surveillance audit, sampling part of your AI systems and governance controls. Before the three-year mark, a full recertification audit confirms your AI management system has continued functioning as your AI systems and use cases evolved. Passing recertification issues a new three-year certificate.
ISO 42001 Certification Cost in Kenya
| Business Profile | Relative Investment Level | Why |
|---|---|---|
| Small, single-system operation | Lower | Narrower asset inventory, fewer applicable controls |
| Medium, multiple-systems operation | Moderate | Broader risk assessment and control implementation scope |
| Larger, multi-department operation with sensitive data | Higher | Extensive systems mapping and complex access management |
| Bundled with a second standard | Moderate-to-higher combined, lower than separate engagements | Shared implementation infrastructure reduces combined cost |
There’s no flat price for ISO 42001 certification in Kenya. Cost genuinely comes down to six factors:
- Nature and stakes of your AI use cases : AI used for credit scoring or health recommendations carries genuinely higher governance requirements than AI used for internal process automation.
- Number of distinct AI systems : Each additional AI system or use case expands the inventory and risk assessment work required.
- Whether AI is built internally or sourced from third parties : Internally developed models require deeper technical documentation; third-party tools require genuine vendor risk assessment instead.
- Existing governance maturity : Businesses with some documented AI use policies already in place aren’t starting from zero.
- Certification body fees, tracked separately from our consulting fees : The certification audit itself is invoiced directly by the accredited certification body.
- Whether you’re bundling standards : Building ISO 42001 alongside ISO 27001 shares meaningful risk assessment infrastructure, reducing combined cost.
Benefits of ISO 42001 Certification for Kenyan Organizations
Kenyan organizations that complete certification gain considerably more than a document proving AI governance. Here is what certified businesses genuinely gain:
Because both the National AI Strategy and the proposed AI Bill 2026 explicitly prioritize responsible governance, certified organizations are demonstrably ahead of where Kenyan policy and law are heading.
ISO 42001 is understood and trusted globally as evidence of genuine AI governance maturity, particularly valuable for Kenyan AI businesses seeking international clients or investment.
Systematic risk assessment covering bias, data quality, and unintended AI outcomes catches genuine problems before they reach customers or trigger reputational harm.
A certified system positions your organization to adapt considerably faster once the AI Bill 2026’s oversight structure, including the proposed AI Commissioner, becomes operational.
International investors and enterprise clients increasingly weigh AI governance credentials when evaluating Kenyan AI-driven businesses.
ISO 42001 requires assigning genuine ownership for AI risk decisions, replacing the common pattern of AI development moving fast with no one formally accountable for downstream effects.
The standard requires genuine scrutiny of data used to train and operate AI systems, directly relevant given the ODPC’s already-active enforcement role in Kenya’s data protection regime.
ISO 42001 requires genuinely identifying the specific risks your actual AI systems pose and building real, documented controls around each one.
Organizations already certified to ISO 27001 find ISO 42001 shares meaningful structural overlap, particularly around risk assessment and data governance.
A Kenyan Business We’ve Worked With
- A Nairobi-based agritech platform offering AI-driven crop yield forecasting for smallholder farmers approached us after an international development partner’s due diligence process asked specific questions about how the platform validated its forecasting model and managed the risk of inaccurate predictions affecting farmer planting decisions.
- Our gap assessment found the underlying model had been built with genuine care, including informal accuracy testing during development, but there was no formal AI risk assessment, no documented process for farmers to flag inaccurate predictions, and no structured way to demonstrate any of this to an outside party.
- We built the AI management system directly around their existing model and farmer engagement workflow, adding a structured feedback loop for flagged predictions and documenting the accuracy testing methodology the team had already been informally applying.
- Certification took just over four months, and the resulting documentation became a direct, positive input into the partner’s due diligence process.
- This reflects a pattern we see often, genuinely careful AI development undermined by a lack of documented, demonstrable governance, rather than a single specific engagement.
Where Certification Matters Most Across Kenya’s Economy?
Fintech and digital lending
ISO 42001 addresses genuine AI-driven credit scoring risk; pair with ISO 27001 given the sensitive financial data involved.
Read moreAgritech
ISO 42001 addresses AI-driven forecasting and advisory tool risk relevant to Kenya’s agricultural economy; pair with ISO 9001 for service quality.
Read moreHealthtech
ISO 42001 addresses AI-assisted diagnostic risk; pair with ISO 27001 given sensitive health data.
Read moreInsurtech
ISO 42001 addresses AI-driven underwriting risk; pair with ISO 27001 for the personal data involved.
Read moreHR technology and recruitment platforms
ISO 42001 addresses genuine bias risk in AI-driven hiring tools; pair with ISO 27001 for personal data protection.
Read moreTelecommunications and customer analytics
ISO 42001 addresses AI-driven profiling risk; pair with ISO 27001 for underlying data protection.
Read moreRealistic Timelines for Kenyan Businesses
| Business Profile | Typical Total Timeline | What Drives This |
|---|---|---|
| Small, single AI use case | 2.5–3.5 months | Narrower system inventory and simpler risk landscape |
| Medium, multiple AI use cases | 3.5–5.5 months | Broader risk assessment across more AI systems |
| Larger, high-stakes AI deployment (fintech credit scoring, healthtech) | 5.5–8 months | Extensive impact assessment and human oversight design |
| Bundled with ISO 27001 | Add roughly 3-5 weeks to the relevant tier above | Shared risk assessment infrastructure meaningfully shortens the combined path |
Beyond organization size, the single biggest timeline driver is how many distinct AI use cases your organization has and how high-stakes their outcomes are.
The Documentation Auditors Expect
A documented statement defining which AI systems, use cases, and business units the management system covers.
A documented policy, approved by top management, expressing genuine commitment to responsible AI development and use.
A documented, actively maintained process for identifying risks specific to your actual AI systems, including impact on individuals affected by automated decisions.
Records showing how training and operational data is sourced, quality-checked, and managed, addressing genuine data quality and bias risk at the source.
A documented register of AI systems in use, including their intended purpose, scope of deployment, and assigned ownership.
Documentation defining where and how human review is genuinely built into AI-driven decisions, particularly for higher-stakes use cases like lending or hiring.
Documentation assessing risk where your organization relies on external AI tools or vendors.
A documented procedure for detecting and responding to AI-related incidents, biased outcomes, system malfunctions, unintended consequences.
A planned internal audit cycle and documented management review decisions on AI governance priorities and resourcing.
The Real Challenges Organizations Face While Implementing ISO 42001
- Viewing governance as a brake on innovation : Technical teams sometimes view AI governance documentation as slowing down genuine innovation, when in practice a well-scoped system formalizes decisions the team was already making informally.
- Assessing risk only at initial deployment : A common gap is assessing AI risk only when a model first launches, without genuinely revisiting it as the model is retrained or its use case expands into higher-stakes decisions.
- Human oversight that exists on paper only : Auditors specifically probe how genuine your human oversight actually is, a “human in the loop” review step that’s routinely rubber-stamped without real scrutiny is a common gap.
- Governance documentation falling behind fast-moving AI development : AI systems evolve faster than most other business systems, and governance documentation can quickly fall out of date if new use cases aren’t genuinely fed back into the risk assessment.
Why Businesses Choose ShineCert in Kenya?
ShineCert brings 10 years of ISO consulting and certification experience to Kenya’s market, coordinated through our Riyadh and India offices with services delivered remotely or on-site depending on what your engagement genuinely needs. We’ve guided more than 10,000 organizations through ISO certification worldwide, and we build every Kenya AI governance engagement around your actual AI systems and risk profile, this is why AI-driven Kenyan businesses increasingly choose ShineCert as the best ISO 42001 consultant in Kenya.
Choosing a Certification Body in Kenya?
What to Check | Why It Matters |
Accreditation under a recognized international accreditation framework | Confirms genuine, internationally recognized certification |
Genuine understanding of AI-specific risk, not just general IT audit experience | ISO 42001 requires assessing bias, transparency, and human oversight, not just data security |
Experience with your specific AI use case’s risk profile | Credit scoring, diagnostics, and forecasting carry genuinely different risk considerations |
Familiarity with Kenya’s AI Strategy and proposed AI Bill 2026 | Ensures the auditor understands the governance context your organization operates within |
Start Your Certification Journey
Whether you’re building AI governance proactively or responding to investor due diligence, we’ll walk through your specific AI systems and cost factors before proposing a fixed-scope plan, delivered remotely, on-site, or however genuinely fits your project. Book a free consultation or contact us directly to get started.
Frequently Asked Questions
Look for genuine AI-specific risk assessment experience and familiarity with Kenya’s AI Strategy and proposed AI Bill 2026, and transparent scoping rather than flat package pricing. ShineCert scopes every Kenya engagement individually.
Not yet as a binding requirement, but Kenya’s National AI Strategy and the proposed Artificial Intelligence Bill 2026 explicitly prioritize responsible governance, meaning certified organizations are positioned ahead of where Kenyan law is genuinely heading.
It genuinely depends on the number and risk level of your AI use cases, we scope every project individually.
Typically two and a half to eight months depending on the scale and risk profile of your AI systems, see our detailed timeline breakdown above.
Yes, ISO 42001 covers both internally developed AI systems and third-party AI tools your organization deploys.
A certified AI management system positions your organization to adapt considerably faster to any new oversight structure than one starting from no formal governance.
Much of the documentation and risk assessment work runs effectively over remote sessions, though certain reviews benefit from in-person discussion with your technical team.
ShineCert doesn’t maintain a standalone Kenya office; we coordinate Kenya engagements from our Riyadh and India offices, with services delivered remotely or on-site as your project requires.